



Pinned Tweet
1 Hour with @PatrickAlphaC where I cover:
1⃣ how I break down stateful fuzz testing by invariant types and contract lifecycle
2⃣ my favorite general heuristics which I use to find all sorts of bugs in many different codebases
3⃣ mindset and ultimate recipe for success
Link👇
Dacian retweeted

Our crowdfund has reached $417k from 69 participants!
We’re well on our way to hitting our $1M target before it closes on 29th October. If we don't hit it, every commitment is returned in full.
Need an invite? DM us.
Have one? Commit USDC at fund.armada.blue
Dacian retweeted

Our frontend audit with @cyfrin is complete.
No critical or high findings, and all 7 medium findings resolved.
Report: gitlab.com/notesystems/note-…
Our backend audit is in progress. Across 75 smart contracts, no high or critical issues found.
Mainnet is getting closer.


3yr speedrun auditor -> executive, ask me anything

October 2022 - started learning solidity as a hobby
March 2023 - focusing on security & began writing my "Deep Dive" series
October 2023 - blessed to join @cyfrin as a full-time smart contract security researcher!
🚀A lot can change in a year if you put your mind to it🚀
Dacian retweeted

Your audit report covers the code you gave us. Here's the list of things that can still drain you.

My X feed has recently degenerated into:
🥇 thirst traps (especially from token2049)
🥈 plague scenarios/theories/doom
🥉 various war/conflict stuff
I don't like any of these posts but X keeps showing them, is there really nothing else more interesting ?
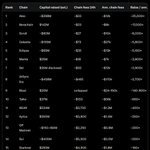
Who is the next Blast according to @grok ?
Last few years saw huge VC alt-chain "gold-rush" but how many alt-chains are generating decent revenue relative to their total raised capital?
xitter.cf/i/grok/share/44b4537c6…

I've pushed significant updates to coldclone, a very useful tool for sanitizing foreign repos before engaging with them.
If you're an auditor doing a lot of quoting or a dev downloading new repos to use, running this first is a no-brainer github.com/devdacian/coldclo…

Dacian retweeted

Cyfrin is officially part of the AvengerDAO Security Marketplace🛡️
BNB Chain is home to millions of users, and every protocol launching there deserves a security review that matches the stakes.
We're here to help @BNBCHAIN teams ship with confidence through private audits from our best-in-class security researchers.
Find us on the marketplace: avengerdao.org/marketplace

More security support, less friction for builders.
6 new security firms just joined the AvengerDAO Security Marketplace, bringing the total to 17:
→ @QuillAudits_AI
→ @cyfrin
→ @asymmetric_re
→ @MixBytes
→ @ConsensysAudits
→ @PashovAuditGrp
From development to launch and beyond, builders can compare services, contact firms directly, or ask the AvengerDAO admin team where to start.
Explore the marketplace 👇
avengerdao.org/marketplace
