

Our REFLEX platform automates the detection lifecycle—building, testing, validating and deploying detections in minutes, not months.
Seattle
Joined June 2023
- Tweets111
- Following157
- Followers22
- Likes18
Detecteam retweeted

🚨 Hackers Built a Windows Backdoor Whose Entire C2 Lives Inside Microsoft 365
Source: cybersecuritynews.com/hacker…
Hackers have built a Windows backdoor that uses Microsoft 365 for all its native command-and-control communications.
Named Antino, the malware turns Outlook messages and OneDrive files into channels for issuing instructions, moving stolen data, and maintaining access to compromised computers.
Attackers used carefully tailored phishing emails, convincing documents, and fake software installers to deliver the backdoor, combining familiar interfaces with cloud services that organizations routinely trust.
#cybersecuritynews

Detecteam retweeted
‼️ Multiple OpenSSL Flaws Let Remote Attackers Crash Servers and Corrupt Heap Memory
More Details: cybersecuritynews.com/chrome…
OpenSSL has issued a fresh security advisory disclosing seven vulnerabilities across its cryptographic library, ranging from a heap-corrupting write bug to memory-exhaustion flaws in its QUIC and DTLS implementations.
The flaws affect widely deployed branches, including OpenSSL 4.0, 3.6, 3.5, 3.4, and 3.0, and, in some cases, the legacy 1.1.1 line, making patching a priority for any organization running TLS, CMS, or CMP services built on the library.
The most severe issue, tracked as CVE-2026-63072, lives in OpenSSL’s CMS decryption code.
#cybersecuritynews

ALT Multiple OpenSSL Flaws Let Remote Attackers Crash Servers and Corrupt Heap Memory
Detecteam retweeted
🚨 Fortinet just dropped patches for 8 vulnerabilities — and two of them let attackers walk right in with random passwords. Patch FortiWeb & FortiManager NOW before threat actors do.
More Details: cybersecuritynews.com/fortin…
#cybersecuritynews

ALT Fortinet Patches Multiple Authentication Vulnerabilities in FortiWeb, FortiManager, and FortiClient
Detecteam retweeted

FULL REMOTE CODE EXECUTION on default nginx 1.30.0 no config changes needed. 🫠
Verichains a deadly exploit chain combining Nginx-Rift (CVE-2026-42945) + Nginx-PoolSlip (CVE-2026-9256).
2-byte heap pointer overwrite & heap over-read then ASLR bypass to arbitrary command execution via system() on connection teardown.

Over the next few months, we'll be gradually publishing some of our internal security research.
Starting with a bug chain that turns Nginx-Rift + Nginx-PoolSlip into full RCE.
More to come.
#Nginx #1day #RCE
blog.verichains.io/p/two-byt…

Detecteam retweeted
🚨 New 7-Zip Flaws Let Attackers Execute Arbitrary Code and Compromise Systems
Source: cybersecuritynews.com/7-zip-…
A critical heap buffer overflow vulnerability has been disclosed in 7-Zip version 26.00, enabling attackers to achieve arbitrary code execution via a vtable hijack by exploiting a defect in the tool's NTFS archive handler.
Tracked as CVE-2026-48095 and assigned advisory GHSL-2026-140, the flaw resides in the CInStream::GetCuSize() function inside NtfsHandler.cpp. The function computes the NTFS compression-unit buffer size using a 32-bit shift operation: (UInt32)1 << (BlockSizeLog + CompressionUnit).
Users are strongly advised to update 7-Zip to a patched version v26.01 immediately and avoid opening untrusted archive files or disk images of any extension until a fix is applied.
#cybersecuritynews

Detecteam retweeted

hackers are now hiding malicious code inside .cursorrules and CLAUDE.md files.
invisible Unicode characters, your AI reads them, you don't.
→ 34 malicious packages across npm, PyPI and Crates .io
→ 384 versions designed to steal SSH keys, crypto wallets, and API tokens
→ attackers opened real PRs to LangChain, LlamaIndex, and MetaGPT to sneak these files in
→ your AI runs a fake "security scan" that silently exfiltrates everything
Socket detected it in under 6 minutes.
check your repos.
Detecteam retweeted

Microsoft Defender detected and protected customers against a new software supply chain compromise affecting the "pytorch-lightning" package and immediately reported the issue to the repository maintainers for takedown: msft.it/6013vJisb.
At the time the compromised packages were identified and distributed, Microsoft Defender had proactive detections that blocked the malicious files as Trojan:JS/ShaiWorm.DQ!MTB. For protected environments, Microsoft Defender for Endpoint raised the alert "ShaiWorm malware was prevented".
Our assessment indicates that Microsoft continues to provide strong protection coverage and has prevented observed activity indicating attempts to install the modified packages. Microsoft Defender continues to monitor for potential follow-on activity, including suspicious use of potentially exposed cloud credentials across major cloud platforms.
Observed activity remains limited to a small number of devices and appear contained to a narrow set of environments. We are also investigating container-based telemetry and registry-related signals that may indicate potential compromise in some scenarios.
Microsoft continues to monitor and investigate the issue, with layered protections, broad prevention coverage, and ongoing hunting efforts in place. We will share updates as more information becomes available.

Detecteam retweeted
⚠️ Critical Wireshark Flaws Let Attackers Execute Arbitrary Code Via Malformed Packets
Source: cybersecuritynews.com/wiresh…
Wireshark, the world's most widely used open-source network protocol analyzer, has released a major security update addressing over 40 vulnerabilities, several of which enable arbitrary code execution through malformed packet injection or malicious capture files.
Organizations and individuals relying on Wireshark for network monitoring, forensics, and traffic analysis should update immediately to Wireshark 4.6.5. The most severe vulnerabilities in this release carry the potential for remote code execution (RCE), moving beyond simple denial-of-service impact.
#cybersecuritynews #wireshark

Detecteam retweeted
🛡️ Trellix Source Code Breach - Hackers Gain Unauthorized Access to Repository
Source: cybersecuritynews.com/trelli…
Cybersecurity giant Trellix has disclosed a significant security incident involving unauthorized access to a portion of its source code repository.
The company confirmed the breach in an official statement published on its website, stating it immediately engaged leading forensic experts upon discovering the intrusion.
Source code repositories are prime targets for attackers seeking to identify exploitable vulnerabilities, embed backdoors, or conduct supply chain attacks against downstream customers.
#cybersecuritynews #Databreach

Detecteam retweeted
🚨 cPanelSniper - PoC Exploit Disclosed for cPanel Vulnerability, 44,000 Servers Compromised
Source: cybersecuritynews.com/cpanel…
A weaponized proof-of-concept (PoC) exploit framework dubbed "cPanelSniper" has been publicly released for CVE-2026-41940, a maximum-severity authentication bypass in cPanel & WHM that has already led to the compromise of tens of thousands of servers worldwide with attack activity traced as far back as late February 2026.
The Shadowserver Foundation confirmed on April 30, 2026, that 44,000 unique IP addresses were observed scanning for victims, launching exploits, or conducting brute-force attacks against their honeypot sensors.
#cybersecuritynews #vulnerability

Detecteam retweeted

🚨 cPanelSniper — CVE-2026-41940
cPanel & WHM'de CVSS 10.0 kritik auth bypass.
CRLF injection → session file poisoning → root WHM access.
Zero creds. ~70M domain affected.
4-stage chain:
→ preauth session mint
→ CRLF inject via Authorization header
→ do_token_denied gadget (raw→cache flush)
→ /json-api/version → PWNED
✅ Interactive WHM shell
✅ Account enum · cmd exec · backdoor admin
✅ Bulk scan · pipeline ready · stdlib only
🔗 github.com/ynsmroztas/cPanel…
#BugBounty #InfoSec #WHM #RedTeam #AppSec #bugbountytip #bugbountytips #infosec #recon

Detecteam retweeted
⚠️ Linux Kernel 0-Day "Copy Fail" Roots Every Major Distribution Since 2017
Source: cybersecuritynews.com/linux-…
A critical zero-day vulnerability in the Linux kernel has been publicly disclosed, enabling any unprivileged local user to obtain root access on virtually every major Linux distribution shipped since 2017.
Copy Fail is a straight-line logic bug not a race condition in the Linux kernel's authencesn cryptographic template, reachable via the AF_ALG socket interface combined with the splice() system call.
A single 732-byte Python script using only standard library modules achieves deterministic root on every tested distribution and architecture.
#cybersecuritynews #linux #CopyFail

Detecteam retweeted

🚨 BREAKING: Wiz Research discovered Remote Code Execution on GitHub.com with a single git push
The flaw in @github allowed unauthorized access to millions of repositories belonging to other users and organizations 🤯

Detecteam retweeted

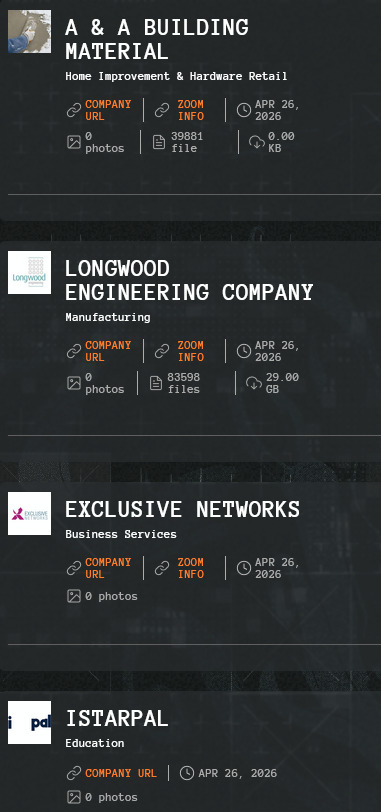
🚨 Ransomware Alert 🚨
Qilin Ransomware group has added 4 new victims to their dark web portal.
* A & A BUILDING MATERIAL CO 🇺🇸
* Longwood Engineering Company Limited 🇬🇧
* Exclusive Networks 🇫🇷
* iSTARpal 🇲🇾
Detecteam retweeted
A newly decoded piece of sabotage malware called Fast16, created before Stuxnet, was made to silently tamper with calculations in research and engineering software. Likely created by the US or an ally, and possibly used against Iran's nuclear program. wired.com/story/fast16-malwa…

Detecteam retweeted

#Lazarus C2 Control Panels & About How They Use AI to Industrialize Attacks on Developers
#AiSecurity
expel.com/blog/inside-lazaru…


Detecteam retweeted
⚠️ Windows RPC Vulnerability Lets Attackers Escalate Privileges Across All Windows Versions
Source: cybersecuritynews.com/new-wi…
PhantomRPC, a newly identified architectural vulnerability in Windows Remote Procedure Call (RPC) that enables local privilege escalation to SYSTEM-level access, potentially affecting every version of Windows. PhantomRPC is not a classic memory corruption bug or a logic flaw in a single component.
Instead, it exploits an architectural design weakness in how the Windows RPC runtime (rpcrt4.dll) handles connections to unavailable RPC servers. When a highly privileged process attempts an RPC call to a server that is offline or disabled, the RPC runtime does not verify whether the responding server is legitimate.
#cybersecuritynews #Windows

Detecteam retweeted
🚨 Hackers Abuse SS7 and Diameter Protocols to Track Mobile Users Worldwide
Source: cybersecuritynews.com/hacker…
A major investigation has revealed that sophisticated threat actors are exploiting fundamental vulnerabilities in global mobile networks to track users worldwide.
By abusing legacy 3G SS7 and 4G Diameter signaling protocols, hackers are successfully bypassing telecom firewalls to conduct silent, cross-border espionage.
By functioning as "Ghost Operators," they manipulate routing data to mask their origins while pinpointing the exact locations of high-value targets.
While the older SS7 protocol completely lacks basic authentication, the newer 4G Diameter protocol suffers from weak security implementation across the industry.
#cybersecuritynews

Detecteam retweeted
⚠️ CrowdStrike LogScale Vulnerability Allows Remote Attackers to Read Files from Server
Source: cybersecuritynews.com/crowds…
An urgent security advisory for a critical unauthenticated path-traversal vulnerability (CVE-2026-40050) affecting its LogScale platform, warning that a remote attacker could exploit the flaw to read arbitrary files directly from the server’s filesystem without authentication.
The vulnerability resides in a specific cluster API endpoint within CrowdStrike LogScale. If this endpoint is exposed, a remote attacker can leverage it to traverse the server’s directory structure and access sensitive files without needing credentials.
#cybersecuritynews

Detecteam retweeted
#Sandworm group leverages nested SSH-TOR tunnels to build a double-encrypted anonymous direct elevator between victims and attackers.
This highly evasive attack enables unrestricted sensitive data theft and persistent remote control.
mp.weixin.qq.com/s/nJpqvXCYV…


#Sandworm Targeted RDP Backdoor Campaign (2024-2026)
The group has fully evolved its operational strategy from high-impact instantaneous system destruction to intelligence-driven, long-term stealthy persistence.
The campaign leverages a highly modular, iterated attack framework (Tambur/Sumbur/Kalambur/DemiMur) targeting global defense industry, critical infrastructure, and government entities.
mp.weixin.qq.com/s/QWe2m4qdp…

