






Pinned Tweet
on compliance impossibility:
now that folks are focused on compliance because they are afraid of facilitating terrorism xfers....lets look at how it's not possible for the types of systems people want
@BenCharoenwong posted our preprint last week
papers.ssrn.com/sol3/papers.…
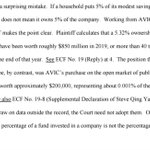
@circle claims of incompetence place it in a tight bind.
Either Circle is misleading a court is Wisconsin or
Circle’s public docs are v v wrong
Both are bad
chainargos.com/cant-seize-or…

And there is an excellent ICIJ piece which is kinder to all involved.
xitter.cf/ICIJorg/status/2081726…

Circle pitches its USDC token as the new face of finance. But some officials have begun to raise alarms about instances of the crypto giant denying law enforcement requests to freeze assets and allegedly refusing to help recover scam victim funds. bit.ly/4bLRrn9

it looks as though circle did facilitate the seizure which calls into question all the arguments circle made quoted above
tx link and screenshot of disposition of seizure case. obv possible its a different 381235 depo'ed straight to circle but hmmm.
etherscan.io/tx/0x23e7771613…

what's funny in the "is thorchain open source" debate is that both sides are not being honest.
yes thorchain routinely develops non-public code. is this bad? obv. is there proof? obv.
but do they keep this secret for long periods? no.
hysteria is not the answer! the truth is.

if you want to claim any project with a security embargo policy is closed-source then you don't know how any of this works.
if you want to claim the thorchain team is not v good at security and their policy is not perfect: nobody is going to argue that!
were not defending thorchain. weve published detailed proof of thorchain's past misrepresentations going through the code in detail.
but it is important to be honest and accurate about how thorchain works.
lying in both directions is bad.
medium.com/chainargos/hammer…

this is clearly true as a matter of law +/- everywhere. joint custody schemes don't magically dissolve liability.
it is, however, also poisonous to many designs to admit this truth. and its suicide for many real products to admit this truth.

I don’t think THORChain’s TSS + validator model represents true decentralization.
The selected validators set collectively controls the underlying assets in the TSS vaults. Once the signing threshold is reached, those validators can move the funds. So from a custody perspective, THORChain is not comparable to Bitcoin or Ethereum base-layer consensus — it effectively acts as an intermediary between users and the native chains.
TSS distributes control among multiple parties, but distributing an intermediary does not eliminate the intermediary.
The choices now are:
A-publish your full proof and litigate if you were sleazy or not
or
B-dont and have everyone assume youre sleazy and a liar
If the leaked correspondence is fake then publish and litigate that. Nobody believes this is the case tho.

A series of false and inflammatory allegations against me are currently circulating on social channels. To clarify, I came into the discussion following academic norms, and I'm disappointed that it has come to this. Anyone who knows me knows that academic standards are of the highest importance to me. Will have more to say tomorrow.
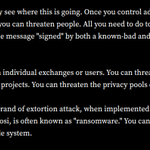
bit of a toyota 2001 moment on this one. my 2023 column talked about extorting automated provenance checks in this way.
unsurprisingly: yes it works. you can impose huge costs from a distance to try to get what you want.


Bloomberg: Kraken Hit by ‘Dust Attack’ as Nearly 12,000 HTX-Linked Transfers Trigger Compliance Reviews
Bloomberg reported that Kraken said some customers were temporarily locked out after receiving small crypto transfers from a wallet identified by Arkham Intelligence as linked to HTX. Kraken described the activity as a “dust attack,” saying it may have been intended to spread sanctioned funds and trigger compliance reviews at other platforms.
From Aug. 17 to 24, the wallet sent nearly 12,000 small transfers to Kraken-linked addresses, mostly worth only a few cents or dollars. Kraken has restored access to affected accounts while continuing to hold the sanctioned funds. HTX denied initiating the transfers and said it is investigating possible address misattribution or malicious third-party activity.


"it is not our proudest product placement, but it shows that sun is looking for the same qualities as anyone else with a pile of tokens and an axe to grind."
as always: h/t wade hoyt, the greatest corporate comms person in history
nytimes.com/2001/11/23/autom…

amazing hypocrisy. here is @RebeccaRettig1 agreeing, on camera at a government event, that automated systems can be "perfect" regulators
now the claim is reliance on well-meaning tools is sufficient to ensure legal liability doesnt attach
what changed?
youtu.be/kl7omhTtERE?si=8mV0…

1/ Today, @m_mosier_ @malekanoms & I are sharing a new paper: "The Compatibility of Financial Integrity With Permissionless Networks". Institutions say BSA & sanctions laws prevent use of these networks. We debunk this & provide a path forward. 🧵 papers.ssrn.com/sol3/papers.…
the real crime here is that bottle of drc echezeaux in an ice bucket and served in a champagne glass
i strongly hope the wine is fake. luckily i also expect it is fake. anyway pls extradite this person to france where this behaviour is a capital crime
This quoted post is unavailable.
The delta wifi "incident" is just ridiculous. Every smartphone can do hotspot and it's harmless to the plane.
Or says thats wrong and hotspot is dangerous. You cant check lithium batteries so i guess you cant fly with phones.
The ignorance is amazing
cbsnews.com/atlanta/news/pos…


Real attackers plan to and do route transactions through services to slow tracing.
We see this in real attacks.
This is why attackers escape. The blacklisters surely know this. The ByBit hack is a great example too.

The good news: attackers persistently escaping is not (entirely) a result of ecosystem slowness or bad tooling or incompetence or anything like that.
The bad news: fixing it requires compromising on core principles.


Why and how blacklist-based compliance fails: a new paper.
We study how retrospective blacklisting fails. And present a model for why this is inevitable.
Forthcoming IEEE BCCA 2026:
papers.ssrn.com/sol3/papers.…
