

CMO @SALUS_sec /Co-Founder @flashrescue 没有完美的犯罪 被盗,被骗资产救援紧急联系方式 tg:DarcyAri
Tukwila, WA
Joined March 2024
- Tweets2.5K
- Following1.7K
- Followers5.9K
- Likes6.8K



Darcy 资产救援⛑️ retweeted
十月十一日,一名自媒体博主收到高薪商业拍摄邀约。对方提前支付定金取得信任,随后诱其前往泰国。抵达后,受害人被带至一处偏僻房屋,面临被转手出售的风险
受害人察觉异常后,及时联系亲友,并装病拖延时间。据其描述,拟接手人员因受害人病情对约定价格提出异议,双方发生争执,交易暂时中止,为救援争取了时间
接到亲友求助后,我们协同警方,结合涉事人员的电话线索、受害人沿途拍摄的照片和一张外卖照片,锁定其位置,最终协助其获救
警方随后将涉事人员带回调查,并继续核查其出入境记录、边境地区行程及是否涉及非正规越境,相关情况仍在调查中
泰缅跨境转运时间窗口极短,一旦出境救援非常困难。境外工作邀约即使提供定金,也应核实雇主、工作地点和接洽人员


On October 11, a content creator received a lucrative offer for a commercial shoot. The organizers paid a deposit upfront to gain their trust, then lured them to Thailand. Upon arrival, the victim was taken to an isolated house, where they faced the risk of being sold to another party
Realizing something was wrong, the victim contacted family and friends and feigned illness to buy time. According to the victim, the prospective buyers disputed the agreed price because of their apparent illness. An argument broke out, temporarily halting the transaction and buying crucial time for rescue. After receiving a request for help from the victim’s family and friends, we worked with police to pinpoint their location using phone-related leads concerning those involved, photographs the victim had taken along the journey, and a photograph of a food delivery order. We ultimately helped secure the victim’s rescue
Police subsequently took those involved in for questioning and continued examining their immigration records, travel in border areas, and possible involvement in irregular border crossings. The investigation remains ongoing
The window for intervention before victims are transferred across the Thai–Myanmar border is extremely narrow. Once they have been taken across, rescue becomes very difficult. Even when an overseas job offer includes an upfront deposit, verify the employer, the actual work location, and the people arranging the engagement


Darcy 资产救援⛑️ retweeted

大家好,我们做了一款真正安全、超轻量、AI Native 的指纹浏览器 —@exfing_browser
我们的 ExFing 指纹浏览器 内测正式上线了!
💡 我们为什么要自己做一款指纹浏览器?
市面上流行的几款指纹浏览器屡次发生被黑客攻击、用户资产遭受不可挽回损失的事件。这说明很多厂商并没有把“安全稳定”作为产品的底层基因。 我个人在浏览器安全领域深耕多年,专注漏洞挖掘与安全风险研究。ExFing 的初衷,就是站在“攻击者”视角做最严苛的安全防护,从底层扼杀潜在攻击,打造真正安全可靠的运行环境。
⚡ 摒弃重量级框架,极致轻便与低资源占用 相信很多多开用户都深受“卡顿、内存吃紧”的困扰。相比其他同行,ExFing 并没有采用传统的 React 模式,彻底告别冗余开销。产品整体架构极度轻便,CPU与内存占用更小,运行与启动速度飞快,哪怕多开几十上百个环境依然顺滑!
🤖 拒绝伪 AI,打造真正的 AI Native 体验 现在的很多指纹浏览器只是生硬地挂个 AI 或 MCP 插件。而 ExFing 从架构之初就是 AI Native 的,旨在帮你以最高效、最自动化的方式完成账号运营工作,大幅减少繁琐的手动操作(功能很快开放!)。
🎁 内测限时福利:
完全免费:内测阶段所有高级功能全部免费开放!
不限环境与子账号:支持创建任意多个环境与子账号,无上限,放开测试!
对于内测用户,我们会在后续使用中,会有更多折扣!
🔗 立即注册下载:app.exfing.com/
🐦 关注官方推特:xitter.cf/exfing_browser
💬 加入内测反馈微信群
欢迎大家下载体验,多给我们提宝贵的 Bug 和建议!

Darcy 资产救援⛑️ retweeted

🚨警惕涉及泰国、越南等地的加密行业招聘广告
据 Web3 安全公司 @salus_sec 监测,其近期发现加密行业出现部分东南亚地区招聘广告,涉及泰国及越南等地。
若应聘者贸然前往可能存在被诱拐至缅甸的风险。
Foresight News 提醒您,前往东南亚国家需要做好充分的攻略并保持警惕,以确保人身与财产安全。


Darcy 资产救援⛑️ retweeted

⚠️据悉,这次事件当事人此前是加密从业者。
小编也提醒各位,前往泰国等地区务必警惕此类“高薪合作/拍摄”诱骗!对方先付定金也可能是圈套,务必核实雇主、实际地点与对接人员真实性,避免被带往偏远或边境区域。一旦接近泰缅边境,救援窗口极窄,难度极大。
安全第一,提高警惕!
On October 11, a content creator received a lucrative offer for a commercial shoot. The organizers paid a deposit upfront to gain their trust, then lured them to Thailand. Upon arrival, the victim was taken to an isolated house, where they faced the risk of being sold to another party
Realizing something was wrong, the victim contacted family and friends and feigned illness to buy time. According to the victim, the prospective buyers disputed the agreed price because of their apparent illness. An argument broke out, temporarily halting the transaction and buying crucial time for rescue. After receiving a request for help from the victim’s family and friends, we worked with police to pinpoint their location using phone-related leads concerning those involved, photographs the victim had taken along the journey, and a photograph of a food delivery order. We ultimately helped secure the victim’s rescue
Police subsequently took those involved in for questioning and continued examining their immigration records, travel in border areas, and possible involvement in irregular border crossings. The investigation remains ongoing
The window for intervention before victims are transferred across the Thai–Myanmar border is extremely narrow. Once they have been taken across, rescue becomes very difficult. Even when an overseas job offer includes an upfront deposit, verify the employer, the actual work location, and the people arranging the engagement
一个多世纪前,许多华人被称作“猪仔”,在诱骗与胁迫下被运往异国,从事各类高危,重体力职业,失去自由,遭受剥削
时至今日,祖国已然强大,百年前的屈辱竟再次重演,同胞被诱骗至东南亚,遭到拘禁、转卖和各种非人的待遇,更令人费解的是作案的团伙从洋人换成了华人
近期相关团伙对于受害人进行职业分析,定制化骗局,我们也关注到加密招聘社群有相关泰国的招聘信息,请谨防上当,并且建议理性拒绝华人同胞在境外提供的“好意”,在东南亚远离华人可以减少绝大多数的麻烦
我们将继续利用长期在东南亚建立的执法资源,深入调查链上相关人口贩卖地址网络,与警方及各方救援力量合作,帮助更多身陷困境的同胞重获自由,平安回家🙏

十月十一日,一名自媒体博主收到高薪商业拍摄邀约。对方提前支付定金取得信任,随后诱其前往泰国。抵达后,受害人被带至一处偏僻房屋,面临被转手出售的风险
受害人察觉异常后,及时联系亲友,并装病拖延时间。据其描述,拟接手人员因受害人病情对约定价格提出异议,双方发生争执,交易暂时中止,为救援争取了时间
接到亲友求助后,我们协同警方,结合涉事人员的电话线索、受害人沿途拍摄的照片和一张外卖照片,锁定其位置,最终协助其获救
警方随后将涉事人员带回调查,并继续核查其出入境记录、边境地区行程及是否涉及非正规越境,相关情况仍在调查中
泰缅跨境转运时间窗口极短,一旦出境救援非常困难。境外工作邀约即使提供定金,也应核实雇主、工作地点和接洽人员
On October 11, a content creator received a lucrative offer for a commercial shoot. The organizers paid a deposit upfront to gain their trust, then lured them to Thailand. Upon arrival, the victim was taken to an isolated house, where they faced the risk of being sold to another party
Realizing something was wrong, the victim contacted family and friends and feigned illness to buy time. According to the victim, the prospective buyers disputed the agreed price because of their apparent illness. An argument broke out, temporarily halting the transaction and buying crucial time for rescue. After receiving a request for help from the victim’s family and friends, we worked with police to pinpoint their location using phone-related leads concerning those involved, photographs the victim had taken along the journey, and a photograph of a food delivery order. We ultimately helped secure the victim’s rescue
Police subsequently took those involved in for questioning and continued examining their immigration records, travel in border areas, and possible involvement in irregular border crossings. The investigation remains ongoing
The window for intervention before victims are transferred across the Thai–Myanmar border is extremely narrow. Once they have been taken across, rescue becomes very difficult. Even when an overseas job offer includes an upfront deposit, verify the employer, the actual work location, and the people arranging the engagement
🚨警惕!与Fomopeek利用KOL诈骗的模式一致,@RevenueFamily 存在恶意授权,作案团伙提交用户的 permit 签名,取得无限额 USDG 使用权限,随即调用 transferFrom,授权和划款在同一笔交易里完成,将用户的钱包清空
资金随后被分为20%与80%流入两个黑客地址,这种分账结构,与至 Inferno 的盗币服务模式相似
🚨@RevenueFamily involves malicious approvals. The perpetrators submit users’ permit signatures to obtain unlimited permission to spend their USDG, then immediately call transferFrom. The approval and fund transfer are completed in the same transaction, draining users’ wallets
The funds are then split 20%/80% between two hacker addresses. This distribution structure resembles Inferno’s drainer-as-a-service model, and its promotional approach matches FomoPeek’s model of using KOLs to carry out scams

Bitget被盗案中,Circle 与 Tether 均已响应冻结:截至今日 13:00(UTC+8),Circle 已冻结约 10 万枚 USDC;今日 20:19(UTC+8),Tether 冻结 218,022.966977 枚 USDT
冻结地址:
0xe07bd590e1198666230932bad5db3dbbe21e7d57
此外,被盗 TRX 的洗转路径中仍存在窗口极短的冻结机会:
TRX → 分批兑换为 USDT → 经 Stargate 或直接进入 THORChain → BTC
链上样本显示,攻击者将 TRX 兑换为 USDT 后,USDT 通常仅在其控制地址停留约 1–8 分钟,随后即被送入跨链或兑换服务。因此,本案中留给 Tether 的实务冻结窗口通常只有约 1–8 分钟
其余资金已换成 BTC,或主要以 ETH、DAI 、XRP 形式停留,不具备代币发行方直接冻结地址的路径;但如果资金进入中心化交易所、托管机构或仍可识别的跨链服务,仍可通过平台协作、司法或执法程序尝试拦截
我们对@bitget 被盗资金展开了全面的追踪溯源,当前资金停留在以下地址,部分资金仍然在进行转移
结合我们以往与朝鲜黑客对抗的案例,追踪冻结相关资金具有较大难度,建议采取 @Bybit_Official 对白帽的赏金模式,激励更多优秀的安全公司以及个人研究者对案件持续追踪:
ETH:
0xD2C2f029eFF5caCc686F24377CfdDcfc82d9F899
0x600cfeDc6Bd65Fa79B604dC44964f419e45784b2
0xDc2901f741B4003e32B8B752e97b8c4C1891dC63
0x9FA39d62095302431d7d4167a7E80F8Ec6eA4FA0
0xA6BFd7FcaF4711dA1f61D5E91d03A2c7C72dB272
0xFd5EBe912e2061992437767e24e5BCb52a3f9e54
0xeD5a394a7558929112848B7e97B569de6bbE1A51
0x52f08Feb1B0Da609A5442514E2Bb43C99D25d284
0xe07bd590e1198666230932bad5db3dbbe21e7d57
USDT / USDC:
0xe07bd590e1198666230932bad5db3dbbe21e7d57
BNB:
0x150889FE4fA7a7699588f75C4189FA9e721acFD3
0x3a82a441f1e75d2022d17f6b082979c04fd67652
0x03df4cb9aa0e73a847b2989c1cd00a2a654b32f7
0x2399548147f367375b798256cc620cf2dbac7f10
BTC:
13RcS1N99wQeD6WvjWqS1L6CwheEKBVC7T
XRP:
rDRV9nLg8xbLsafKZnhNgWuE1TiSLE95hs
r3UGfDM4ZyFSCzKH7TQEjgago9QoUJagtJ
rH7oMFKBgdK99TPQctFVzddD7srRzyCqZn
rwSjBrtxBC75TqZ5YvJ1TGfaRpQvVNsAKw
r6NcwN3dR5ciyBv9XsLyMNc9Kg2FBCs7Y
rhdAf73TPX45LmHeZqxzLMdtd44jrY2w3p
r4duMqEXMMmWpaN8LC2URmmVE2JkqTT5ig
rHCPH9VCKvYRsQ2eJBFydpLqLqb5S6a3ET
r3PkiYKo2yFiunHuEGHtTMFPQXEgyCkWj7
rnHdntCUt2vU8YMXarhvSeDRrZ8xwaFcTR
rwRnFu7QeQcd7p5qvyHkububNrfPRyEf2C
r4vyVuh8QXvUHh7HFt4EiFLDVFkTBe7fJx
rQKChXgu2AkqUcGTth2FYHVu93aNYsURZw
rD5AL2MtdRUfDXJF8GPK5CpSF3ZNKKgp6z
RLUSD:
rQKChXgu2AkqUcGTth2FYHVu93aNYsURZw
rD5AL2MtdRUfDXJF8GPK5CpSF3ZNKKgp6z
r4CAbSkDf4MgGZjao78Ufcks3jxr2UiPfD
TRX:
TBWNguTTgezw9dVorX441C6nDrZpRxYwKD
We have conducted comprehensive tracing and forensic analysis of the funds stolen from @bitget . The funds are currently held at the addresses listed below, although some remain in motion.
Based on our previous experience responding to incidents involving North Korean threat actors, tracing and freezing these assets is likely to be highly challenging. We recommend that Bitget adopt a white-hat bounty program similar to @Bybit_Official ’s model, incentivizing more leading security firms and independent researchers to continue monitoring and tracing the stolen funds.
ETH:
0xD2C2f029eFF5caCc686F24377CfdDcfc82d9F899
0x600cfeDc6Bd65Fa79B604dC44964f419e45784b2
0xDc2901f741B4003e32B8B752e97b8c4C1891dC63
0x9FA39d62095302431d7d4167a7E80F8Ec6eA4FA0
0xA6BFd7FcaF4711dA1f61D5E91d03A2c7C72dB272
0xFd5EBe912e2061992437767e24e5BCb52a3f9e54
0xeD5a394a7558929112848B7e97B569de6bbE1A51
0x52f08Feb1B0Da609A5442514E2Bb43C99D25d284
0xe07bd590e1198666230932bad5db3dbbe21e7d57
USDT / USDC:
0xe07bd590e1198666230932bad5db3dbbe21e7d57
BNB:
0x150889FE4fA7a7699588f75C4189FA9e721acFD3
0x3a82a441f1e75d2022d17f6b082979c04fd67652
0x03df4cb9aa0e73a847b2989c1cd00a2a654b32f7
0x2399548147f367375b798256cc620cf2dbac7f10
BTC:
13RcS1N99wQeD6WvjWqS1L6CwheEKBVC7T
XRP:
rDRV9nLg8xbLsafKZnhNgWuE1TiSLE95hs
r3UGfDM4ZyFSCzKH7TQEjgago9QoUJagtJ
rH7oMFKBgdK99TPQctFVzddD7srRzyCqZn
rwSjBrtxBC75TqZ5YvJ1TGfaRpQvVNsAKw
r6NcwN3dR5ciyBv9XsLyMNc9Kg2FBCs7Y
rhdAf73TPX45LmHeZqxzLMdtd44jrY2w3p
r4duMqEXMMmWpaN8LC2URmmVE2JkqTT5ig
rHCPH9VCKvYRsQ2eJBFydpLqLqb5S6a3ET
r3PkiYKo2yFiunHuEGHtTMFPQXEgyCkWj7
rnHdntCUt2vU8YMXarhvSeDRrZ8xwaFcTR
rwRnFu7QeQcd7p5qvyHkububNrfPRyEf2C
r4vyVuh8QXvUHh7HFt4EiFLDVFkTBe7fJx
rQKChXgu2AkqUcGTth2FYHVu93aNYsURZw
rD5AL2MtdRUfDXJF8GPK5CpSF3ZNKKgp6z
RLUSD:
rQKChXgu2AkqUcGTth2FYHVu93aNYsURZw
rD5AL2MtdRUfDXJF8GPK5CpSF3ZNKKgp6z
r4CAbSkDf4MgGZjao78Ufcks3jxr2UiPfD
TRX:
TBWNguTTgezw9dVorX441C6nDrZpRxYwKD
@GracyBitget @xiejiayinBitget


很遗憾看到Hsin-Ju死亡的消息,但这似乎助长了一些阴谋论的传播,我希望补充一些额外信息:
“当警员发现她时,她的手臂上插着一根针,从车窗外就能看见。他们知道是药物过量,所以打破了车窗,试图给她用药,但她已经死亡了” @hack_vc @alpackaP
I’m saddened to hear of Hsin-Ju’s death, but the news seems to have fueled the spread of conspiracy theories. I’d like to share some additional information:
“When officers found her, she had a needle in her arm that was visible through the car window. They knew it was a drug overdose, so they broke the window and tried to administer medication, but she was already deceased.” @hack_vc @alpackaP
Darcy 资产救援⛑️ retweeted

Salus has completed a smart contract security audit of @KeyFlow_EN’s KEYFlexibleStake
Developed by the KeyFlow team and deployed on @BNBCHAIN, the contract supports multiple asset configurations to provide users with a more flexible on-chain staking and asset management experience
The audit focused on signature verification, access control, core business logic, and critical execution paths—helping the team identify potential risks and further strengthen the contract’s security and reliability
No high- or medium-severity issues were identified within the audited scope
Read the full audit report:
github.com/Salusec/Salus-aud…

我们正在招聘兼职「渠道商务拓展」(Partnerships & Business Development)伙伴!
Salus 专注于智能合约审计、Web3 渗透测试及资产救援服务,为 Web3 项目提供专业的安全支持。
我们的安全成绩:
🛡️ 300+
已服务及保护的项目
✅ 0 REKT
官网披露的受保护项目安全记录
📈 100%
官网披露的项目安全率
⚔️ 100%
官网披露的渗透测试成功率
你将与我们一起:
• 服务有安全需求的优质 Web3 项目
• 通过社区及生态合作伙伴拓展合作渠道
• 持续跟进潜在客户与合作机会
• 协助建立长期、稳定的生态合作关系
有商务拓展、渠道合作或社区运营经验者优先。
兼职岗位 · 完全远程
提供行业内具有竞争力的薪酬与激励机制
请将简历或简短的个人介绍发送至 [[email protected]],或者直接私信投送到@Jack24klove 或 @DarcyAri 进行最快速度交流沟通
邮件主题:Part-time Channel BD(兼职渠道商务拓展)
如果你认识合适的人选,欢迎转发或推荐!
We’re hiring a part-time Channel Business Development professional to join our Partnerships & Business Development team!
Salus specializes in smart contract audits, Web3 penetration testing, and asset recovery services, providing professional security support for Web3 projects.
Our security track record:
🟠 300+
Projects served and protected
🔴 0 REKT
Publicly disclosed security record of protected projects
🟠 100%
Project security rate disclosed on our official website
🔴 100%
Penetration testing success rate disclosed on our official website
You’ll work with us to:
• Support high-quality Web3 projects with security needs
• Develop partnership channels through communities and ecosystem partners
• Follow up with prospective clients and partnership opportunities
• Help build stable, long-term ecosystem partnerships
Experience in business development, channel partnerships, or community operations is a plus.
Part-time · Fully remote
Industry-competitive compensation and incentives
Send your CV or a brief introduction to [email protected]. For the fastest response, you can also DM @Jack24klove or @DarcyAri directly.
Email subject: Part-time Channel BD
Know someone who might be a great fit? Feel free to share this opportunity or refer them to us!

分析发现,FomoPeek 事件作案团伙在今年 6 月已有私钥盗取相关的作案记录,但其作案手段是否与Fomopeek案一致,仍有待进一步核查
本次事件的已确认黑客地址:
0x6d37f2C5e8F8546b648D317295565dA95975f4BB
获利约 57.99 万 U,资金主要分为以下三条路径进行转移:
FixedFloat 路径,合计 401,028 USDT:
经地址:0x111faeb95cd0786593433bcc762dc5c1debf541c 转入FixedFloat,215,000 USDT
经地址: 0x2d53113c89c83c520c17b8bbcdc22aa0518a38be 转入FixedFloat,27,028 USDT
经地址:0x0df6ac2e2856114228756947d1b1d9ff63ea3e68 转入FixedFloat,159,000 USDT
KuCoin 路径,合计 20,000 USDT:
从 0x2d53113c89c83c520c17b8bbcdc22aa0518a38be 分两笔转出,每笔 10,000 USDT,分别经过两个存款地址,最终归集至 KuCoin 热钱包
担保平台路径,合计121,458.3085 USDT:
经地址: 0x4c73d7e8ef0e61129403e219debc597fd43aa0ec 中转后,流向担保平台关联地址,111,458USDT
经地址: 0x0361897d757d13a4afad64a2e1bc561b96a8c7cf 进入 CCE 混币服务,流向担保平台关联地址,10,000 USDT
我们正在对其余涉案地址展开更全面的追踪。如果你是 FomoPeek 事件受害者,或掌握相关线索,可私信@DarcyAri 或 @Jack24klove ,提供被盗地址、交易哈希,帮助我们进一步锁定资金流向和关联地址

Analysis indicates that the group behind the FomoPeek incident had already been involved in a private-key theft case in June. Whether the same method was used in this incident remains under investigation
Confirmed hacker address in this incident:
0x6d37f2C5e8F8546b648D317295565dA95975f4BB
Estimated proceeds: approximately 579,900 USDT
The funds were primarily transferred through three routes:
• FixedFloat route:
215,000 USDT via 0x111faeb95cd0786593433bcc762dc5c1debf541c
27,028 USDT via 0x2d53113c89c83c520c17b8bbcdc22aa0518a38be
159,000 USDT via 0x0df6ac2e2856114228756947d1b1d9ff63ea3e68
totaling 401,028 USDT
• KuCoin route:
20,000 USDT was transferred from 0x2d53113c89c83c520c17b8bbcdc22aa0518a38be in two separate transactions of 10,000 USDT each. The funds passed through two deposit addresses before being consolidated into a KuCoin hot wallet
• Escrow-platform route:
111,458.3085 USDT was routed through 0x4c73d7e8ef0e61129403e219debc597fd43aa0ec before reaching addresses associated with an escrow platform.
10,000 USDT entered the CCE mixing service via 0x0361897d757d13a4afad64a2e1bc561b96a8c7cf and subsequently reached addresses associated with an escrow platform.
We are conducting a more comprehensive trace of the remaining addresses involved in the incident.

Darcy 资产救援⛑️ retweeted

On Sep 14, we showed how a single prompt injection could drain an OKX OnchainOS agent @wallet in a local test.
Today, we're breaking down the technical details of the hack.
It starts with a token's name. 🧵

受害人疑似因私钥泄露,被盗取金额超80wu,资金迅速拆分流向疑似OTC网络
Salus @salus_sec 及时响应,协助其进行追踪调查,已帮助受害人成功挽回损失约 6.8wu,目前正在进行下一步调查工作

一名Hyperliquid用户账户遭到未经授权控制,约73.86万USDC已被转走,另有10,287枚HYPE被解除质押,部分被盗资金流向疑似Bitget相关地址
受害账户:
0x5b6d236e39a4723a8f79db93cfd1af4d228f9c60
截至核查时,这批HYPE仍在staking balance,尚未进入提款队列。攻击者如继续发起cWithdraw,经过7天等待期后,即可将资产进一步转移
我们近期接触的2起类似案件中,受害人被盗时同样有资产仍处于质押阶段,却因缺少可由用户触发的紧急暂停和恢复机制,最终未能阻止资产被再次盗走,该情景下损失已超过110万U,本案的10,287枚HYPE也正面临同样风险
针对私钥或账户签名权限失陷后,质押资产尚未完成提款的情况,为保护用户权益,我们建议Hyperliquid考虑推出由用户预先启用的Guardian / Recovery机制:
Guardian只能临时暂停cWithdraw、转账、Agent授权及多签变更,不能转移资金
暂停应自动到期且不能无限续期,Guardian更换或账户恢复应经过时间锁、证据审核及独立或验证者门槛,并将状态变更公开记录在链上

A Hyperliquid user account was taken over without authorization. Approximately 738,600 USDC was transferred out, while another 10,287 HYPE was undelegated. Some of the stolen funds appear to have reached addresses potentially associated with Bitget.
Affected account:
0x5b6d236e39a4723a8f79db93cfd1af4d228f9c60
At the time of our review, the HYPE remained in the staking balance and had not yet entered the withdrawal queue. If the attacker initiates a cWithdraw, the assets can be transferred after the seven-day waiting period.
In two similar cases we handled recently, the victims also had assets still in staking when their accounts were compromised. Due to the absence of a user-triggered emergency pause or recovery mechanism, they were unable to prevent those assets from subsequently being withdrawn and stolen. Losses under this scenario have already exceeded $1.1 million. The 10,287 HYPE in this case now faces the same risk.
To better protect staked assets that remain pending withdrawal after a private key or account-signing compromise, we propose that Hyperliquid consider introducing an optional Guardian / Recovery mechanism that users can configure in advance.
A Guardian should only be able to place a temporary hold on cWithdraw, transfers, Agent approvals, and multisig changes. It must never be able to move funds, and the hold should expire automatically without allowing indefinite renewal.
Guardian replacement or account recovery should require a timelock, evidence-based review, and an independent or validator-governed threshold, with every state change recorded publicly on-chain.

经调查,MSX @msxcom 创始人 @BTCBruce1 或为 Hyperliquid 上的巨鲸地址实控人,该地址承接大量的MSX热钱包体系关联资金,并且上游注资地址与汇旺担保存在交互,接收超 1500w 杀猪盘关联资金:
Hyperliquid 地址:0x32008FCB6bbD16532Afc83ca8b6C920DDE22c407
MSX 内部结算钱包 D 直接向 Hyperliquid 交易钱包B转入300万USDT,MSX 多链归集钱包X分两笔向Hype交易钱包B转入300万和200万USDT,合计800万USDT。
其中一笔 200 万 USDT 可以从 MSX 旧 Ethereum 热钱包 H 开始完整追踪。
tx1:
0x30f8e270299ffcb021f3346324af76567e2ceba42d5e66de90b739304a714a34
tx2:
0x59f3bcf6cd6acb1905951b22b98cc1e6d6fe50408089f031643ee88d5a5c4254
tx3:0xa7d29986465cfa5e8018b40debfc4c653781941f73262007083e8cb9af85e708
并且 Hyperliquid 交易钱包 B 与 MSX 体系之间还存在反向资金调拨。 Hyperliquid 交易钱包 B 曾直接向 MSX 旧 Ethereum 热钱包 H 转入97万 USDT,很快又原额转给 MSX 内部结算钱包 D;

According to an on-chain investigation by Salus, MSX’s hot wallets and internal settlement system have conducted large-value transactions with a Hyperliquid whale account suspected of being controlled by its founder. The fund flows indicate that MSX user assets may have been transferred into this account and used for perpetual futures trading at approximately 11.2× leverage.
As of September 7, 2026, the account held roughly $89.31 million in notional positions, with approximately $7.97 million in equity and $3.046 million in unrealized losses.
The upstream funding of this Hyperliquid account can be traced to TRON address P. A deposit QR code shown in a public video further indicates that P is an address associated with Betronomy deposits.
The data also identifies direct, one-hop inflows to P from two Huione-linked wallets. Huione Group remains the subject of ongoing investigations and enforcement actions by U.S. law enforcement and regulatory authorities.
Taken together, the fund flows raise serious concerns that MSX user assets may have been diverted into high-leverage trading, while the upstream funding links to a suspected Ponzi-style scheme deposit address and Huione-associated payment channels.
These findings reflect risk indicators observed in publicly available on-chain evidence. Further investigation is warranted into the sources of funds, control relationships, and ultimate destinations of the assets.
@FBI @zachXBT
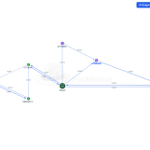
MSX 链上地址关联调查
通过实际充提币测试确认 MSX 的三个热钱包锚点:MSX 当前 Ethereum 热钱包 A 、MSX 旧 Ethereum 热钱包 H、MSX Solana 热钱包及归集地址 S
以这三个地址为起点继续扩展,MSX 内部结算钱包 D 与 MSX 旧 Ethereum 热钱包 H 发生 45 笔直接双向 USDT 结算,并向 MSX 共同部署执行节点 G1 提供 50 ETH ,可定性为 MSX 内部结算钱包
MSX 多链归集钱包 X 由 MSX 旧 Ethereum 热钱包 H 预先注资、由 MSX 共同部署执行节点 G1 启动,同时持续接收 MSX 旧 Ethereum 热钱包 H 、MSX 内部结算钱包 D 及 MSX Solana 热钱包 S 资金簇通过多条跨链路线定向交付的资金,可定性为 MSX 多链归集钱包
MSX 批量分发钱包 T 由 MSX 共同部署执行节点 G1 启动,直接向 MSX 当前 Ethereum 热钱包 A 和 MSX 旧 Ethereum 热钱包 H 归集资金,并与 MSX 内部结算钱包 D 、MSX 运营及资金调度钱包 K 双向调拨,可定性为批量分发钱包
MSX 运营及资金调度钱包 K 与 MSX 当前 Ethereum 热钱包 A、MSX 旧 Ethereum 热钱包 H、MSX 内部结算钱包 D、MSX 批量分发钱包 T 均有直接、双向、跨功能资金往来,可定性为运营及资金调度钱包
MSX 共同部署执行节点 G1 负责启动 MSX 多链归集钱包 X 和 MSX 批量分发钱包 T,可定性为 MSX 强关联的部署执行节点。
相关地址:
MSX 当前 Ethereum 热钱包 A
0xa53970f778F2ffe563a345FC38138982dE867477
MSX 旧 Ethereum 热钱包 H
0xbF0b8b961Fc8F0d04fEe805da299b1280889FcE6
MSX Solana 热钱包及归集地址 S
BJGtfqrBnHsKtzZ9Qi99z3FTQi5w8L8uWr6naDMxqDPF
MSX 内部结算钱包 D
0x566092a61eF24125EFe743f288621cF0809C851b
MSX 多链归集钱包 X
0x58a0395f539c2f90dac32bef621d1a1e357dfd6a
MSX 批量分发钱包 T
0x09f482aa308035a8328410941c407e083cf8a5ff
MSX 运营及资金调度钱包 K
0x1decE291eb2c8F8e7aC076Ffc8366eC3861B268B
MSX 共同部署执行节点 G1
0x26d66ac9a625090cf6aac66eb848240e37d93207
Hype 交易钱包 B
0x32008FCB6bbD16532Afc83ca8b6C920DDE22c407
Hype 钱包资金管理关联地址 M
0x7c81D4367829fE8C048923aF713f3033052fD612
跨链落地及分发地址 N
0x1365F445Aa962d98B7Cb129CD61E3F835c00A593
Betronomy 关联 TRON 清算地址 P
TDC9KDC2b5ubA71eBQJMnY1eyPYQ4Kkv4x
TRON 清算枢纽 C1
TKHbcnBySP2zuwFNfC5T89rKQyKFRjDEDD
TRON 结算节点 C2
TWVHd6LnSnmjX7nxBZjYkqdwJANJroxtLY
TRON 中转节点 C3
TDhZtysVqKJD2L1BejFLRcmbjeV5Wu1dPm
跨链发起地址 C4
TMo2RNBujvbzZXi5nqP5w152BR5HyczNT5
