
we help Ukrainian nonprofits with digital safety issues
Joined June 2018
- Tweets201
- Following70
- Followers337
- Likes196




Over the summer, Digital Security Lab Ukraine investigated a series of phishing campaigns targeting Ukrainian civil society organizations. Attackers sent fake event invitations and collaboration offers – including invitations to the Ukraine Recovery Conference 2026 – followed by malicious files disguised as legitimate documents.
After execution, the malicious files created Windows scheduled tasks used to download and execute malware and establish persistence on the system.
@Microsoft recently published a broader investigation, which also incorporated data from our research.
Microsoft named this technique RedFlick and linked the attacks to Star Blizzard (aka Coldriver/UNC4057), which is linked to Russia’s FSB.
Also, our colleagues at @RESIDENT_NGO documented similar campaigns targeting Moldovan media and civil society in September, with threat actors impersonating European donor organizations.
Researches:
🔗 dslua.org/publications/spear…
🔗 microsoft.com/en-us/security…
🔗 resident.ngo/lab/writeups/ma…


DSLU investigated a multi-stage phishing campaign targeting Ukrainian civil society that combines reply-baiting, malicious LNK files, GitHub+GitLab abuse, and fileless execution.
The attack starts with a harmless-looking collaboration email with no links or attachments. Only after the victim replies do the attackers send a link to an archive containing an LNK file disguised as a PDF.
Once opened, it displays a decoy document while executing malicious code in the background. The attackers use GitHub to deliver additional code, establish persistence through a scheduled task, and collect and exfiltrate data from the compromised system.
Full technical analysis and IOCs:
dslua.org/publications/livin…


Interesting – DSLU recently investigated a campaign targeting Ukrainian civil society with a remarkably similar attack chain: archive-delivered LNK files masquerading as documents, PowerShell execution, scheduled-task persistence, and remotely retrieved payloads.
In our case, the attackers also abused GitHub and GitLab infrastructure for payload delivery: dslua.org/publications/livin…
3/3
The attackers obtained long-lived OAuth tokens that remain valid after a password change. Because users authenticate through Google's legitimate sign-in flow, MFA alone does not stop this technique. Access persists until the malicious app is revoked.
2/3 The infrastructure included:
• lookalike domain with SPF/DKIM/DMARC
• hCaptcha-based anti-analysis
• fake Google Drive (React)
• OAuth token interception infrastructure
• 4 domains registered the same day
1/3 🚨 DSLU investigated a targeted phishing campaign against the Ukrainian civic network OPORA.
Instead of stealing passwords, the attackers abused OAuth consent phishing to compromise Google accounts.
Technical analysis:
dslua.org/publications/phish…


3/3 Indicators (defanged):
🔗 103[.]160[.]59[.]97
🔗 89[.]125[.]66[.]183
🌐 secure-dns-hub[.]com
📧 [email protected]
📦 Files.vhdx inside a password-protected ZIP
Full IoCs + analysis in the report
2/3 What makes it sneaky 👇
The first email has NO attachment. The malicious file arrives ONLY after you reply asking for it - so it slips past bulk scanning and reaches only engaged targets.
The payload hides inside a virtual disk (VHDX) to dodge Windows' download warning.
1/3DSLU uncovered a targeted phishing campaign against Ukrainian civil society - advocacy groups, journalists, and economists.
The lure: fake #URC2026 Ukraine Recovery Conference invitations that quietly install Windows malware.
Full report: dslua.org/publications/spear…


🚨 DSLU analyzed a spearphishing campaign targeting Ukrainian organizations, attributed with moderate confidence to UAC-0050.
The attackers impersonate Ukraine’s State Tax Service and deliver LiteManager Pro RAT via password-protected archives hosted on Backblaze.


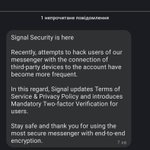
Threat actors are adapting @signalapp phishing campaigns: Ukrainian users now receive messages allegedly from Signal about “mandatory 2FA” due to ongoing attacks.
No codes are requested yet – this is a trust-building step before attempts to steal login codes and hijack accounts.

IOCs:
Domains:
www[.]saas[.]successint[.]org
pub-f2449c7fa66a473db1ad9323672392cf[.]r2[.]dev
rushdayz[.]com
URL paths:
/pta/grd
/index.html?eta=
/z/api.php?action=save
🔎 New analysis of a credential phishing campaign
It leverages domain-adaptive infrastructure to evade detection and increase the success rate of account compromise.
Details: dslua.org/publications/analy…


IOCs:
🔺Domains:
ln[.]run
badge-verified0903261[.]vercel[.]app
🔺URLs:
hxxps://ln[.]run/badge-verified0903261
hxxps://badge-verified0903261[.]vercel[.]app/index1[.]html
Detailed analysis and more IOCs: dslua.org/publications/meta-…
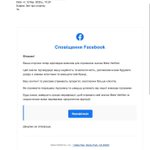
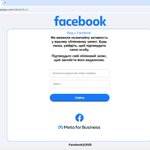
Large-scale phishing attacks keep evolving, abusing trusted platforms like Google, Cloudflare, Vercel, and Telegram. Pre-built kits enable massive scaling. A new “Meta Verified” tactic steals credentials and bypasses 2FA in real time via Telegram exfiltration.


SHA-256:
4362f67ab65cca32fb610e62745aac7d8587a7bac46e5a6c89db8b4a9c7e9458
f78944a2699b21fb34fc9c1c7c0ae7ca16c709bf72cbc15ad0cdaa66bec8d1bd
ad8a491018f5c5edecfc75ec3a3627aa04a26019ce87c8f236bb400ec35c3244
a0e709c0df0e38b30a2283dc5c1667c852d212952cc4db18c364d35a70ca0c96
IOCs:
46.4.92[.]6
64.20.61[.]146
pixeldrain[.]com
id[.]remoteutilities[.]com
Payload:
Remote Utilities
rutserv.exe, rfusclient.exe
Attack chain:
PDF posing as an official document→ embedded button→ RAR archive→ ZIP archive→ JS file disguised as a document.
The JS drops a fake “corrupted” PDF for the user, requests elevated privileges, and silently downloads an MSI payload.
Final stage: installation RAT


