

Security Researcher @block_apex | dApp Auditor @hackenclub | eCPPTv2 | CRTP | CEH (Practical)| DM -Audit/Pentest
Joined July 2020
- Tweets472
- Following497
- Followers269
- Likes349






Recently tested an LLM app with AI agents wired into real company tools.
A stack trace → a version → a known CVE → other users’ OAuth tokens, all from a normal account.
Full write-up 👇
gdroz3r.github.io/blog/break…
#AISecurity #LLMSecurity #AppSec #PenTesting
Happy to contribute! 🔥

Glider Contest final leaderboard.
🥇 @ChaseTheLight99
🥈 @0xodus
🥉 @0xK42
Congrats, and thanks to everyone who submitted queries.
Wrote up a recent API pentest. Six business logic bugs I found in a payment API, and how I found them.
gdroz3r.github.io/blog/break…
Completed an off-chain source code security review with @ShieldifySec . Identified critical and multiple medium severity security issues during the assessment.
Grateful for the opportunity 🫡 looking forward to more engagements! 🚀
Been busy lately!
Started working as a Security Engineer for a fintech app, helping integrate security into the SSDLC process. 🔒
At the same time, I built my portfolio website. 🚀
gdroz3r.github.io/
Gul Hameed retweeted
I've Open sourced: 6-day Canton/DAML security bootcamp for auditors crossing from EVM/Solana.
26 vulnerability patterns, code examples, deployment audit checklist, OZ toolchain
github.com/gdroz3r/Canton-da…
@CantonNetwork @CantonFdn
#canton #daml

Gul Hameed retweeted
spent some time pulling my security work into one place
👇
web2 pentests → CEX audits → web3 protocol audits.
Research.
want to collab? DMs open
github.com/gdroz3r/gdroz3r

These are great resources for learning Canton.
Thank you for the mention as well.

📢Currently, many firms and protocols are actively looking for DAML-focused auditors.
If you want to position yourself early in this niche, here’s a structured roadmap to become a strong DAML auditor and start getting booked faster:
1. Always start with the official docs:
- DAML official docs: docs.digitalasset.com
- Canton Network docs: docs.canton.network
2. Refresh with writeups:
Great for understanding real-world attack surfaces and audit methodology.
- scauditstudio.com/blog/DamlS…
- halborn.com/blog/post/daml-a…
- informal.systems/blog/securi…
- halborn.com/blog/post/daml-a…
3. Read Real Audit Reports:
This is where most people level up.
- certificate.quantstamp.com/f…
- certificate.quantstamp.com/f…
- halborn.com/audits/temple/da…
Pro tip: Reproduce findings locally and try identifying additional edge cases the auditors missed
4. Learn the tools:
- daml-lint : Static analyzer
- daml-props : Property-based testing
- daml-verify : Formal verification
Kudos to @OpenZeppelin for creating tools.
The strongest auditor combines automated testing (including AI) alongside manual.
The DAML/Canton ecosystem is still early. If you consistently study docs, review audits, train your AI agent, and practice on live codebases, you’ll be ahead of most auditors entering the space.
📌Bookmark this thread if you're serious about DAML security.

Gul Hameed retweeted

📢Currently, many firms and protocols are actively looking for DAML-focused auditors.
If you want to position yourself early in this niche, here’s a structured roadmap to become a strong DAML auditor and start getting booked faster:
1. Always start with the official docs:
- DAML official docs: docs.digitalasset.com
- Canton Network docs: docs.canton.network
2. Refresh with writeups:
Great for understanding real-world attack surfaces and audit methodology.
- scauditstudio.com/blog/DamlS…
- halborn.com/blog/post/daml-a…
- informal.systems/blog/securi…
- halborn.com/blog/post/daml-a…
3. Read Real Audit Reports:
This is where most people level up.
- certificate.quantstamp.com/f…
- certificate.quantstamp.com/f…
- halborn.com/audits/temple/da…
Pro tip: Reproduce findings locally and try identifying additional edge cases the auditors missed
4. Learn the tools:
- daml-lint : Static analyzer
- daml-props : Property-based testing
- daml-verify : Formal verification
Kudos to @OpenZeppelin for creating tools.
The strongest auditor combines automated testing (including AI) alongside manual.
The DAML/Canton ecosystem is still early. If you consistently study docs, review audits, train your AI agent, and practice on live codebases, you’ll be ahead of most auditors entering the space.
📌Bookmark this thread if you're serious about DAML security.
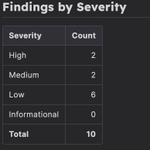
Just wrapped a Mobile Pentest for a CEX 📱
10 findings - 3 Medium, 5 Low, 2 Info.🔥
Wild how many issues are still sitting in production CEX apps in 2026. Mobile is still where security debt lives.
Get your apps pentested - DMs open. 🛡️


Thanks, Team! 🫡🔥

Proud to share that our auditor @CyberGul has contributed an excellent resource for developers and security researchers diving into @CantonNetwork & DAML auditing 🔍
We’ve now added the repository to the @block_apex GitHub for broader access and continued contributions from the team.
Check it out here:
github.com/BlockApex/Canton-…
Huge shoutout to @CyberGul for the effort put into this 👏

All of my Glider queries are now approved in the Glider DB ✅ Huge thanks to @xyz_remedy especially @_mr_thank_you_ (reviews + optimization) + the team.
Hope these help catch bugs earlier and keep protocols safer. Appreciate it 🤝
r.xyz/glider-query-database/…

Kicked off a Mobile App Pentest for a CEX today. Hoping to surface some interesting bugs. Should be a great week! 🔥🕵️♂️
spent some time pulling my security work into one place
👇
web2 pentests → CEX audits → web3 protocol audits.
Research.
want to collab? DMs open
github.com/gdroz3r/gdroz3r
Just wrapped a Canton/Daml smart contract Review found around 10 issues. (more details soon)
If you're curious about Daml based audits, this is the resource
github.com/gdroz3r/Canton-da…
I've Open sourced: 6-day Canton/DAML security bootcamp for auditors crossing from EVM/Solana.
26 vulnerability patterns, code examples, deployment audit checklist, OZ toolchain
github.com/gdroz3r/Canton-da…
@CantonNetwork @CantonFdn
#canton #daml
STATE MACHINE - 2 of 20:
E.1 Catching ContractNotActive - silently uses archived state, masks auth errors
E.2 Stale snapshot reads - cross-tx divergence (e.g., price changed since quote)