

one of the many
WeAreCultDAO
Joined August 2008
- Tweets4.2K
- Following337
- Followers4.9K
- Likes6.2K




Pinned Tweet
Dual-Token Economy of @ModulusZK :
- $CULT for gas
- $MOD for specialized utilities & team Dapps
$MOD token distribution
MAX supply : 666 million tokens

Fam ill be taking a break from X and Crypto i have few things to focus on
I will be back when the time is right
i understand the team worked hard and theres no funding at all and i appreciate this hard work but pulling liquidity from $RVLT aint the answer @RevoltToEarn had its own members who believed in it
feeling sorry for whoever lost funds there.
🚨 ALL EYES ON @ModulusZK
zkFOL time is here and now 🔥
capital will rotate to $CULT (DAO)
this is gonna be violent 🔥🔥🔥
Trends get rewarded purely because they create volume, fees, bags, and engagement. Quality doesn’t matter until the chart forces attention.
$CULT isn’t ugly. It’s just not the current trend yet.
马哈茂德 🩸🩸🩸مْحَمْوُدْ• CULT DAO retweeted

What if smart contracts didn’t need code, VMs, or bytecode?
#zkFOL compiles first-order logic directly into polynomial constraints.
The contract *IS* the specification!
A state transition ONLY happens if it can be proven valid.
No VM. No execution layer.
Massive speed & memory gains vs current zkVMs on ordinary hardware.
Early tech, just #opensource .
Worth a look if you’re into ZK or privacy.
#zkFOL #ZeroKnowledge #ZK #Privacy #ModulusZK


Cryptocurrency thrives as a scarce, decentralized alternative to fiat money whose supply central banks can expand at will, eroding purchasing power through inflation. Its core appeal as a long-term store of value and inflation hedge depends on the persistence of that monetary flaw. If the existing system were genuinely fixed with credible, non-inflationary policy, hard constraints on money creation, and restored trust in fiat as sound money the main economic rationale driving demand for crypto would largely disappear, leaving it without its strongest use case and we all know that will never happen.
马哈茂德 🩸🩸🩸مْحَمْوُدْ• CULT DAO retweeted

Leave your meme coin community
Wear this mask
Join #CultDAO
Built by the people
Lead by the people 🩸🩸🩸
We are more than everyone
Unite.

Crypto spends a lot of time asking how to make zkEVMs faster.
zkFOL asks a more disruptive question: how much of the virtual machine do we need in the first place?
A zkEVM proves that @Ethereum-compatible code executed correctly. @ModulusZK’s zkFOL approach expresses applications as logical conditions and proves that a proposed state transition satisfies them, compiling those conditions into polynomial constraints. That changes the starting point for building an application. (ethereum.org, docs.moduluszk.io)
So why isn’t zkFOL getting more attention?
My view: crypto understands a faster version of an existing product more easily than a different architecture.
“Better zkEVM” fits an established story: #Solidity developers, Ethereum compatibility, existing applications, familiar investment categories.
“Build applications around provable logical conditions” requires people to rethink the development model and explain why developers would switch.
Existing investment, tooling and commercial commitments may also make that conversation uncomfortable. But limited attention does not prove deliberate suppression. Some skepticism is reasonable: a compelling idea still needs reproducible results, independent security review and applications people actually use.
@ModulusZK publishes striking benchmark results against SP1 and RISC Zero. Those are specific zkVM comparisons on selected workloads, not evidence that #zkFOL has already outperformed production zkEVMs across real @Ethereum applications. The results deserve investigation; the broader conclusion still needs testing. (moduluszk.io)
What could this mean for zkEVM companies?
If zkFOL delivers meaningful advantages in production, companies whose main advantage is proving efficiency could face pressure on pricing and margins.
Teams with strong developer relationships, liquidity, distribution and settlement infrastructure may be better positioned to adapt. They could integrate new proving approaches, support a second application model or build services around it.
Ethereum compatibility would still have value. A new architecture does not automatically migrate existing contracts, assets and users.
For investors, the distinction is crucial: technical success and investment returns are separate questions.
A cheaper proving system could create enormous user value while reducing revenue for some infrastructure providers. An incumbent could adopt the technology successfully. A technically impressive newcomer could struggle to attract developers.
The questions become: who captures the savings, who owns the customer relationship, and does adoption create revenue or token demand at all?
How would a transition likely happen, if zkFOL succeeds?
My expectation is gradual adoption:
-Independent teams reproduce results and test the security assumptions.
-Narrow applications adopt it where expressing explicit rules offers a measurable benefit.
-Integrations connect those applications to existing wallets, assets and settlement systems.
-Developers choose it for new products; established applications migrate only when the benefits justify rewriting and reviewing them.
-Both models coexist, with adoption expanding where the evidence is strongest.
This also changes what security review focuses on. A proof can establish that a transaction satisfies the rules you wrote. It cannot establish that you wrote every rule your business needed. Specification mistakes, oracle assumptions and integration failures still matter.
🚨zkFOL deserves serious scrutiny now. Demonstrating a useful new approach is a meaningful achievement before a complete chain ships; establishing production security remains a separate milestone.
The industry should be willing to test an architecture that challenges its assumptions.
And zkFOL’s strongest case will be made by independent results, useful applications and developers choosing it because it works.

zkFOL is now public.
It compiles first-order logic predicates directly into polynomial constraints. No bytecode. No VM. No execution layer.
Published claim on the same fib(10,000) benchmark:
• zkFOL: 4.82 ms, <10 MB
• RISC Zero / SP1: 3.7–49 s, 312 MB–17 GB
Looking for independent reproduction of the numbers.
Repo: github.com/zkFOL/zkfol
Paper: github.com/zkFOL/zkfol/blob/…
@benediktbuenz @ronrothblum @pumatheuma @BruestleJeremy @SuccinctLabs @RiscZero @zksecurityXYZ

Every major zkVM (RISC Zero, SP1, etc.) still forces you to write code → compile to a VM → emulate that VM inside a circuit → then prove the circuit.
zkFOL deletes the middle steps.
It compiles first-order logic straight into polynomials. No bytecode. No virtual machine. No execution layer. The rule you write is the rule that gets proved.
Same machine.
Same fib(10,000) claim. Same algorithm:
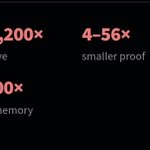
zkFOL: 4.82 ms | 49.8 KB proof | <10 MB memory
RISC Zero: 3.69 s | 210 KB | 312 MB
SP1: up to 49 s | 1+ MB | up to 17 GB
That’s not incremental. That’s three orders of magnitude on hardware you already own with privacy as a free byproduct instead of an expensive extra layer.
Everyone else is still emulating a computer inside a proof system. zkFOL stopped.
@ModulusZK #zkFOL #ZK #ZeroKnowledge
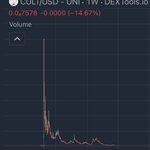
Anyone interested in a "dead" coin with this chart & a bad ass community, bad ass tokenomics and being a GAS token for new zkFOL privacy tech blockchain [ @ModulusZk ] ? $CULT is the ticker.


🩸🩸🩸 @RyoshiResearch
You built $SHIB as a pure experiment in decentralized community ownership no leader, no control, the project belongs to the people.
That same spirit lives in @wearecultdao: a fully autonomous public good. Contracts renounced, liquidity locked, treasury funded by tax, proposals by Guardians, decisions by The Many. No team can stop or alter it. It funds anything that fights centralization.
They are now building @ModulusZK zkFOL.
On Modulus the contract is the specification. Applications are written as first-order logic predicates. A state transition happens only if a proof shows the conditions hold. No bytecode. No VM. No execution layer. No gap between what the author meant and what the chain does.
Defects refuse instead of paying out. Proving is orders of magnitude faster and lighter than zkVMs. Privacy is native. The entire Uniswap-style swap is four logical lines.
This is the next step of the vision you started: math-enforced decentralization that cannot be captured or drifted from.
The docs, benchmarks, and code are public:
moduluszk.io
docs.moduluszk.io
github.com/zkFOL/zkfol
Come back. Look at it. If the vision still matters, help push it forward. The community that believes in what you started is ready.
Request for review: zkFOL, a direct arithmetisation of first-order logic, now public.
@ModulusZK compiles application rules written as first-order logic predicates straight to polynomial constraints. There is no bytecode and no zkVM. A state transition is accepted only with a proof that the predicate holds. The contract is the specification; a rule that cannot be proved does not execute.
The implementation is the construction in Murdoch J. Gabbay’s ePrint 2024/954, “Arithmetisation of computation via polynomial semantics for first-order logic”: truth maps to 0, conjunction and universal quantification to addition, disjunction and existential quantification to multiplication, with no encoding into an abstract machine.
Public material:
• Repo: github.com/zkFOL/zkfol/
• Draft: github.com/zkFOL/zkfol/bl…
• Docs: docs.moduluszk.io
The published desktop-CPU comparison, fib(10,000) by fast doubling against RISC Zero 3.0.5 and SP1 6.3.1, is 4.82 ms and under 10 MB versus 3.69–49.24 s and 312 MB–17 GB. Those figures are ours. They have not been independently reproduced.
What we want is a technical review, not an endorsement. In particular: soundness of the shallow translation outside the finite models in the paper, the compiler from predicate to constraint system, the commitment scheme and any setup assumption, and a rerun of the fib benchmark.
If you review proof systems or polynomial commitments, a written objection is as useful as a confirmation. Repo, draft, and ePrint are linked above.
@0xJaehaerys @cryptodavidw @benediktbuenz @ronrothblum @pumatheuma @SuccinctLabs @BruestleJeremy @RiscZero @drakefjustin @0xAlbertG @ant_sabado @AnnaRRose @zeroknowledgefm @IOHK_Charles @VitalikButerin @EliBenSasson
JUST IN🚨
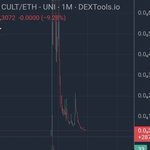
$CULT against $ETH hits an all time low
so much $CULT has been sold
CULT uniswap pool at an ATH
-i would never sell even $1 with a chart looking like this its max bottom signal even if it takes look
- @ModulusZK released the GitHub docs for zkFOL tech
ngl idk what should happen but theres loads of gasoline everywhere for #CultDAO and @modulusZk im just watching how will this be ignited.
