


Derpino retweeted

🚨 UPDATE: 1.7M $BTC sits in addresses with exposed public keys, Starknet says, as quantum attack estimates fall 20x.

Derpino retweeted
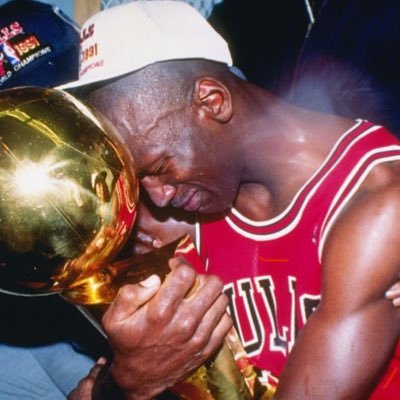
Police have confirmed nearly $1 million worth PSA trading cards were stolen in Fedex truck heist


Derpino retweeted

‼️ BREAKING: 8 Private keys belonging to eMudhra intermediate certificate authorities (CA) have been compromised.
Chrome and Firefox blocked the affected certificates within hours. Go, NSS, and other software have issued fixes.
Full details - thehackernews.com/2026/10/ei…

Derpino retweeted

‼️BREAKING: Security firm Calif appears to have a working exploit for the leaked PHP flaws, hours before the patch.
A briefly posted video credited to Calif shows it running commands on a WordPress 7.1.3 site on PHP 8.5.4. Kevin Beaumont says a screenshot from it is real.
A separate public PoC is also circulating, but its own author now says one of its attack chains is dead and code execution is unreliable.
Admins have two stopgaps until the fix lands at 14:00 UTC today.
Turning off session.upload_progress.enabled in php.ini disables the feature the leaked details point to. The only cost is upload progress bars.
Blocking every request with a multipart Content-Type at the web server goes further, but breaks file uploads.
Neither is official. Gina Peter Banyard, a PHP core developer at the PHP Foundation, says "the only mitigation is patching / upgrading PHP."
If you can afford to switch a server off for a day, she says, that might be the most sensible thing to do.
"I sadly know too much," she wrote.


Derpino retweeted
‼️ PHP UPDATE: A public exploit for the leaked PHP flaws is now online, complete with downloadable code, hours before the patch.
Its author, who posts as J4ck3LSyN, says it was recreated and "lab/field tested", and labels one of the two bugs "weaponized (lab)".
The PoC was recently updated, admitting the attack chain it first described does not work.
A separate exploit credited to security firm Calif was shown running commands on a WordPress test site in a video that was briefly posted.
PHP's fix is due at 14:00 UTC today.


Derpino retweeted
‼️ PHP UPDATE: The Dutch parliament, the Dutch national cyber agency and Finland's central government have pulled websites offline ahead of the PHP patch.
Finland's state IT centre Valtori is shutting down public-facing central government web services. The National Land Survey of Finland is already down.
In the Netherlands, the Tweede Kamer, the NCSC and the Dutch Data Protection Authority are offline. So are tech site Tweakers and NotuBiz, which runs council information for 100+ local governments.
The University of Vienna switched off its websites, webmail and Moodle. The University of Freiburg and Finland's Haaga-Helia have taken services down too.
Fur Affinity, Pinboard, explain xkcd and every wiki on Miraheze are dark as well.
Valtori says its shutdown is a precaution, not the result of an attack or breach.
PHP was created by Rasmus Lerdorf in 1994, it initially stood for Personal Home Page
PHP's fix is due at 14:00 UTC today.


Derpino retweeted
🚨 TECH EMERGENCY: The internet could be facing what security researchers are calling a “HACKPACALYPSE.”
In simple terms, an Indian company responsible for issuing digital certificates used to secure software and internet communications reportedly made a catastrophic security mistake.
Some of its supposedly secret cryptographic keys were generated using shockingly weak numbers, including one as simple as “4.” Other keys were reportedly just as insecure, making them potentially easy for attackers to crack.
Now, a massive security response could be underway, with affected software, systems, and devices needing urgent updates before hackers can exploit these weaknesses.
The biggest concern? State-sponsored hackers, including groups linked to North Korea, could potentially take advantage of vulnerable, unpatched systems to launch cyberattacks, compromise software, and cause widespread disruption.
The race is now on to secure affected systems before attackers can exploit them.

Derpino retweeted

Buying cards at shows? Read this:
A lot of cards are getting pen-marked to hide whitening and edge damage. It’s easy to miss in bad lighting.
Bring a small blacklight, check the edges before you buy. You might look like a try-hard, but it’ll save you from an expensive mistake.
Derpino retweeted
‼️BREAKING: Cloudflare says it is already seeing early attacks on the two leaked PHP flaws, hours before the patch.
Its CTO Dane Knecht says WAF rules for the known exploit vectors are live for all customers, including free plans, but calls them "a STOPGAP only".
Websites are going dark while they wait. NotuBiz, used by 100+ Dutch local governments, pulled council information sites offline, including those of Den Bosch, Breda and Eindhoven.
explain xkcd and the Star Citizen Wiki are down too.
PHP ships the fix at 14:00 UTC today.


‼️ BREAKING: Two leaked remote code execution flaws in PHP are real, watchTowr confirms.
PHP will ship fixes for two critical flaws, both rated CVSS 9.2, on Wednesday 21 October at 14:00 UTC, a day before the embargo was due to lift.
CVE-2026-109618 and CVE-2026-109619 first surfaced in a Hacker News post whose author admitted having no evidence beyond "source: trust me, bro".
Kevin Beaumont flagged the leak, and watchTowr confirmed it two hours later.
PHP says it may release sooner if details go public or exploitation appears. It has not named the CVEs or the affected versions.


Derpino retweeted

🔴 NEW MEMBERS VIDEO
"THE AI ENDGAME | ICP"
youtu.be/N9f48iLUOW4?is=7wYU…
$ICP ☁️♾️

Derpino retweeted

BREAKING: Security teams around the world are on high alert after 8 internet security certificates were found broken.
Every secure website proves its identity with a digital certificate. Certificate authorities issue them, and browsers trust those authorities by default.
eMudhra, which says it has issued over 60 million certificates, had private keys for 8 of its certificates compromised. One key was just "4".
With these keys, an attacker can forge a trusted certificate for any website.
But fixes are already rolling out. eMudhra has revoked all 8 certificates, and Firefox, Apple and Microsoft have shipped protection, while some software is still waiting for updates.


Derpino retweeted

Internet encryption is currently having a nuclear meltdown.
Cryptographers are calling it "bigger than Heartbleed."
A global Certificate Authority just leaked 8 master private keys that allow anyone to impersonate any server on Earth (Google, banks, government sites).
A normal master key has 116 digits of entropy.
The actual leaked keys?
4. 56. 66. 115.
A toddler on a calculator could have cracked them.
While browsers patched it today, millions of IoT devices, Linux servers, and Docker containers will take years to clean up.
We bet global digital security on centralized human gatekeepers who forgot to check their math.
True security can't rely on trust cartels. It has to be governed by mathematical consensus.
See the signal. ♾️


Derpino retweeted
Its an easy choice


An important advantage that network cloud can provide to onchain services is better "AI Safety". Here's how.
When AI makes cryptography unsafe, networks can be rapidly upgraded, protecting all hosted software.
With traditional tech stacks, algos are linked into the various layers and components, making upgrading difficult and laborious for those operating services.
Networks, like the Internet Computer/ICP, can abstract the core security math that keeps hosted services safe.
They can also upgrade peripheral (non-core) cryptography.
For example, on a dime, the Internet Computer could could upgrade to a new version of HTTPS in response to AI suddenly making the current version unsafe, without those running services having to do anything.
By contrast, on traditional tech stacks, (or "on" traditional blockchains, where the apps are actually served from traditional tech, such as from AWS, with only tokens a DeFi logic onchain), those running services would need to manually upgrade all their web servers and application servers.
Where the software powering a service makes HTTPS outcalls to other services, it will be directly linked to libraries enabling the calls — so it will all need to be upgraded too!
By contrast, the Internet Computer hosts serverless code, where these kinds of complexities are abstracted away from services. If a service makes an HTTP outcall to another service, the call uses whatever version of HTTPS the network chooses (since the network makes the actual call on behalf of the software). If the network is upgraded, then so is every service — automatically.
This further reflects the way that the Internet Computer as cloud dramatically reduces security admin and systems admin demands compared with building on traditional tech, and additional unique advantages.
It also highlights another crucial axis on which networks must be measured, whether they seek quantum safety (when relevant) or AI safety (since today, AI can now find flaws in algorithms and software at any time) — agility.
That is, how fast can a blockchain network be upgraded in response to a new threat?
The Internet Computer is unique in that it is orchestrated by a decentralized governance system called the Network Nervous System (something like a DAO with system privileges, but much more sophisticated).
That enables the network to be agile, and to rapidly respond to emerging threats, by upgrading the code running on the node machines hosting it. The Internet Computer is a self-updating, adaptive network.
The ability of chains to rapidly react to new threats that have been suddenly uncovered/created by AI, whether they are flaws in cryptography algorithms, or flaws in software libraries, will be a defining feature as things get more hairy.
This is a conundrum for traditional chains chasing quantum safety, of course. By definition, they are claiming that upgrading networks is a long and arduous process, and therefore that they have achieved something important and valuable by upgrading to quantum-safe algorithms ahead of time.
But the algorithms they are upgrading to — so they can claim "quantum safety" — are new and do not benefit from the decades of examination that e.g. ECDSA has.
What then, if AI finds suddenly problems with them, like it did with HAWK?
They have tacitly declared that they cannot quickly switch back, because transitioning is something that takes time, which is why their upgrades are such an achievement...
I will press the point no further, but as an industry, we need to get much more nuanced and sophisticated in how we understand security in an age where AI can suddenly upset security assumptions and make software insecure.
The Internet Computer has got this crucial agility axis covered, and it's agility, not the premature adoption of new and unproven quantum safe crypto algorithms, that really defines safety.
The key point is, if a network has to adopt these unproven algorithms years before a cryptographically-relevant quantum computer exists, then it's doing something very wrong.
The Internet Computer has solved agility. It provides an end-to-end alternative to traditional tech, where people can build services, and gain safety and independence from the rapidly shifting sands of security that the AI era will bring.
It is another reason that the mainstream world needs Internet Computer cloud. It's a security and resilience haven.
Derpino retweeted
🔴 WHAT'S NEXT FOR LLMs?
Today it's primarily text and image generation
THE NEXT PHASE IS BUILD AND DEPLOY WEB APPS. Then run them autonomously.
$ICP ☁️♾
Derpino retweeted

- Revolut
- Lloyds Bank
- Bank of Scotland
- HSBC
- Halifax
- Barclays
Major UK banks and fintech experiencing a significant outage.
Outages are becoming more commonplace.
You need to have a reserve of cash and start using it.


