

Information security | VAPT | OWASP Kathmandu Chapter Leader
Kathmandu, Nepal
Joined December 2012
- Tweets1.6K
- Following508
- Followers1.2K
- Likes2.8K





Oops! retweeted
Introducing Burp AT.
Agentic AI for human-led pentesting, with Burp Suite’s proven tools, your project context, and purpose-built skills.
Now live in public beta for Burp Suite Professional users.
portswigger.net/blog/introdu…

Oops! retweeted

Huge thanks to the @owasp_kathmandu (@Corrupted_brain and the team) for providing me the oppurtunity to share my findings and thoughts with the community. It was a pleasure connecting with everyone there. Looking forward to more such events in the future!
Oops! retweeted

Thank you Ullens College @Bugcrowd @AlteredSecurity @Hacker0x01 @apisecu NCA Nepal Rovix Cloud stickermandu🙏🇳🇵
A huge appreciation to all the amazing speakers, volunteers, & participants who made this event possible! 🎉
We look forward to organizing another event together soon!

Oops! retweeted

Had a really great time talking at @Steel_Con
Giving talks, meeting people, playing games and stuffs. Fun times!


Oops! retweeted
Slides from our (w/@bishal0x01 ) talk at @owasp_kathmandu "Breaching The Perimeter - Our Most Impactful Bug Bounty Findings" is now up. Shout out to the OWASP KTM organizers @smaranchand @Corrupted_brain for another grand event!! 🔥🔥
#BugBounty #owasp
docs.google.com/presentation…

Hack entire datasets rather than playing with prompts.

We scanned 400TB of DeepSeek’s training data & found:
🚨 ~12K live API keys & passwords
🌐 2.76M affected pages
🔄 One key appeared 57K+ times
🔑 219 secret types (AWS root keys, Slack webhooks, etc.)
🔗 Full research: trufflesecurity.com/blog/res…

Security is about keeping risk at a manageable level. You should continuously focus on managing the risks and put controls in place.
Found SolarWinds serv-u vulnerability CVE-2024-28995 using following endpoints to execute LFI. #solarwinds #Pentesting
example.com/?InternalDir=/..…
example.com/?InternalDir=/..…


When you have to meet the compliance requirements and there is no budget from management. #Compliance #GRC

Identified #XSS vulnerability in the #AWS system and reported the issue to the Amazon security team. #pentesting #informationsecurity

5th Chapter Meetup for @owasp_kathmandu has been successfully completed. We are thankful to @CedarGateTech for sponsoring this event. @smaranchand #owasp #infosecurity


Time to present your research at #OWASP Kathamndu. If anyone is willing to travel to Nepal, let's catch up and make it an #infosec tour. 😀

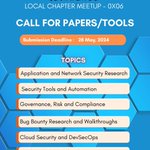
Call for papers! Don't miss this incredible opportunity to showcase your cybersecurity research at OWASP Kathmandu's 5th Meetup. Reach out to @smaranchand and @Corrupted_brain for queries. #infosec #owasp #CyberSecurity

The dark side of large language models: uncovering and overcoming of code vulnerabilities by @javanrasokat at @THREAT_CON #THREATCON_2023 – at Nepal

It's about to start. Nepal's biggest and first cyber security conference. #THREATCON_2023 @THREAT_CON


We're happy to announce our community partner for THREATCON 2023: OWASP Kathmandu
We want to take this moment to express our appreciation for being our esteemed community partner. Thank you for your support in advancing the field of cybersecurity in Nepal.
#THREATCON2023 #owaspkathmandu #Cybersecurity #EthicalHacking #poweredbythreatnix

It was a great talk by @uraniumhacker. Thank you for your time and presence.

Would recommend joining the talks today. Presenting on something @itscachemoney and I have been working on for past few years that we have not presented anywhere yet. 😃
I'll be sharing my insights on "Software Supply Chain Attacks and Preventions" at the @pentesternepal event this Saturday, hosted at Softwarica College, Dillibazar!
