






Cofense Intelligence retweeted

🚨 New “Complaint Stealer” Malware Escalates, Targeting Cryptocurrency Wallets & Hospitality Sector🚨
@CofenseIntel has seen an increase in the last few days in the newly christened #ComplaintStealer malware. Here's what we know so far 👇
cofense.com/blog/new-complai…
Cofense Intelligence retweeted

Major U.S. energy org targeted in QR code phishing attack - @billtoulas
bleepingcomputer.com/news/se…

Cofense Intelligence retweeted
"Human intuition is often much better at recognizing these differences, so training employees to be vigilant against phishing threats is a critical element of good cyber defense."
Another great discovery from @CofenseIntel. Written by @wirelesswench.
bit.ly/45oflAh

Cofense Intelligence retweeted
❗𝗕𝗥𝗘𝗔𝗞𝗜𝗡𝗚 𝗡𝗘𝗪𝗦❗#Emotet has resumed activity this morning, sending emails with attached .zip files that are not password protected.
Learn more below ⬇️
bit.ly/3SSOgj1
Emotet Update: Loader DLLs for #Emotet botnet- (Epochs 4 and 5) have recently been updated, and #malicious #email dissemination may not be far behind! We're anticipating email activity will resume in the next couple of weeks, if not days. Stay vigilant.
#Emotet is back, and reaching inboxes! #Malicious XLS files are attached to emails, sometimes zipped. #Email subjects appear to be taken from email reply-chains. Cofense #Phishing Defense Center has seen multiple instances of Emotet in corporate inboxes this morning. Example:

Cofense Intelligence retweeted
❗NEW #BEC REPORT❗
𝗪𝗵𝗮𝘁 𝗵𝗮𝗽𝗽𝗲𝗻𝘀 𝘄𝗵𝗲𝗻 𝘆𝗼𝘂 𝗴𝗶𝘃𝗲 #𝗕𝗘𝗖 𝘀𝗰𝗮𝗺𝗺𝗲𝗿𝘀 $𝟱𝟬𝟬 𝘄𝗼𝗿𝘁𝗵 𝗼𝗳 𝗴𝗶𝗳𝘁 𝗰𝗮𝗿𝗱𝘀?
That's what @iHeartMalware wanted to find out.
Shocker, they move extremely fast.
Read the full report 📝 bit.ly/3DOURUD
Need to know what's up in the phishing threat landscape? Check out our Q3 Phishing Intelligence Trends Review, out now!
cofense.com/blog/q3-2022-cof…
Cofense Intelligence retweeted
🚨NEW: Scammers Are Targeting Hurricane Relief Funds From FEMA🚨
@iHeartMalware has evidence that shows scammers are actively sharing tutorials and documents with criminal networks on how to steal relief funds from @fema.
Here's what we know ⬇️ bit.ly/3MpizdE
Cofense Intelligence retweeted
Reply-Chain #phishing email found by our Phishing Defense Center (PDC) after it was missed by #Proofpoint.
Reply-chain tactic – using an existing email threat to tack on the #phishing email – gaining trust from the recipient to increase the likelihood of them interacting. (1/4)

Cofense Intelligence retweeted
Microsoft 365 phishing attacks impersonate U.S. govt agencies - @billtoulas
bleepingcomputer.com/news/se…

Ever wonder how a threat actor might selectively target government contractors without even knowing whether the recipient of a #phishing #email is one?
We've got details on a long-standing activity set with convincing lures and #spoofed gov websites ➡️ bit.ly/3qQebui

Cofense Intelligence retweeted
Uber hack updates from @iHeartMalware 👇
VPN credentials compromised via social engineering and hard-coded credentials in scripts led to the compromise of Uber's infrastructure.
Also, make sure you use MFA on your VPN and train your users not to leak VPN credentials. #cybersec
#Lampion malware is back, this time targeting @WeTransfer. We found this #phishing attack in environments using #Microsoft as their standard email security.
@billtoulas @BleepinComputer #malware #cybersecurity

Lampion malware returns in phishing attacks abusing WeTransfer - @billtoulas
bleepingcomputer.com/news/se…

New insights from the team on a unique attack using customer feedback systems that were utilized to launch #phishing attacks. These emails were found by our Phishing Defense Center in environments protected by Microsoft.

Unusual Microsoft 365 Phishing Campaign Spoofs eFax Via Compromised Dynamics Voice Account bit.ly/3TcvHpI by Elizabeth Monalbano #365 #phishing


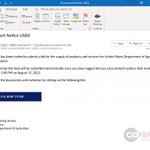
A well-crafted credential #phishing campaign is specifically targeting the food manufacturing industry, spoofing @USDA. Images below are of the original phish and subsequent landing/harvesting pages. @CofenseIntel customers can find details in Cofense ThreatHQ.


Q2 2022 is in the books! We've distilled some of the most important takeaways for you to catch up on between meetings today, but if you want the full picture of today's #Phishing Threat Landscape, there's also a link to download the complete report here: sprou.tt/1j4DJtyrL27
Check out our recently released Business Email Compromise (BEC) study. Cofense Intelligence & @CofenseLabs teams phished hundreds of scammers and gained some amazing insights into their techniques and mindset!
cofense.com/blog/phishing-th…