

Solving problems you didn't know you had. ⬢ @InfinityBotList · @TryByteSend · @FivePRS ⬢ Married to @CallMeAByte & @code ⬢ CEO @NodeByteLTD 🇬🇧
In my Igloo
Joined May 2018
- Tweets1.8K
- Following80
- Followers493
- Likes1.5K



Pixel 🇨🇦 retweeted

I think we've discovered another critical vulnerability:
CVE-2026-BURNOUT: AppSec Professional Exhaustion
Severity: Critical (CVSS 10.0)
Description: A vulnerability affecting security professionals exposed to a continuous stream of critical RCEs, zero-days, emergency patches, and Friday afternoon disclosures.
Impact: Sleep deprivation, excessive caffeine consumption, and an inability to enjoy weekends.
Attack vector: Reading security advisories.
Affected versions: All AppSec professionals, regardless of experience.
Mitigation: No known patch. Air-gapping may delay the inevitable. Total system collapse remains a possibility. 🔥
Pixel 🇨🇦 retweeted

Thank you, Alberta!
I’m very pleased to see the initial results from Elections Alberta show widespread support for remaining in Canada. Albertans have voted for a stronger Alberta in a united Canada.
Thank you to all Albertans who took time to vote on these critically important referendum questions.
Tomorrow evening, October 20, I will address Albertans live at 6:45 p.m. to discuss the results of all referendum questions for which results are available, and where our province goes from here.

Pixel 🇨🇦 retweeted

The PHP Foundation says Chainguard unilaterally broke the embargo and published built images containing the critical RCE fixes more than six hours early:
“This disregarded weeks of work by many parties toward a coordinated disclosure.”
socket.dev/blog/php-embargo-…

Pixel 🇨🇦 retweeted

⚠️ Vulnerability alert: php2shell
Unpatched sites running PHP 5.4 or later are at risk of remote code execution, data exposure, and crashes.
If your site’s web traffic is proxied through Cloudflare, we deployed protections before official public disclosure. Check the blog post to see which mitigations are enabled by default.
Even with these mitigations in place, update PHP as soon as possible to fix the underlying vulnerabilities.
xitter.cf/Cloudflare/status/2112…

Cloudflare has deployed default web application firewall (WAF) protections for newly disclosed PHP vulnerabilities before public disclosure. The rules use request and response signals to stop exploit attempts and prevent exposed data from reaching attackers. cfl.re/488w8dc

Pixel 🇨🇦 retweeted
Archive.org is currently offline. We are working to restore service now.
Pixel 🇨🇦 retweeted

Security called me at 6:12 AM today.
"Patch every PHP server immediately."
I asked what happened.
"Two critical vulnerabilities. Remote code execution. No authentication required."
Cool.
How many PHP servers do we have?
According to inventory: 12
According to reality:
Nobody knows.
We found one running WordPress.
Three running old internal tools.
One under someone's desk.
Two inside vendor appliances.
A forgotten employee directory from 2016.
And a server named:
PHP-OLD-DO-NOT-TOUCH
Naturally, that one runs payroll exports.
Then we found a PHP 5.6 box.
I asked who owned it.
The documentation said:
BRIAN.
Brian left in 2019.
We called Brian.
He said:
"Oh wow, that's still running?"
Excellent.
By 8 AM, leadership joined the incident call.
CEO:
"Can hackers actually get in?"
Security:
"Potentially yes."
CEO:
"Without a password?"
Security:
"Yes."
CEO:
"Then why do WE need passwords?"
Not the lesson.
Finance asked if we could wait until the weekend to patch because downtime affects revenue.
Security explained that the alternative was letting strangers execute code on our servers.
Finance asked for a cost comparison.
At 9:17, someone suggested temporarily taking the vulnerable websites offline.
Marketing refused.
"Our campaign is live."
So for the next hour, the company officially decided maintaining a landing page for 20% off webinar registration was more important than preventing remote server takeover.
We finally patched everything we could find.
Then our scanner discovered another PHP server.
Hostname:
TEMP-PHP-2014
Uptime:
4,512 days.
Nobody knows what it does.
Nobody owns it.
Nobody can shut it down.
But every time we block network access, the warehouse stops printing shipping labels.
Security has classified it as critical infrastructure.
It is running PHP 5.4.
The vulnerability has existed longer than half our employees.
The emergency patch took four hours.
Finding out what PHP actually runs took eleven.
The internet isn't held together with code.
It's held together with servers everyone is afraid to turn off.
Pixel 🇨🇦 retweeted

Leaving this here, PHP 8.5.12 security patch is incomplete. ( needs further validation )

Readers added context they thought people might want to know
Unvalidated AI output (author admits in replies: omp with glm5.3 + ds4), not a lab result. Its screenshot says both CVEs are fixed; the 'surviving paths' need unserialize() of attacker data or an app LFI. Patch per php.net: php.net/archive/2026.p…


Pixel 🇨🇦 retweeted

You can finally SEND AND RECEIVE emails with ByteSend 👀 it’s pretty awesome check out the new release notes 👇
bytesend.cloud/changelog#v0.…


Pixel 🇨🇦 retweeted

You when you buy a Minecraft or a FiveM server from Nodebyte Hosting
nodebyte.host/


Pixel 🇨🇦 retweeted

We have just launched our rebuilt Billing Panel!
This is built on top of our existing billing backend and overtime we will be shifting into our new backend!
What's new:
- A faster, cleaner client area for services, invoices, support tickets and your account, designed to work properly on mobile too
- A new store and checkout with clearer plan options and pricing
- Looking Glass Test your connection to each of our locations from your browser, plus download test files, so you can pick the best location before you buy
- Object Storage manager Browse, upload and share files, manage access keys and bucket settings, all from the panel
- Language support The panel follows your chosen language
Come check it out!
billing.nodebyte.host/
#Hosting #GameHosting

Pixel 🇨🇦 retweeted

Two new recipes have been added to the txAdmin recipes list, the RTS-style multiplayer game mode Warfare Tactics V, and the vMenu tools for server owners — both created in collaboration with FiveM community developers.
Read more on our forum: forum.cfx.re/t/5427091

ALT Rockstar Games and Cfx poster with text reading: \"txAdmin Game Recipes: vMenu Enhanced and Warfare Tactics V\"
Pixel 🇨🇦 retweeted

There is so many new ways for you to share and grow on Omniplex:
• Bot Listings
• Server Listings
• Profile Themes
• Emoji Packs
• Sound packs
And more.
omniplex.gg

Pixel 🇨🇦 retweeted
We just dropped our largest update since the release of the new site 👀 check it out
omniplex.gg/blog/v0-1-3-serv…

Pixel 🇨🇦 retweeted

🚨 A single "edit" permission is all it takes to become a Kubernetes god-mode admin. Here's how CVE-2026-10090 breaks Red Hat ACM wide open.
Full story: cybersecuritynews.com/red-ha…
#cybersecuritynews

ALT Red Hat ACM Privilege Escalation Vulnerability Lets Attackers Gain Full Cluster-Admin Access.
Pixel 🇨🇦 retweeted

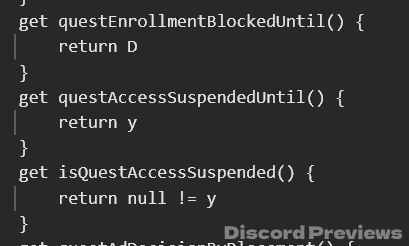
Discord is working on new systems to automatically restrict access to Quests if users are found to automate them.
Recent client updates include logic to handle temporary suspensions for Quests.
Pixel 🇨🇦 retweeted
📣 The moment is here. 📣
TypeScript 7 is officially released! 7️⃣
devblogs.microsoft.com/types…

Pixel 🇨🇦 retweeted
Celebrate the 4th of July week with 25% OFF ALL HOSTING SERVICES across our entire catalog!
From high-performance game nodes to dedicated virtual private servers, level up your infrastructure for less.
💥 Use code: MAGA2X26
⏳ Ends July 11th!
👉 billing.nodebyte.host

Pixel 🇨🇦 retweeted

Canada Day with my favourite person @CodeMeAPixel ❤️🍁 We celebrate the country we call home while honouring the Indigenous Peoples who have cared for these lands since time immemorial and acknowledging the harms of colonization. #CanadaDay #TruthAndReconciliation
