
Cybersecurity Community || Training || Mentoring || Consultancy || Security Audit
Accra, Ghana
Joined January 2025
- Tweets4.3K
- Following6
- Followers2.8K
- Likes4.6K




ClickSafe Community(CSC) retweeted

Data Science Full Course ✅
drive.google.com/drive/mobil…
ClickSafe Community(CSC) retweeted
SANS Holiday hack challenge is open now.
Don’t miss out.
lnkd.in/p/d3hbJT3K

ClickSafe Community(CSC) retweeted
Take advantage of this now.
58% discount is huge.

I'm running a FREE CCNA Cohort one Last TIME, so let's make it BIG!
Get Credly verified badges from Netacad and 58% discount voucher.
IT'S 𝙱̶𝙻̶𝙰̶𝙲̶𝙺̶ BRIGHT FRIDAY!!!
What It includes:
1. Netacad Registration in CCNA ITN
2. Pass it and get promoted to CCNA SRWE
3. Pass it and get promoted to CCNA ENSA
4. pass it and get 58% Discount Voucher
Register here: LearnWithMoosa.com/ccna-free

ClickSafe Community(CSC) retweeted
When you create an account, the website takes your password and runs it through a mathematical blender called a hashing algorithm.
This process turns your password into a unique, random-looking string of letters and numbers called a hash.
The website throws away your real password and saves only this scrambled hash in its database.
Because this process only works one way, nobody can reverse the scrambled code back into your original password.
Later, when you try to log in, the website takes whatever password you type and runs it through that exact same mathematical blender.
It then compares the newly scrambled code with the original hash saved in its database. If you typed the right password, both hashes will match completely and let you in.
If you missed even a single letter, the scrambled code changes entirely, so the website knows right away that your password is wrong

ClickSafe Community(CSC) retweeted
Which OSI layer do routers use to forward packets based on IP addresses?
A) Layer 2 (Data Link)
B) Layer 3 (Network)
C) Layer 4 (Transport)
D) Layer 7 (Application)
ClickSafe Community(CSC) retweeted
Explanation:
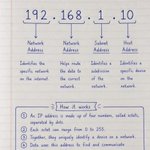
B) /24 (255.255.255.0)✅
A /24 subnet provides 256 total IP addresses, leaving 254 usable addresses after subtracting the network and broadcast addresses.


ClickSafe Community(CSC) retweeted
For Hands-On Labs & Packet Analysis Focus for Network Engineers
Thank me later
containerlab.dev
clab.netlab.tools
malware-traffic-analysis.net
subnettingpractice.com
bgp.he.net
Bookmark & repost!

ClickSafe Community(CSC) retweeted
Place a Word document named 2026-Salaries-and-Bank-Details.docx containing a hidden tracking pixel (from Canarytokens) in your cloud drive so you get an instant email with the attacker's IP address the second someone opens it.
ClickSafe Community(CSC) retweeted
Hackers no longer need your password or your 2FA code if malware steals your active browser session cookie, allowing them to clone your logged-in session instantly.
How are you protecting your session tokens right now?🥴


ClickSafe Community(CSC) retweeted
🧵 Good search engines obey your website's robots.txtfile. Hackers and vulnerability scanners use it as a treasure map.
Here is how to turn robots.txt into an automated honeypot that instantly bans bad bots at your firewall:
ClickSafe Community(CSC) retweeted
📌 Step 4: Activate the firewall ban
Add the jail rule to /etc/fail2ban/jail.local:
[nginx-honeypot]
enabled = true
port = http,https
filter = nginx-honeypot
logpath = /var/log/nginx/access.log
maxretry = 1
bantime = 86400
Restart Fail2Ban (sudo systemctl restart fail2ban). Now, any bot that touches your bait URL gets banned for 24 hours on the first try
Retweet to share this defense trick with other builders, and follow @CyberRacheal for more!

ClickSafe Community(CSC) retweeted
Linux Resources 👇🏽
Introduction to Linux : youtu.be/6yoVC6IPpQU
Linux Command line: youtu.be/6L-EBZL66Rw
Managing Users and Groups : youtu.be/6L-EBZL66Rw
Retweets, ❤️ and bookmark for future.
Linux Resources 👇🏽
Introduction to Linux : youtu.be/6yoVC6IPpQU
Linux Command line: youtu.be/6L-EBZL66Rw
Managing Users and Groups : youtu.be/6L-EBZL66Rw
Retweets, ❤️ and bookmark for future.