

Conference on Applied Machine Learning for Information Security
Washington, DC
Joined September 2017
- Tweets539
- Following52
- Followers1.2K
- Likes182





Camlis Org retweeted

Paper coming soon @CamlisOrg @CrowdStrike


Our last talk of Day 1! "Inherited Circuits, Learned Semantics: How Fine-Tuning Creates Evasion Vulnerabilities Invisible to Standard Evaluation" from Ryan Fetterman looks at how fine-tuning might overfit to token-level features.

Third talk of the Malware track: David Ion from CrowdStrike presents "Euclidean Embedding of TLSH Digests" -- how can you get TLSH-like matching scores in an ML-friendly metric space?

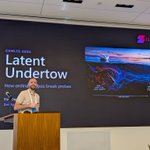
Our second talk of the session is "Latent Undertow: How Ordinary Typos Break Probes" from Elad David -- how simple typos break hidden-state probes without modifying LLM intent or response.


Our first talk of session 2 starts with the inimitable Edward Raff: "Trouble With Time: Compile Timestamps and First-Seen Date Regression in EMBER2024" -- time-splitting is critical for good malware evals, but how might we do it without external sourcing? Watch and find out!

Our second session of day 1 -- Malware analysis -- starts in just a few minutes!
Follow the livestream here! camlis.org/event-registratio…

Our last talk of the Agents for Security session: Wayne Fullen brings us home with "RuleForge: Automated Generation and Validation for Web Vulnerability Detection at Scale"

Talk 3 of our Agents for Security session is Diane Lin: "Robustness in the Gray Zone: Securing AI Agents via Semantic and Episodic Memory against Boundary-Search Attacks" -- framing LLM consistency as adversarial robustness. Livestream it at camlis.org/event-registratio…

Talk two of our Agents for Security session is starting; John Seymour presents "Citadel: A Maintained, Queryable Grounding Layer for the SOC" -- continuous generation of telemetry maps for agents and analysts. What do you do with "20+ logging platforms"?

Remember, you can watch most of our talks online at camlis.org/event-registratio… !
Our first session on Agents for Security kicks off with Arjun Chakraborty presenting "CTI-REALM: A Benchmark to Evaluate Agent Performance on Security Detection Rule Generation Capabilities" -- how well does your agent support detection engineering? Watch and find out!

