

An information technology company, committed to providing clients with greater efficiencies that center on people, platform and processes with proven results.
Joined August 2017
- Tweets1.9K
- Following200
- Followers90
- Likes72





Unpatched systems create unnecessary business risk.
Risk-based patch management helps close security gaps, accelerate remediation, and reduce exposure before vulnerabilities are exploited.
#PatchManagement #CyberSecurity #RiskManagement

Cybersecurity risk doesn't stop at your network perimeter.
Vendors, SaaS providers, and external integrations can introduce new exposure.
Strong third-party risk management helps organizations protect interconnected environments.
#ThirdPartyRisk #CyberSecurity #RiskManagement

Identifying vulnerabilities is only the first step.
Prioritizing risk and accelerating remediation help organizations reduce exposure before threats are exploited.
#VulnerabilityManagement #CyberSecurity #RiskManagement

Access is a security control.
Excessive permissions and unmanaged privileges increase risk. Least-privilege access helps ensure users have what they need and nothing more.
#LeastPrivilege #CyberSecurity #ZeroTrust

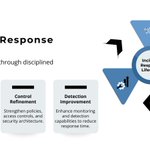
Incident response doesn't end with containment.
Identifying root causes, refining controls, and improving detection help turn each incident into stronger security operations.
#IncidentResponse #CyberSecurity #CyberResilience

Every endpoint is a potential entry point for cyber threats.
CDA helps organizations strengthen endpoint protection, improve threat detection, and reduce security exposure across the enterprise.
#EndpointSecurity #CyberSecurity #ThreatDetection

Strong security isn't defined by the number of tools deployed.
It depends on whether controls are consistently applied, validated, and supported by day-to-day operations.
CDA helps build security that operates.
#CyberSecurity #SecurityOperations #RiskManagement #EnterpriseIT

Security improves when ownership is clear.
Strong governance creates accountability for risk, remediation, and results. Turning security priorities into measurable action.
#CyberSecurity #SecurityGovernance #RiskManagement #GRC

Today, we remember the lives lost on September 11, 2001, and honor the courage of the first responders, service members, and everyday Americans who answered in the face of tragedy.
We remember their sacrifice, their courage, and the unity that followed.
#September11 #NeverForget

You can’t respond to what you can’t see.
Security visibility helps teams detect threats sooner, understand risk, and respond before issues become larger disruptions.
#CyberSecurity #SecurityVisibility #ThreatDetection #IncidentResponse #EnterpriseSecurity

Security tools are only as effective as the environments they're configured to protect.
Strong security baselines and consistent configurations help reduce attack surface and unnecessary exposure.
#SecurityHardening #CyberSecurity #EnterpriseIT

Access should be based on what users need not what they've accumulated over time.
Strong identity and access controls reduce unnecessary exposure while improving visibility and accountability.
#IdentityAccessManagement #CyberSecurity #ZeroTrust

Strong cybersecurity requires more than technology—it requires governance. Clear accountability, aligned priorities, and measurable controls help turn security strategy into action.
#SecurityGovernance #CyberSecurity #RiskManagement #SecOps

Finding vulnerabilities is only the beginning. Effective vulnerability management means prioritizing findings based on risk and driving them through remediation...not simply identifying them.
#VulnerabilityManagement #CyberSecurity #RiskManagement #SecOps

Third-party risk is business risk.
Strong vendor governance helps organizations reduce exposure, strengthen resilience, and support compliance.
#ThirdPartyRisk #CyberSecurity #Governance #Risk #Compliance #GRC

The best time to prepare for a cyber incident is before it happens.
Effective incident response planning reduces downtime, strengthens resilience, and improves organizational readiness. #IncidentResponse #CyberSecurity #BusinessContinuity

You can't reduce risk you haven't identified.
#Security assessments help organizations prioritize #vulnerabilities, strengthen #governance, and make informed security decisions. #RiskManagement #CyberSecurity #Compliance
criticaldesign.net/cybersecu…

Stolen #credentials, #phishing, and excessive privileges remain common paths into enterprise environments. Protecting identities with #MFA, least privilege, and continuous #monitoring helps reduce #risk before an incident occurs.

Celebrating 250 years of freedom and honoring all who have served to protect it.
From everyone at @CDA_Critical, have a safe and wonderful Fourth of July!
Happy 250th Birthday, America!
#America250 #FourthOfJuly
Security readiness is operational.
It's built through visibility, validated controls, tested response plans, and continuous improvement—not just more security tools.
Is your organization prepared to respond and recover?
#CyberSecurity #ZeroTrust #CyberResilience
