

Offensive Web Application Security Software
Joined May 2018
- Tweets839
- Following9.7K
- Followers19.1K
- Likes1.3K




Pinned Tweet
Burp Bounty Pro 4.0.0 is here.
Burp Bounty Go's capabilities are now integrated into Pro. We're also introducing Burp Bounty Server for standalone scanning, REST integrations and AI agents through MCP.

"Test only this parameter with SQLi profiles. Cap traffic at 30 RPS. Summarize the findings."
Connect your AI agent to Burp Bounty Server through MCP to discover profiles, run scans and retrieve evidence.
bountysecurity.ai/pages/burp…

Burp Bounty Server runs on your machines and VPSs. Connect an AI agent through MCP to discover profiles, launch scans and retrieve findings.
Available standalone. Included with Pro.
One user. 10 registered activations.
With Pro, those activations are shared across Pro and Server. Bring your scanning workflow to your laptop, servers and AI agents.
Explore 4.0.0:
bountysecurity.ai/pages/burp…
Think about a bug you found last year because you tried something your usual checks missed.
An unusual parameter. An unexpected encoding. A payload you adapted after one small detail.
How often have you tested for that same pattern since?

Good techniques end up scattered across notes, old reports and Repeater tabs.
Burp Bounty Pro turns them into custom scan profiles. Define payloads, insertion points and match conditions once.
🎁 15 days free → bountysecurity.ai/pages/cont…
We took August off. Back today, new season starts now.
Before the break: AI Scanner in v3.1.0, five LLM providers, six new AI/LLM passive profiles, and you told us to build an MCP server. So we did.
What's next: the MCP server so an agent can drive BBP directly, more AI security profiles, and Tuesday/Thursday content back on schedule.
New here? 262 profiles, 28 Smart Scan rules, AI targeting, 15 days free 🪶
🎁 bountysecurity.ai/pages/cont…
Put a number on your hour, then ask what you're spending it on.
Hunting? One finding you wouldn't have reached covers the tool many times over.
Consulting? Every hour of manual fuzzing is expert rates billed for mechanical work.
Users have reported a £5,000 dependency confusion bounty, path traversal to full server takeover, SQLi escalated to RCE.
No promises, nobody can guarantee a bounty. But the routine work has a price and you're already paying it.
🎁 15 days free → bountysecurity.ai/pages/cont…
Most scanners inject payloads in 2 places: URL params and body params.
The interesting bugs hide where they don't look.
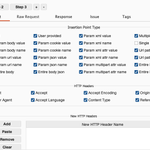
Burp Bounty Pro injects into 30+ insertion point types, and each profile picks exactly which to test.
Parameter names (not just values). Path folders and filenames. Cookies. JSON keys. XML attributes. Host, Origin, X-Forwarded-For and any custom header.
The same payload is a different test in each spot. Often only one lands
🎁 15 days free → bountysecurity.ai/pages/cont…
The pentesters who build a reputation aren't the ones who run the most scans.
They're the ones who find what everyone else walked past.
You can't do that if your hours are spent manually fuzzing every input by hand.
Burp Bounty Pro takes the mechanical work off your plate. Every parameter, every insertion point, every payload fired across the target.
The freed-up focus goes into the findings nobody else got to
🎁 15 days free → bountysecurity.ai/pages/cont…
Every pentester knows the feeling.
You've sent the report. The engagement is closed. And a voice in the back of your head asks: did I miss something?
That doubt is the worst part of the job.
Burp Bounty Pro fuzzes the inputs you'd otherwise test by hand. Every parameter, every insertion point, every payload against every relevant endpoint.
Close engagements knowing the parameter surface was covered.
🎁 15 days free → bountysecurity.ai/pages/cont…
How many hours of your last engagement did you actually spend hunting?
Not configuring. Not waiting on scans. Not reading output to confirm what you already suspected.
Actually hunting.
For most pentesters: "less than I'd like."
Burp Bounty Pro runs the routine testing in the background while you do the part that needs a brain. Come back to findings already triaged, not a blank target.
Some users save entire days per engagement
🎁 15 days free → bountysecurity.ai/pages/cont…
You didn't get into security to run the same manual checks on every target.
You got into it to find the bug nobody else found.
We're in the age of AI. The move: let the machine clear the routine, aim your skill at the bugs only a human catches.
That's what Burp Bounty Pro is for. Users have found path traversal → server takeover, SQLi → RCE, chained SSRF, a £5k dependency confusion bounty.
The tool does the grinding. You do the hunting
🎁 15 days free → bountysecurity.ai/pages/cont…