


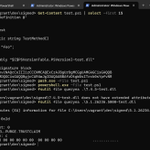


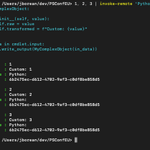
It's been a long time coming but PSWSMan v3 for #PowerShell has been released powershellgallery.com/packag…. This is a major upgrade that moves away from the C omi library to a C# WSMan stack. No more root required, better Enter-PSSession experience, and lots more features enabled.

Big shout out to @DevolutionsInc for sspi-rs github.com/devolutions/sspi-… which PSWSMan ships with and can optionally use. It provides a consistent Kerberos/NTLM stack across the various platforms and have been very quick to fix up any bugs I've encountered when integrating it.

I've always disliked that I couldn't test Kerberos in CI easily and so I've written a #PowerShell module called Obol that can setup a KDC and configure the environment for the platform you are on github.com/jborean93/PowerSh….


Anyone interested in yet another attempt at trying to enhance splatting in #PowerShell. I've tried to collate all the options proposed over the years with their pros/cons. Hoping to get any community feedback before trying to champion a proper RFC github.com/jborean93/PowerSh….

Did you know it is possible to use Kerberos keytabs on SSPI. I've released a version of sspilib for #python that exposes this in a friendly way through the SEC_WINNT_AUTH_IDENTITY_EX2 struct
cred = sspi.KeytabCredential("[email protected]", "kerb.keytab")
github.com/jborean93/sspilib…

Jordan Borean retweeted

A new article in my blog: tbt.qkation.com/posts/rpc-en…
This is the longest post I've ever written (so far). This is a deep dive into Kerberos RPC encryption: how it works and how to implement it.
So, if you ever wondered (most likely not) about such things, this is your chance. 😉

Jordan Borean retweeted
So Windows 11 Insiders Build introduces `Administrator Protection`... And (to my surprise) no changes were needed on gsudo to work on it!
techcommunity.microsoft.com/…

Just pushed a new version of my #Ansible debugging tool ansibug. This new update fixes support for restarting a launched debug session but also adds support for breakpoints for task failures, unreachable hosts, or skipped tasks github.com/jborean93/ansibug
For anyone interested in making Azure Trusted Signing a good fit for #PowerShell signatures please have a look and add +1 or comments if you think of anything else to github.com/PowerShell/PowerS… so the team can see how important this would be to have.


Pushed a new version of my #PowerShell module OpenAuthenticode github.com/jborean93/PowerSh…. It adds support for signing using Azure's Trusted Signing service. I've found it has been pretty easy to setup as an individual to use but a pity pwsh's trust model won't work nicely with it.

ALT PowerShell, certificate, and signature output showing how the key is retrieved and used by the OpenAuthenticode cmdlets.
Jordan Borean retweeted

If you missed the webinar, here is the video recording for "Decrypting RDP Traffic in Wireshark"! The slides are great, but the one-hour presentation is even better: youtube.com/watch?v=VUHucXiM…
Pushed a new version of my #PowerShell module OpenAuthenticode github.com/jborean93/PowerSh…. It adds support for signing using Azure's Trusted Signing service. I've found it has been pretty easy to setup as an individual to use but a pity pwsh's trust model won't work nicely with it.
ALT PowerShell, certificate, and signature output showing how the key is retrieved and used by the OpenAuthenticode cmdlets.
I've opened a #PowerShell RFC to set environment variables for sub processes like the 'FOO=bar command' functionality on sh based shells github.com/PowerShell/PowerS…. If you are interested, it would be great to get some feedback around the proposed syntax or potential alternatives.

Does anything know what the fileHashList and authenticodeHashList represents in Azure Trusted Signing sign operation? How would I have multiple files with 1 digest or even the authenticode signature before signing github.com/Azure/azure-rest-…
I have a security vulnerability to report to Microsoft. I’m wondering if there are any recommendations or things to do first from someone who has gone through the process.
Ever wanted to know what data #PowerShell or other programs send to AMSI. I wrote a C# COM server implementation that logs this data as a JSON string. Had some fun learning more about COM and .NET AOT with this little project github.com/jborean93/AmsiPro…

Had some fun working with a challenge posed by @awakecoding. A POC that can run multiple #PowerShell named pipe instances with custom pipe names. Usually you have to start a new process but this can be done in proc. Non-public APIs so not production code gist.github.com/jborean93/43…

Can anyone explain this behaviour before I dig into the SIP code. #PowerShell's authenticode signature hashes the contents based on the UTF8 encoding unless the script is more than 33 characters AND a non-ASCII character is present after the 32nd character in which it uses "ANSI"

I'm hoping to add an automatic CancellationToken property to #PowerShell functions. If anyone is interested in this I would love any thoughts on the RFC github.com/PowerShell/PowerS… and possible implementation of this RFC github.com/PowerShell/PowerS…

Jordan Borean retweeted
Friendly Reminder: If you have admin privileges but lack the necessary file permissions, you can leverage the SeBackup/SeRestore privileges directly from cmd.exe! There’s no need to elevate to LocalSystem, duplicate TrustedInstaller, or use similar methods. Simply enable the required privileges in your token, and you’re good to go.
Here are a few key points to keep in mind:
1. This approach addresses ERROR_ACCESS_DENIED, not ERROR_SHARING_VIOLATION. Note that elevation won’t resolve sharing violations anyway.
2. If you use a separate tool to enable privileges, it must modify the token of its parent process, not itself. Alternatively, the tool can adjust its own token and then launch a new instance of cmd.exe, which will inherit the updated token.
3. You can achieve the same functionality with PowerShell, but in this case, the script must manipulate its own token.
For convenience, you can use a ready-made tool that enables all available privileges, not just those related to Backup/Restore. This makes it more versatile. github.com/gtworek/PSBits/tr…
