

"Find out what makes you kinder, what opens you up and brings out the most loving, generous, and unafraid version of you." -George Saunders I like the corn. 🟠
Joined June 2018
- Tweets6K
- Following1.8K
- Followers2K
- Likes119K




oh

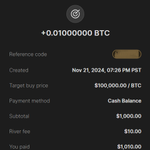
Cash App is building a way to buy a whole bitcoin and spread the cost over a set repayment period
if i had financed ₿1 on august 1, i'd have locked it at $62,275
bitcoin is $81,500 today
that's $19,225 up in 68 days
to not be worth it, the interest so far would need to top 166% a year
a whole bitcoin used to mean stacking ₿ for years
soon you'll be able to finance it


Boiler retweeted

Some things don't make sense.
Bitcoin does.
block.xyz/bitcoin/does
Boiler retweeted

how can you not believe in God when octopuses DREAM and otters have a favorite rock they carry around in a little SKIN POCKET and cows have BEST FRIENDS and bees are out there communicating the coordinates of flowers through INTERPRETIVE DANCE and they have REGIONAL DIALECTS??
cats are PURRING at frequencies associated with bone healing??? forests get absolutely incinerated and respond by growing FLOWERS??? dolphins literally invent NAMES for themselves and yell them across the ocean??? penguins are waddling around Antarctica looking for the PERFECT LITTLE ROCK to give their beloved???
CROWS REMEMBER YOUR FACE. THEY TELL OTHER CROWS ABOUT YOU. THEY TELL THEIR CHILDREN ABOUT YOU. YOU CAN HAVE GENERATIONAL BEEF WITH A BIRD.
goats have ACCENTS. rats GIGGLE when you tickle them. elephants mourn their dead. whales make SONGS and then OTHER WHALES LEARN THE SONG and suddenly everybody across the ocean is singing the new hit single.
monarch butterflies are born knowing how to fly thousands of miles to a place THEY HAVE NEVER BEEN. sea turtles hatch out of an egg, immediately sprint toward an OCEAN they have never seen, disappear into it for like THIRTY YEARS and then somehow come back to THE SAME BEACH???
birds can see COLORS THAT WE CANNOT SEE. there are colors happening RIGHT NOW that we don’t even get to know about.
there are sea slugs that eat algae and STEAL ITS CHLOROPLASTS and then are just like great thanks I’ll be PHOTOSYNTHESIZING NOW. there are mushrooms communicating underground. there are seeds sitting in the dirt for DECADES like no actually I will wait.
squirrels plant MILLIONS OF TREES because they simply cannot remember where they put their snacks.
A CATERPILLAR GOES INTO A LITTLE BAG, DISSOLVES MOST OF ITS BODY INTO ORGANIC SOUP, REARRANGES ITSELF, GROWS WINGS AND LEAVES.
and you’re telling me a tiny acorn knows how to become a 70-foot oak tree??? nobody tells it what to do??? it just has TREE INSTRUCTIONS INSIDE IT???
your body started as ONE CELL. ONE. and that cell divided itself into a brain that can think about its own existence and eyes that can look at stars and hands that can hold somebody else’s hands and a heart that runs on ELECTRICITY without you even asking it to???
the iron in your BLOOD was made inside a STAR.
I’M SORRY?????
we are walking around on a wet rock covered in bioluminescent oceans and singing whales and laughing rats and birds holding lifelong grudges and flowers exploding out of FIRE and somehow we’re supposed to act like this is a normal place to live?????????

how can you not believe in God when octopuses dream, otters have a favorite shell that they carry all their lives, cows have best friends, bees have different "dialects" of dance depending on the region, cats purr at a frequency that accelerates bone healing, the forest grows flowers first after a fire, dolphins give each other names and respond to them, penguins make proposals by giving each other the most beautiful pebble, crows will tell their children about you, goats have accents, rats giggle when you tickle them, sea slugs become powered by the sun just by green algae and squirrels plant millions of trees every year just by forgetting where they've buried their nuts!
Boiler retweeted

If you believe the risk is coming from 1-3 people in a garage with no money and no compute, you just don't understand this technology and haven't learned anything this summer.
Risk comes from the asymmetry of capabilities created by secret labs training frontier agents and running them with massive amount of compute. Open-source is exactly the solution to this asymmetry and empowers hospitals (and any smaller orgs) to defend themselves!

We're used to thinking of open-source models as an unadulterated good. But in the case of AI, they can actually pose additional dangers, as @ReidHoffman and I got into at #CGI2026. I appreciated this nuanced discussion.
Boiler retweeted

Shielded Bitcoin:
You peg BTC into a private bucket of encrypted notes. Move it around with zero-knowledge proofs so nobody sees sender, receiver, or amount. Later you peg out to a fresh address, on-chain link is gone.
Same mixer logic as Tornado Cash:)
No soft fork. No operators. Bitcoin just stores the receipts.


Boiler retweeted
JUST IN: East Texas A&M University students announce they've built the first post-quantum security solution for the Bitcoin Lightning Network 👀

Boiler retweeted

Thanks for the careful review. This is the kind of discussion necessary for making progress on post-quantum Bitcoin.
There's a lot here I agree with, though I come to a different conclusion. I agree that hash-based signatures are a good fit for Bitcoin, for the reasons the review gives. Reducing block space usage is indeed a primary design goal of SHRINCS, and it comes at a cost. The stateful path's safety depends on wallet infrastructure that the protocol does not prescribe and that still needs standards.
I also agree that if block space stays cheap, the stateful path adds complexity for little benefit. But that seems unlikely, since today's fees reflect 64-byte signatures, and stateless SHRINCS signatures are about 90 times larger. High fees matter for a store of value too, because holders eventually need to spend, and we should aim for Bitcoin to remain usable by people who don't hold large amounts.
Congestion and high fees are a strong argument for minimizing signature size, and stateful signatures are up to about 10 times smaller than stateless ones. Wallets can start with stateless signing and enable stateful signing for their existing keys later, without another soft fork. A block-size increase can't fully solve this. Every node has to download and validate every block, so blocks can't grow arbitrarily large.
The review suggests that the stateful path lets the SHRINCS authors say the block-size concern has been addressed. The intent is rather that SHRINCS doesn't depend on a block-size increase, so that question can be discussed separately without holding up post-quantum signatures.
On custody, I agree that it's unreasonable to expect replicas to share stateful signing slots safely. Some high-availability setups can still use the stateful path, for example one where a designated signer signs statefully while the replicas sign only statelessly, so failover costs larger signatures but requires no coordination of state. In practice, custodians may simply sign statelessly.
The review describes stateful signing as an optimization, which fits better than the BIP's "primary path" wording. It also made me realize that calling the stateless path a "fallback" is misleading, and we're considering changing the terminology in the BIP.
The review proposes considering a stateless-only scheme with a larger block size. Modified algorithms could reduce stateless signatures to roughly 4,000 bytes, about 60 times the size of a Schnorr signature instead of 90. Would that be worth departing from the SLH-DSA algorithms?


Boiler retweeted

i deleted instagram about 5 years ago, so i had almost forgotten what it feels like to have it in your life
watching people around me use it now feels strange
you end up checking the daily lives of people you haven’t seen in ten years, people you probably wouldn’t even stop to talk to if you crossed them on the street.
random people from your past become permanent background characters in your mind.
then add the fact that a huge part of instagram is effectively a dating product
if you’re already in a long-term relationship, keeping that constant stream of attention, comparison and other people’s lives in your head has destroyed countless couples
after being off it for years, the whole thing looks much more extreme from the outside. – at Barcelona, Spain
Boiler retweeted

Charlie Munger had a simple rule for toxic people:
“Get them the hell out of your life - and do it fast.”
Who you surround yourself with matters much more than you think.

Boiler retweeted

I’m a retired brain surgeon and I wanna tell you why you feel like life is passing by. I just need one minute to explain this to you so hang in there.
Repetitive daily routines stop the brain from recording clear detailed memories. When every day looks the same, your brain does not track time the same as a clock does. It tracks change. If nothing new happens then days, months, and years start to blur together.
This is know as Time compression. When life lacks variety, your brain compresses past days together, making it feel like time is sped up.
To stop feeling like life is passing you by, add new experiences to your life. Break routine habits, like changing your daily home routine, taking a different route to work, or trying a new hobby.
Schedule small trips or plan new adventures so your days do not blend together.
Practice mindfulness by staying fully focused on what you are doing right now and not trying to race off to the next task.
Keep a journal and write down happy memories or memorable parts of the day before you go to sleep.
Take deep, calm breaths when you feel anxious or rushed to return your focus to the moment.
You can and you will retrain your brain to not feel like life is passing you by by following these few simple measures.
Boiler retweeted

My life got a lot better when I started leaving my phone at home. Often. As a default. Go to the gym without it. Go to dinner without it. Take a walk without it. Go to a museum without it. At first, you will start to come up with justifications for why you can’t do this. But once you overcome them, you will start to experience a wonderful mix of creativity & happiness as you unshackle yourself from your handheld dopamine casino.
Boiler retweeted

Underrated life advice: Have more hobbies and fewer opinions. The happiest people I know spend less time discussing what everyone else is doing and more time doing things themselves.
Boiler retweeted

Fiat currency ultimately trends to zero. The State will always find a way to shave off the edges of gold coins, then decouple money from the gold standard, and eventually just make up out of thin air what money is worth.
Even physical coins are just plated steel these days: basically using the 2nd most common metal found in the Earth's crust (iron), rather than the precious metals (gold, silver) coins used to be made of.

Boiler retweeted

A 14th proposal dropped on Part 3.
It's the first one that actually answers the question I got most: "what can I do today without betting on a soft fork?"
Daniel Buchner (@csuwildcat) published a draft BIP on April 10 that uses a corner of BIP 342 nobody was really using. Tapscript already treats any non-32-byte public key as an "unknown type" and any non-empty signature element as successful. That corner was left deliberately open so future soft forks could add new signature algorithms without redesigning tapscript.
Buchner's insight: use it RIGHT NOW as a forward-compatibility slot. Encode a real SLH-DSA or SHRINCS public key with a one-byte tag, drop it into a tapscript leaf next to your real Schnorr key, spend today with a dummy witness. You get an ordinary Schnorr-secured spend under current rules — AND an on-chain commitment to the exact PQC verification slots you'd want after activation.
When a future soft fork binds real semantics to those tags (with PQ signatures transported via the annex), the same UTXO becomes strictly PQ-verified with no migration spend. You don't have to pick BIP 360 vs SHRINCS vs STARK compression first. The slots just sit there. Whichever scheme eventually gets real verification rules is the one that wakes them up. If Q-day never comes, you lose nothing. If it does, your April 2026 UTXO becomes quantum-safe on its own.
IF I had not elder oracle, It's the first proposal in the entire writeup that treats "what should I do today" as a solvable one-line problem. Full analysis + jump link to the new section: bitcoinquantum.space/part3/#…

Boiler retweeted

Satoshi s'est trompé.
Il y a un bug dans le minage de Bitcoin depuis le tout premier jour. C'est une simple erreur de calcul de Satoshi qui pourrait être exploitée pour miner des blocs à une vitesse délirante. C'est un des bugs que le BIP-0054 (en discussion) résout. Je vous explique.
Pour comprendre, il faut d'abord rappeler le fonctionnement du mécanisme d'ajustement de la difficulté. Comme vous le savez, tous les 2016 blocs, soit environ toutes les 2 semaines, les noeuds recalculent la cible de difficulté. L'objectif est de maintenir un rythme stable d'un bloc toutes les 10 minutes, quelle que soit la puissance de calcul déployée par les mineurs. Pour faire cet ajustement, les noeuds mesurent combien de temps la dernière période a duré, la comparent au temps qu'elle aurait due durer (2016 x 600 = 1 209 600 secondes), puis corrigent la difficulté en conséquence.
C'est dans ce calcul qu'il y a le bug. Pour mesurer le temps de la dernière période qui vient de passer, le noeud compare l'horodatage du premier bloc de la période à celui du dernier. Instinctivement, ça parait logique de faire ça, mais en fait c'est une erreur, car il n'y a que 2015 intervalles entre le premier bloc et le dernier de la période, pas 2016.
Si on note t0 l'horodatage du premier bloc et t2015 celui du dernier, le noeud calcule le temps écoulé comme T = t2015 - t0. Les intervalles mesurés sont donc :
de t0 à t1 (1 intervalle) > de t1 à t2 (2 intervalles) > ... > de t2014 à t2015 (2015 intervalles)
On obtient bien 2015 intervalles et pas 2016. Pour en avoir 2016, il aurait fallu calculer T = t2015 - t-1, où t-1 est l'horodatage du dernier bloc de la période précédente. C'est ce qu'on appelle un bug "off-by-one" : une erreur de décalage d'une unité.
Concrètement, l'impact sur la PoW est négligeable. Ce décalage introduit un biais d'environ 0,05% vers une difficulté très légèrement surestimée. Mais le vrai problème est ailleurs. Ce bug fait que les périodes d'ajustement ne se chevauchent pas. L'horodatage du dernier bloc d'une période n'entre pas dans le calcul de la suivante :
- La première période : t0 à t2015
- La deuxième : t2016 à t4031
- etc.
Il n'y a jamais de chevauchement, et c'est précisément cette discontinuité qui rend possible une attaque que le l'on appelle "time warp".
Le principe est le suivant :
1 - un mineur qui controlerait une majorité de la puissance de calcul commence par fixer les horodatages de tous les blocs d'une période, sauf le dernier, au minimum autorisé par les règles du protocole (supérieur au MTP, la médiane des 11 derniers blocs), au lieu de mettre l'heure réelle comme horodatage.
2 - sur le dernier bloc de la période, il attribue un horodatage artificiellement avancé dans le futur. La limite maximum pour un horodatage d'un bloc Bitcoin, c'est NAT + 2 heures. Le NAT c'est la médiane des temps réels des nœuds, mais pour simplifier, on peut dire que c'est presque le temps réel. On prend donc ce temps réel et on ajoute 2 heures de largesse dans le futur. Ce temps NAT + 2h, c'est la limite maximum, et l'attaquant va placer cette limite max dans le futur sur le dernier bloc de la période.
3 - la période est terminée, tous les nœuds Bitcoin appliquent l'ajustement de la difficulté. À cause de la manipulation des horodatages de l'attaquant, la période mesurée a duré plus longtemps qu'en réalité. Les noeuds abaissent donc la difficulté de minage pour la période suivante.
4 - l'attaquant reproduit exactement la même manipulation sur la période suivante. Puisque les périodes ne se chevauchent pas, et puisque le MTP est une médiane et non une moyenne, le premier bloc de la deuxième période d'attaque peut avoir un horodatage loin dans le passé, alors que le précédent a un horodatage dans le futur. À la fin, l'écart entre le premier bloc de la période et le dernier sera encore plus grand que la période précédente, et cet écart augmente de période en période.
En répétant ce procédé sur plusieurs périodes, un attaquant pourrait théoriquement faire chuter la difficulté de minage au point de produire jusqu'à 6 blocs par seconde (au lieu de 1 toutes les 10 minutes). Les conséquences seraient terribles : les timelocks ne serviraient plus à rien, le réseau serait saturé, les réorganisations se multiplieraient, et les confirmations de transactions perdraient leur valeur. Le tout permet à l'attaquant de récupérer les récompenses de bloc à un rythme effrené.
Si Satoshi avait fait se chevaucher les périodes, comme nous l'avons vu en intro, cette attaque ne serait pas possible. Ce qui la rend réalisable, c'est que le calcul du temps de la période repose sur le premier bloc de la période, qui peut être placé loin dans le passé, plutôt que sur le dernier bloc de la période précédente, qui dans le cas de cette attaque se trouve placé dans le futur.
Comment résoudre ce bug ?
Et bien le plus simple serait de corriger l'erreur de Satoshi, et de se faire chevaucher les périodes. Mais c'est impossible sans faire un hard fork. Le BIP-0054 (consensus cleanup) propose donc une autre approche par soft fork : imposer que le premier bloc d'une nouvelle période de difficulté porte un horodatage qui ne précède pas de plus de 2 heures celui du dernier bloc de la période précédente. Cette contrainte rétablit une forme de continuité entre les périodes, empeche la manipulation des écarts temporels, et donc empeche l'attaque time warp.
Le BIP-0054 ne corrige pas que ça, il corrige également d'autres vulnérabilités historiques du protocole.
