

BlackArrow - offensive driven defense #redteam #threathunting by @Tarlogic
Joined June 2019
- Tweets74
- Following14
- Followers1.8K
- Likes5





Evading Gatekeeper in enterprise macOS environments 🍎
In this post, @0xCappuCHINO covers a Red Team case study on macOS initial access, quarantine propagation behavior, and adapting payload delivery against built-in controls and EDR.
➡️ Read more: tarlogic.com/blog/macos-gate…

All materials from BlackArrow’s talks are now available in our GitHub repository.
➡️ github.com/blackarrowsec/tal…

Microsoft has addressed a one-click NTLM leak vulnerability affecting Windows Snipping Tool (CVE-2026-33829), discovered by our researcher Marcos Díaz (@Calvaruga).
➡️ Read the write-up: github.com/blackarrowsec/red…
➡️ Microsoft bulletin: msrc.microsoft.com/update-gu…
On our way to Switzerland 🇨🇭, where tomorrow @ineesdv will present our research at @1ns0mn1h4ck on abusing calendar invite processing in modern email clients.
➡️ Read more: insomnihack.ch/talks/meeting…

BlackArrow retweeted

Phishing now happens in meetings as well? @ineesdv say yes! Understand how attackers exploit collaboration tools with this new #Insomnihack talk.
Buy your ticket now: ow.ly/yBis50Ya55M
#InsomniHack #Cybersecurity #INSO26

Just over 24 hours until @_kripteria takes the stage at @h_c0n to revisit the design and methodology of attack graphs in Active Directory, showcasing new approaches with Neo4LDAP.

Meetings You Didn’t Plan, But We Did
In this post, @ineesdv breaks down how calendar event processing in Outlook and Gmail can be abused to deliver spoofed meeting invites that are automatically added to a user's calendar without interaction
➡️Read more: tarlogic.com/blog/abusing-ca…

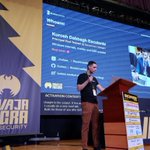
Kudos to our colleague @_Kudaes_ , who yesterday delighted us at @NavajaNegra_AB with his talk 'Activation Context Hijack,' which can be rewatched here: twitch.tv/videos/2581089790?…

This Thursday, our colleague @_Kudaes_ will be at @NavajaNegra_AB presenting Activation Context Hijack: a new code execution technique for Windows environments.
➡️ More info: navajanegra.com/2025/speaker…

Are you aware that even with App-Bound Encryption, attackers can still attempt to steal browser cookies?
Our #ThreatHunting team explains how the technique works and how to detect it.
➡️ github.com/blackarrowsec/tac…


AvePoint has fixed a vulnerability in DocAve, Perimeter and Compliance Guardian discovered by our researchers @m1ntko and @Calvaruga.
This vulnerability can be used to achieve Remote Code Execution (RCE) in affected systems.
➡️ Advisory: avepoint.com/company/docave-…

Are you aware that WebDAV and search-ms can trick users into executing remote files as if they were local?
Our #ThreatHunting team breaks down how the technique works and how to detect it.
➡️ github.com/blackarrowsec/tac…


BlackArrow retweeted

¡No parpadees si no te lo quieres perder! Kurosh Dabbagh nos habla de "Call Stack Spoofing para ocultar la ejecución de implantes desde memoria" #WindowsInternals #Malware #EDR @_Kudaes_

In a few hours, our colleague @_Kudaes_ will talk at @EuskalHack about call stack spoofing to hide the execution of implants from memory. #ESCVII
➡️ Read more: securitycongress.euskalhack.…

Are you aware of this technique for achieving fileless persistence?
Find out how it works and how to detect it.
➡️ github.com/blackarrowsec/tac…


BlackArrow retweeted

Although it's nothing new, @ineesdv and I are pleased to publish our own ROP-based implementation of the code fluctuation technique. We've tried to keep it simple and functional, avoiding to use common features like Timers, HWBP or APCs. github.com/Kudaes/Shelter

Our colleagues @_Kudaes_ & @ineesdv will be at #HackOn2024 presenting an alternative approach to ROP-based sleep obfuscation technique to evade memory scanners.
➡️ Read more: hackon.es/charlas/In%C3%A9s_…
