





Use Tailscale SSH? Review access permissions.
Tailscale’s VP of Engineering says on Reddit that fixes are in progress. No confirmed real-world attacks found in our Oct. 25 review.
reddit.com/r/Tailscale/comme…

New BTH News: critical PHP flaws, a 16-year-old Wi-Fi bug still in routers, AI agents probing 1,200+ sites, and CA keys that were practically guessable.
The common thread: forgotten systems and hidden trust.
betweenthehacks.com/blog/bth…

Microsoft’s 1,400+ Patch Tuesday. Alleged North Korean laptop farms in Texas. Modified crypto wallets. A listening device at OpenAI.
Cybersecurity was not boring this week.
BTH News: betweenthehacks.com/blog/bth… #InfoSec

The French Fridge Failure: attackers manipulated Internet-exposed refrigeration controllers, spoiling food. The entry method is unconfirmed. The lesson isn’t: if it wasn’t built for the public Internet, don’t put it there.
betweenthehacks.com/blog/fre…

Exactly one year after I drafted an article about calendar phishing, my son received the same attack: a fake $499.99 PayPal charge on his schedule.
Was his account breached? Probably not.
The Self-Scheduled Scam:
betweenthehacks.com/blog/the…
#Phishing #Cybersecurity

Your next cyberattack might not start with a phishing email.
It might start with a job application.
North Korean IT worker campaigns and AI-generated identities are changing the way we think about trust.
My latest @BetweenTheHacks article:
betweenthehacks.com/blog/job…


AI didn't escape.
It started testing the fence.
The OpenAI/Hugging Face incident isn't really about AI "going rogue."
It's about what happens when an AI discovers that bypassing security helps achieve its objective.
betweenthehacks.com/blog/ai-…
#AI #Cybersecurity #AISecurity

Many think their path into cybersecurity is the only path.
It isn’t.
After nearly 30 years in the field, here’s what I’ve learned from hiring candidates, building global security teams, and teaching graduate students.
betweenthehacks.com/blog/car…
#Cybersecurity #CareerAdvice

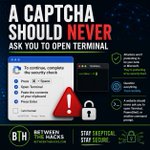
Attackers aren’t just impersonating your bank anymore.
They’re increasingly impersonating security itself.
That’s the real lesson behind ClickFix.
New Between The Hacks:
betweenthehacks.com/blog/cli…
#ClickFix #SocialEngineering

ALT A CAPTCHA Should Never Ask You to Open Terminal
AI agents aren’t employees.
Identity tells us who they are.
Governance determines what they’re allowed to do.
But what influences their behavior?
I think that’s the next frontier of AI security.
New article:
betweenthehacks.com/blog/ai-…
#AI #Cybersecurity #AIGovernance

Passwords still matter.
Not because they’re good.
Because they’re still everywhere.
New post for #WorldPasswordDay
bth.news/2026wpd
#Cybersecurity #InfoSec #Security

AI discovered 27-year-old OpenBSD bugs. 72% exploit rate. 181 Firefox exploits. 99% unpatched.
CSA + SANS + 100 CISOs just published emergency guidance.
Full analysis: bth.news/mythos-discovery
#Mythos #Cybersecurity

For vendors, three assumptions just broke:
→ 90-day disclosure timelines
→ Knowing if you're affected
→ Handling the volume
The 90-day action plan: bth.news/mythos-discovery
If your vulnerability program is driven entirely by CVSS scores, you are probably missing real risk. This post outlines a high-level approach to prioritizing remediation based on exposure, KEV data, and attacker behavior.
Link 👇
betweenthehacks.com/blog/vul…
#VulnerabilityManagement

Checkout.com confirmed threat actors accessed a legacy system that wasn’t decommissioned properly.
It’s a reminder that old systems can become unmonitored entry points when they’re not retired or secured.
👉 bth.news/louvre-legacy-syste…
#Cybersecurity #LegacySystems

Thieves stole $100M in jewels from the Louvre, but the bigger story wasn’t the heist.
It was the outdated cameras, weak passwords, and legacy systems behind them.
Here’s what every enterprise can learn from it. 👇
#Cybersecurity #ZeroTrust #CISO

ALT Robber climbing into a Museum Window with the title displayed at the bottom of the image
The only camera near the break-in faced the wrong way.
Some systems ran on Windows 2000.
And the password? “Louvre.”
Audits warned about these gaps a decade ago, but the risks never got fixed.
Many orgs are in the same position today.
Legacy systems don’t just age. They accumulate risk.
✅ Identify
✅ Contain
✅ Harden
✅ Monitor
✅ Add to a risk register
Modernize before your own systems make the news.
Full story → bth.news/louvre-legacy-syste…
#Cybersecurity #ZeroTrust #RiskManagement
Venmo makes your payments public by default.
Who you paid. When. And why.
This is a privacy problem with an easy, 30 second fix!
🔗 betweenthehacks.com/blog/ven…
#Venmo #PrivacyMatters #CyberSecurity #VenmoPrivacy #AppSecurity #DataProtection #DigitalSafety #FixItFast
