

👰🏻+🤱🏻+☁️👩🏻💻. Vice President, Head of Global Communications @Cloudflare. The higher the hair, the closer to the clouds!⛅️
San Francisco
Joined November 2009
- Tweets4K
- Following1.3K
- Followers2K
- Likes3.9K




Daniella V. retweeted
This is going to be a very important resource for everyone managing any technology infrastructure to bookmark.

Introducing Zero Wire: a public vulnerability intelligence feed on @CloudflareRadar, bringing the clarity of a news wire service to critical security developments. cfl.re/4iCvSbj

Welcome to the team, Alex! 🚀

I'm Incredibly excited to be joining @Cloudflare today as SVP of Emerging Technology.
I’ll be leading ETI, Cloudflare’s skunkworks, working with the ridiculously talented and ambitious team there to build Cloudflare’s next generation of products and businesses. The mandate for ETI is to look beyond the core business today, make ambitious bets on what will matter tomorrow, and turn those bets into businesses that shape the company’s future.
I’ve long believed that open and free access is one of the most powerful forces we have for creativity, competition, connection, and opportunity. Open source software, open models, and access to knowledge give more people the ability to build—and an open Internet lets them reach the world. But keeping the web open means constantly pushing back against walled gardens and gatekeepers. As AI changes how people find information, use software, and interact with each other, preserving that access becomes even more consequential.
Cloudflare is uniquely positioned to protect the open web and has a long history of doing so. We saw it again two weeks ago: when the php2shell vulnerabilities hit PHP, which runs almost 70% of the web, Cloudflare had protections live before the flaws were even public, automatically, for every site behind it, including the ones on the free plan.
That independent global network puts powerful capabilities in the hands of builders everywhere. On Cloudflare’s developer platform, you don’t pick a region: every service runs in every data center, in nearly 350 cities around the world. And it’s backed by a culture of experimentation and shipping that I’ve admired for years. The team consistently turns ambitious technical ideas into things people can actually use.
I’ve been a Cloudflare user for over a decade, and today it’s where I build and run my own projects, from a website for a friend’s barbecue restaurant to the infrastructure behind my home network. I’ve experienced firsthand how much it makes possible.
From Stack Overflow to Stacks to investing in and advising founders, I’ve always loved building things that help people build things. The common thread is giving more people access to the tools, knowledge, and infrastructure to build on their own terms. I love working with people who see what’s possible, giving them the room to pursue it, and building the teams and businesses that make it real.
At Cloudflare, I get to bring those things together at an extraordinary scale, in service of a mission I deeply believe in: helping build a better Internet.
There’s a lot to build. I’d love to hear what you think we should take on. And if you want to come work on it, DMs are open.

1
2
235
My new lava lamp is bringing Cloudflare energy and a little zen to my desk. ☁️🌋
High velocity, but calming the stress. The blobs understand the assignment.
1
14
597
Daniella V. retweeted

PREDICTION: Cloudflare CEO Matthew Prince (@eastdakota) says AI agents will change the business model of the Internet over the next decade:
"In five years, agent traffic is going to be 1000x human traffic."
"The Internet almost collapsed during COVID when traffic doubled."
"There's a lot more servers, routers, and bandwidth that has to get provisioned in order for that to work. The question is, who will pay for it?"
"My hunch is that something's got to change in terms of how the Internet works. Like some version of micropayments that every time you access a resource, your agent pays a ten-thousandth of a penny to be able to see the menu."
"Then there's probably some sort of trade where if you are willing to tell the restaurant what you're looking for, that price goes down, maybe it's free. In some cases, the site might actually pay you to come visit it."
"This will lead to the next version of advertising, which is how do you advertise to agents?"
No better way to inspire what’s next than to have @AdamMGrant and @zatlyn close out #CloudflareConnect. Bringing together everything we’ve learned this week, they’re exploring what it means to embrace change, and continue evolving.

11
344
Daniella V. retweeted
Two classes extremely bad cyber vulnerabilities disclosed in the last 24 hours. The first potentially impacts everyone online. The second impacts nearly everyone running a server.
tl;dr: Everyone should upgrade their OS and Browser as soon as possible. If you run a server you should upgrade PHP (or ensure it’s removed if you’re not using it) as soon as possible.
The first class of vulnerabilities is a set of root TLS certificates that were discovered to have a trivial private key. Literally the number 4. These roots were controlled by #eMudhra. The problem is that with that an attacker could create a certificate and, if they could get in the traffic flow, intercept traffic to any site or service. The solution is to stop trusting certificates issued by these vulnerable roots. Upgrading your browser and OS is the fastest way for most Internet users to do this.
The second class of vulnerabilities doesn’t apply to most consumers directly, but does apply to most anyone running a server. These vulnerabilities have been dubbed #php2shell. PHP is one of the most widely used web programming languages. It’s estimated 70% of websites run on PHP. These vulnerabilities allow an attacker to send a crafted set of queries to a server running PHP and potentially take over the server. From there they could potentially read, modify, delete, or repurpose anything on the server. The solution is to upgrade PHP to the latest version ASAP. Even if you’re not using PHP for your web development, it’s often included by default. So make sure it is either upgraded or fully removed.
@Cloudflare received advanced warning of both of these classes of vulnerabilities. We’ve ensured that where we act as a proxy we are no longer trusting the vulnerable roots. We are also reviewing certificate transparency (CT) logs for any sign the vulnerability was exploited before its disclosure. We have not found any evidence but CT logs are not perfect and a sophisticated attacker who knew about the weakness could have exploited it without a new certificate being logged.
For the PHP vulnerabilities, we have deployed mitigations available for all customers for free. Because of the complexity of the vulnerabilities and number of ways it can be exploited, we also released new WAF capabilities that are unique in the industry to catch the exploit based on the response. These too are available for every Cloudflare customer for free.
Even if you are taking advantage of Cloudflare’s protection, it is important to upgrade your OS, browsers, and PHP installations as soon as possible. We can provide a strong bandaid, but the best protection is to fix the underlying problem.
If you’re interested in learning more, you can read our blogs:
Vulnerable roots: blog.cloudflare.com/emudhra-…
PHP vulnerabilities: blog.cloudflare.com/php-vuln…

He was so inspirational and his energy was electric. What a way to scale innovation!? 🚀🚀🚀

Inspired hearing about the new company @Bill_Gross has launched called IdeaLab AI. There are 1.2 million ideas on there for anyone that wants to build something. And @Cloudflare is giving $100,000 in credits to help build any of the ideas. Let’s go!


2
234
Daniella V. retweeted

Day 2, general session. Here’s how the morning started at #CloudflareConnect SF.


And great shoes to boot! 🤠👢
Powerful hearing @tecovas share how @Shopify and @Cloudflare working together makes the shopping experience more efficient and more seamless. Excited for this new era of online commerce 🎉


121
Daniella V. retweeted

You should see the other guy. @eastdakota doesn’t play around in enterprise negotiations.

Daniella V. retweeted
You all loved having @common at #CloudflareConnect last year, so we brought the legend back, performing live to kick off @eastdakota’s keynote. The energy in this room is unreal—if you aren’t here, you’re missing out. 🎤✨

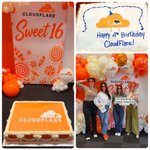
My first @Cloudflare cake was for our 4th birthday. This week, we celebrated our 16th!🎂
The cake, company, & celebration have gotten a whole lot bigger… but it’s always been just as sweet to build, ship, and share innovations with the world. 🧡 Happy #BirthdayWeek!

Nothing says “DO NOT DISTURB” quite like @kkblinder in this chair, designing her heart out during #BirthdayWeek 🎨🎂✨

Marketers everywhere right now: “Quick, replace every ‘AI’ keyword with ‘super intelligence.’” 🤓
3
187
Super proud @Cloudflare is helping to power America.gov. An extra special moment during #BirthdayWeek. 🇺🇸🚀 What a time to help build a better Internet!

Daniella V. retweeted
Just insane velocity at @Cloudflare. It’s giving AWS a decade ago.

there are so many exciting launches going on for birthday week that we put together a site so you (or your agent) can keep track of them all...
also added a fun little easter egg if you can find it 🧞♂️
cloudflare.com/birthday-week
Daniella V. retweeted
Welcome to @Cloudflare's #BirthdayWeek. As is our tradition, @zatlyn and I penned our annual Founders' Letter to kick the week off: blog.cloudflare.com/cloudfla…
