
The security partner that companies turn to for end-to-end solutions that attack the chaos of the cybersecurity landscape with context. Show No Weakness®
Phoenix, AZ
Joined June 2009
- Tweets5.2K
- Following606
- Followers1.4K
- Likes28K



💥 #FLASHNOTICE 💥
CVE-2026-0257 is being actively exploited to bypass #GlobalProtect authentication and gain unauthorized VPN access.
Organizations using vulnerable PAN-OS or Prisma Access deployments should patch immediately. More here: avertium.com/flash-notices/p…

Passing an audit doesn’t mean you’re secure. Learn how Avertium’s Assess, Design, Protect approach helps turn #Microsoft investments into stronger security, streamlined compliance, and an audit-ready program.
Get the guide 🖱️ avertium.com/resources/guide…

#BEC has traditionally targeted people. The next wave may target AI agents.
As #AIagents gain access to systems, attackers can use #promptinjection and malicious inputs to influence authorized actions, expose data, or manipulate financial workflows. 🔗 darkreading.com/cybersecurit…

When a healthcare nonprofit needed to build independent security capabilities from the ground up, Avertium helped create a cloud-first #Microsoftsecurity program with 24x7x365 protection through #MicrosoftSentinel + #DefenderforEndpoint.
Read the story: avertium.com/case-study/heal…

💥 FLASH NOTICE 💥
China-linked #ransomwaregroup #Warlock is actively targeting critical infrastructure organizations across Spanish and Portuguese-speaking countries.
On-prem and hybrid #SharePoint environments remain vulnerable and at risk. 🔗 avertium.com/flash-notices/w…

AI readiness starts with data security.
A #healthcaretechnology company partnered with Avertium to leverage #MicrosoftPurview, identify security gaps, strengthen data governance, and create a roadmap for secure #AIadoption.
Read the story: avertium.com/case-study/cust…

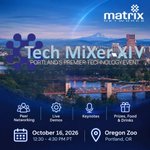
We’re excited to be sponsoring this year’s Tech Mixer XIV!
Join @Matrixnetworks on October 16 at the Oregon Zoo for an afternoon of live demos, insightful keynotes, and great conversations with the local tech community.
See you there! 🐯 mtrx.com/tm14/ #TM14

Server security is often overlooked as organizations focus on cloud, #AI, and identity. Yet servers remain a critical attack surface.
Learn how Defender for Servers and #DefenderforCloud fit together: avertium.com/blog/demystifyi… #cloudsecurity

💥 FLASH NOTICE 💥
#Apple released emergency updates for iOS & iPadOS addressing an actively exploited, critical #zeroday vulnerability in CoreGraphics.
Users of affected iPhone & iPad devices should update to #iOS 26.7.1 / iPadOS 26.7.1 immediately. 🔗 avertium.com/flash-notices/a…

Getting the most from #MicrosoftSecurity requires more than tools alone.
#FusionMXDR for Microsoft combines Microsoft Sentinel, #DefenderXDR, AI-powered investigation, and 24x7 expert monitoring to accelerate threat detection, response, & resilience.
➡️ avertium.com/fusion-mxdr-for…

Bush Brothers & Company partnered with Avertium to modernize security with #MicrosoftDefender XDR, #MicrosoftSentinel, and Fusion MXDR.
The result: greater visibility, streamlined operations, and stronger #threatdetection. Download the case study 👇
avertium.com/case-study/how-…

#Microsoft has disrupted #EvilTokens, an AI-powered phishing-as-a-service platform that helped attackers compromise 12,000+ inboxes across 10,000+ organizations using device code phishing.
The takeaway: #identitysecurity is the new frontline. Details: darkreading.com/identity-acc…

🚨 :
A Windows Defender #zeroday exploit has been released that can prevent #MicrosoftDefender Antivirus from receiving updates.
Unlike an attack that disables antivirus software entirely, the tool interferes with Defender’s update process. Details: avertium.com/flash-notices/w…

Great discussion at the Annual #PCIConference last week! Sarah Minday-Clarke joined PayPal's Nicole King to explore how #AI is streamlining #PCI assessment management, from control mapping to audit-ready documentation.
Thanks to everyone who joined the session 👏 👏

Avertium helps organizations assess maturity, prioritize risk reduction, strengthen governance, and operationalize #NISTCSF outcomes with expert consulting, #securityoperations, and #compliance support.
Learn more about our NIST CSF services here: avertium.com/nist-csf-consul…

A #SOC2audit shouldn't be a one-time event.
As threats, technologies, and business requirements evolve, annual #SOC2 audits help orgs validate security controls, maintain stakeholder trust, and stay ready for customer requirements.
Read the blog: avertium.com/blog/soc2-audit…

Being #SOC2 ready requires continuous monitoring, #riskmanagement, evidence collection, and security controls that stand up over time.
Avertium helps organizations achieve and maintain #SOC2readiness while reducing risk and strengthening trust. Explore: avertium.com/soc-2-complianc…

The FBI warns #AI is helping attackers find and exploit vulnerabilities faster, making traditional quarterly patching cycles riskier.
But the fundamentals still matter: #MFA, timely patching, and strong #cyberhygiene remain critical defenses. 🔗 cyberscoop.com/fbi-cyber-str…
As #AIadoption grows, so do risks like sensitive data exposure, compliance gaps, and #shadowAI.
Our new checklist outlines practical steps to manage AI risk with #MicrosoftPurview DSPM and build a stronger governance framework.
Download it for free ⤵️
avertium.com/resources/check…

💥 FLASH NOTICE 💥
An investigation has documented covert #datacollection and network surveillance activities in #LGOLED televisions.
This contradicts LG's public statement that TVs "do not collect, record, or store ambient conversations."
Details ➡️ avertium.com/flash-notices/l…
