Andrea R retweeted
Unencrypted password and user related to ssh in a Go Loader, interesting 🤔
0caa772186814dbf84856293f102c7538980bcd31b70c1836be236e9fa05c48d
"CelestialCodes.exe" is Rhadamanthys
cc: malwarebytes.com/blog/threat…
@RussianPanda9xx @suyog41 @crep1x @1ZRR4H
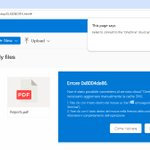
#Malspam spotted in Italy 🇮🇹
Fake OneDrive DNS Error
EML>.zip>.html>powershell(clipboard)>.exe
hxxps://pixeltechnical[.]com/V1x/172988
hxxps://trendistech[.]com/mPy8/507641
hxxps://pixelprofiti[.]com/cpxMn7/535927
virustotal.com/gui/collectio…
csirt.gov.it/contenuti/rilev…
Andrea R retweeted
Seems that someone compromise legitimate Wordpress sites to install malicious JS,that,on the client side, retrieve other JS from a smarcontract on the BSC blockchain and show to the user a fake browser update page to lure users to installmalware #clearfake #malicioussmartcontract
#Pikabot - BB28 @Cryptolaemus1
When the #TA577 splits the base64 string, using characters from one to four, a single-character split has a high chance of being repeated as a splitter point, leading to incorrect parsing.
cyberchef.org/#recipe=Split(…
Andrea R retweeted
2023-05-17 (Wednesday): Today, this week's BB28 #Qakbot-style distribution chain pushed #Pikabot instead of Qakbot. Followed up with #CobaltStrike using #DNSTunneling. We later saw additional Cobalt Strike traffic over HTTPS. List of IOCs available at https://xitter.cf/t.co/grUnRUq13b
Andrea R retweeted
#CVE-2023-23397 + #hashrelay + RCE + #empire 😈 Complete compromise of a machine by exploiting the Outlook CVE on patched Win11!
Andrea R retweeted
Threat Actors Spreading malware via legitimate websites.
.lnk > powershell > curl > .bat > powershell (renamed) > decrypt embedded payloads > reflective code loading
patrizioperna.wordpress.com/…
The IOC shared by @pr0xylife in its github related to the DLL contained in the #QakBot 1677576236 campaign may be inaccurate cause the overlay of different sizes is added to the original DLL with each Invoke-WebRequest. Further analysis will continue
Andrea R retweeted
1/ #TA505 has joined the @GoogleAds party! 🎉🎉
They distribute malware via download-cdn[.]com, previously used to push #Get2.
MSI (VT: 0/60) installs Ldrp.dll and then HVNC.dll, this last one connects to 64.190.113.123:443
[+] 328 related domains: github.com/CronUp/Malware-IO…
[Malvertising]
#Vidar Stealer
Source: hxxps://notepadsplu-plusinstall.com (77.73.131.130)
C2 Server: 77.73.133.32
Related IOCs:
505255cfa537772c206c5a35c6cfd08b
ed9e29f6e6442e6990a968ba4f8d2328
b748f697bcd3896153b1762f0376db8a772bf024
c5eb0bffdbb3db3d4751375f049af94e5e6c23c0