

@AMLBotHQ
Account based inSoutheast Asia!
About this account
- Account based in
- Southeast Asia
- Connected via
- Eastern Europe (Non-EU) App Store
X says this location may be affected by a proxy or VPN.
Account-level information from X, not a live location or the device used for a specific post.
Blockchain Intelligence at your fingertips. Crypto Tracing / AML Screening / Incident Response
Joined October 2020
- Tweets2.2K
- Following623
- Followers8.2K
- Likes4K




Pinned Tweet
New Product: AI Tracer is Live 🔍
A self-serve crypto investigation tool, built for everyone. Paste a TxID and AI traces where the funds went — every wallet, bridge, and exchange along the path, across 14 chains. A visual map in minutes. No analyst skills needed.
First Trace FREE → amlbot.com/ai-tracer
At least $755K taken from @rrealist in a UK wrench attack
Tracing shows ~719K USDC was deposited to @hitbtc within hours. The SOL was swapped to ~14.7 ETH via @near_intents and is now sitting untouched at 0xeec36e6b1dad28331e457d1abf532265d6ee700f
We are actively monitoring this case


if you live in the uk and do crypto get the fuck out
just got my house invaded, taped up held at knife point & robbed for $800k
in so much shock i dont know what the fuck to do, fuck this country. No this is not satire, i fucking wish it was.
wallet with stolen funds
solscan.io/account/B3pMs331k…

AMLBot retweeted
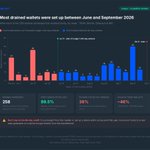
Onchain data from the recent incident involving @Ledger devices sold through reseller @cryptobilis shows most drained wallets were first funded between June and September 2026
We checked when each of the 258 drained addresses first received funds. ~90% were first funded after June 1. The median date is Aug 6, and none was funded after Oct 4
But 98 of them (38%), holding ~46% of the value drained from these addresses, were already in use before July 11. That is outside the 90-day window in Ledger’s advisory. This points to devices bought earlier, or existing seeds restored onto newer devices
If you bought from this reseller this year, or entered an existing seed into one of its devices, don’t rely on the 90-day cutoff. Move your funds to a new seed generated on a device bought directly from the manufacturer

Update on the @Ledger drained devices incident, linked to devices reportedly sold through reseller @cryptobilis. Our tracing puts total losses at over $80M
Roughly two-thirds of the stolen value is still on-chain: ~20.2K ETH is lying dormant across 14 ETH addresses and 92.5 BTC has not moved. @Tether has since frozen ~11% of the total in USDT on TRON
Most of the remaining TRON USDT was bridged and swapped into ETH via @USDT0_to, @THORChain, @RelayProtocol, @Chainflip, @BitgetWallet, HiFiSwap and @near_intents. Around one fifth of the stolen funds has since been deposited into Tornado Cash and laundering is ongoing
We are actively monitoring this case


Onchain data from the recent incident involving @Ledger devices sold through reseller @cryptobilis shows most drained wallets were first funded between June and September 2026
We checked when each of the 258 drained addresses first received funds. ~90% were first funded after June 1. The median date is Aug 6, and none was funded after Oct 4
But 98 of them (38%), holding ~46% of the value drained from these addresses, were already in use before July 11. That is outside the 90-day window in Ledger’s advisory. This points to devices bought earlier, or existing seeds restored onto newer devices
If you bought from this reseller this year, or entered an existing seed into one of its devices, don’t rely on the 90-day cutoff. Move your funds to a new seed generated on a device bought directly from the manufacturer
Glad to see this one end with the funds back where they belong. Credit to the @79thVault team for acting fast — speed is what makes recovery possible. We’ll keep tracing and reporting illicit flows on-chain so more incidents end this way.

🤝 Thank you @AMLBotHQ for supporting 79VAULT with on-chain monitoring and transaction tracing following the recent security incident involving 16,249 BNB.
🔐We’re grateful the funds have been returned safely. Strong collaboration and blockchain intelligence made a real difference.
#79AU #79VAULT #AMLBot

AMLBot retweeted

🤝 Thank you @AMLBotHQ for supporting 79VAULT with on-chain monitoring and transaction tracing following the recent security incident involving 16,249 BNB.
🔐We’re grateful the funds have been returned safely. Strong collaboration and blockchain intelligence made a real difference.
#79AU #79VAULT #AMLBot
The reported @frogmanhaha drain netted the attacker roughly $2.4M after the stolen assets were sold
Tracing shows ~13,241 SOL, currently worth ~$1.54M, entered @theprivacycash. Another ~$815K deposited to Hyperliquid and was converted into XMR through @PerpetualCow XMR1
A smaller portion of 160 SOL (~$18.6K) reached a @kucoincom deposit address, while ~80 SOL (~$9.3K) was commingled by an unidentified service.
We are actively monitoring this case


Was drained for $4m+ USD this morning at 4:30am while I was asleep
Not sure how it happened yet, but I'm in Singapore and met a lot of new people
Thank you to the teams and individuals who are helping with the investigation. Will share more when I can
Impressive work by @zachxbt ! Interestingly enough, it looks like Chinese launderers couldn't care less where the funds are coming from... 349.7K USDC came straight from zachxbt.eth on Base via @debridge


The @bitget hacker seems to have fumbled ~$700K while laundering the stolen funds😂
Our tracing shows the attacker sent funds to @Chainflip deposit channels on the wrong chains:
~267K USDC was swapped via CoW Swap and paid on Ethereum to a channel that only exists on Arbitrum. That address has now been blacklisted by @circle
~160 ETH (~$430K) was bridged to Arbitrum and sent to a channel that only exists on Ethereum. No contract on Arbitrum can sweep it, so the funds are stuck
Both deposits were likely automated, with only seconds between hops. It appears their laundering script mixed up Ethereum and Arbitrum, twice

Bitget exploiters are laundering through @THORChain affiliates they appear to control themselves
Our tracing shows 3 affiliates were used only by @bitget attacker wallets: ~3.7K swaps worth ~$58.7M, mostly XRP/ETH to BTC. No swaps from any other users at all
The affiliates collected ~330K RUNE (~$245K) in fees. One cashed out ~132K USDT and ~0.56 BTC, all of which ended up at @okx. Another swapped its fees straight back into an attacker wallet
One affiliate is still holding ~72K RUNE (~$54K), unmoved
thor18dvgrgpvxlh7rhhld4qjyrxs9c7tvwdakrkjm4
thor1rj9f7m7n72nwslau7jzla09u0l4zr4ru8277d2
thor199tl2t4fkxqn7pawk8dgera79dl70rnczu6jsl

AMLBot retweeted
Update: @near_intents has confirmed the security incident
nitter.cf/near_intents/status/21…

Earlier today NEAR Intents services were stopped after a security incident was detected. The incident was caused by a bug in the Omni deposit and withdrawal infrastructure interaction with NEAR Intents smart contract.
The preliminary report indicates the total loss of approximately $3.8M. These funds will be compensated in full.
The contract-side vulnerability has been patched. The operations of the NEAR Intents and near(.)com are expected to resume within 1h.
Deposits and withdrawals on the following networks will remain unavailable for an additional ~12 hours while fixes to the Omni infrastructure are completed: BSC, Polygon, TON, Optimism, Avalanche, Stellar, Monad, LayerX, Adi, Scroll and Plasma.
In case users hold any assets from these chains inside NEAR Intents (for example, in HOT wallet or on near(.)com), they will be able to swap them into other assets once NEAR Intents is back up (in ~1h).
The incident has been reported to law enforcement, and we are working with security and blockchain analytics partners to trace the funds and pursue recovery. A detailed report will be shared publicly in the following days.
🚨 Suspicious activity involving @near_intents: ~$4M in withdrawals
Our monitoring has flagged a series of suspicious withdrawals totaling approximately $4M
At this stage, it is not clear whether this is an exploit of the protocol or whether the funds may be connected to another incident
Suspicious txs:
0x9fe58e031f73bbd880c782bc9e7446bcda32cadb304a729209871a4a81856c4c
0x0381265d6a1bb09de899f49f410a8b907cd548358a7e3c91076c3a52656b8220
0x69d1c68c7e961a0199d3c9f3b6a31cb168ed775ef34b51a42762253ac1efcceb
0x9c10b967da0c85631ec105e3b322c0a851fcd01b69ff390ff58f860e5cce003a
Our tracing indicates that funds are currently moving toward @kucoincom, with some funds bridged to BTC
We are actively monitoring the situation and will share updates as they become available, pending official confirmation of security incident from NEAR Intents

Update: @near_intents has confirmed the security incident
nitter.cf/near_intents/status/21…
Earlier today NEAR Intents services were stopped after a security incident was detected. The incident was caused by a bug in the Omni deposit and withdrawal infrastructure interaction with NEAR Intents smart contract.
The preliminary report indicates the total loss of approximately $3.8M. These funds will be compensated in full.
The contract-side vulnerability has been patched. The operations of the NEAR Intents and near(.)com are expected to resume within 1h.
Deposits and withdrawals on the following networks will remain unavailable for an additional ~12 hours while fixes to the Omni infrastructure are completed: BSC, Polygon, TON, Optimism, Avalanche, Stellar, Monad, LayerX, Adi, Scroll and Plasma.
In case users hold any assets from these chains inside NEAR Intents (for example, in HOT wallet or on near(.)com), they will be able to swap them into other assets once NEAR Intents is back up (in ~1h).
The incident has been reported to law enforcement, and we are working with security and blockchain analytics partners to trace the funds and pursue recovery. A detailed report will be shared publicly in the following days.
Join our giveaway with @SimpleSwap_io
Share a moment when checking an address before sending made a difference, or when skipping the check cost you.
How to enter:
Follow @SimpleSwap_io and @AMLBotHQ
Quote the original post with your story and #SimpleSwapxAMLBot
Prizes:
5 winners get $50 in USDT + 50 AMLBot checks each
Ends October 5 👇

The Check Before You Send – $250 Giveaway + 250 AMLBot checks
Before crypto leaves your wallet, there are two different things worth checking.
Is this actually the address you meant to send to?
And does its on-chain history give you any reason to pause?
Tell us about a specific moment when checking before a transfer made a difference, or when skipping that check taught you a lesson.
Maybe you spotted a lookalike address copied from your transaction history. Maybe an address check showed risk you weren't expecting. Maybe one last review made you stop before sending funds somewhere you shouldn't.
How to enter:
1️⃣ Follow @SimpleSwap_io and @AMLBotHQ
2️⃣ Quote-repost this post with your story and #SimpleSwapxAMLBot
🏆 5 winners, chosen at random from valid entries: $50 in USDT + 50 AMLBot checks each
🗓 Campaign ends October 5. Winners announced October 6.

AMLBot retweeted
Bitget exploiters are laundering through @THORChain affiliates they appear to control themselves
Our tracing shows 3 affiliates were used only by @bitget attacker wallets: ~3.7K swaps worth ~$58.7M, mostly XRP/ETH to BTC. No swaps from any other users at all
The affiliates collected ~330K RUNE (~$245K) in fees. One cashed out ~132K USDT and ~0.56 BTC, all of which ended up at @okx. Another swapped its fees straight back into an attacker wallet
One affiliate is still holding ~72K RUNE (~$54K), unmoved
thor18dvgrgpvxlh7rhhld4qjyrxs9c7tvwdakrkjm4
thor1rj9f7m7n72nwslau7jzla09u0l4zr4ru8277d2
thor199tl2t4fkxqn7pawk8dgera79dl70rnczu6jsl
Update: It seems stolen funds from the @bitget hack have started to be laundered through Wasabi CoinJoin (mixer)
Our tracing links ~4 BTC in a CoinJoin round back to a Bitget TRON wallet. The funds were swapped from TRX to USDT, bridged to Ethereum via @USDT0_to, swapped to ~145 ETH, then sent through @THORChain to ~4.59 BTC. The BTC was then split and prepared before entering the CoinJoin
We have blacklisted the related addresses and are monitoring the attacker's BTC for further CoinJoin activity
A fake chain impersonating @GIWA_by_Upbit was listed with a bridge/RPC and drained ~768 ETH ($2.07M) in ~13 hours
Our analysis shows around 1,350 unique wallets were affected. The operator deployed a real-looking bridge using the OP Stack, but kept admin control of it. Once deposits piled up, they swapped the bridge code, took all ETH, then switched it back, all in a single transaction
~407 ETH has since been deposited to Tornado Cash. ~358 ETH is lying dormant across three addresses holding 221, 107 and 30 ETH. We are monitoring the related wallets
Interestingly the contract deployer has gas funding from @Changehero_io
Only bridge via official links. Stay vigilant!

Update: It seems stolen funds from the @bitget hack have started to be laundered through Wasabi CoinJoin (mixer)
Our tracing links ~4 BTC in a CoinJoin round back to a Bitget TRON wallet. The funds were swapped from TRX to USDT, bridged to Ethereum via @USDT0_to, swapped to ~145 ETH, then sent through @THORChain to ~4.59 BTC. The BTC was then split and prepared before entering the CoinJoin
We have blacklisted the related addresses and are monitoring the attacker's BTC for further CoinJoin activity
~$343M (~88%) of the ~$389M stolen from @bitget has not moved
Our tracing shows 13 attacker wallets are lying dormant: ~68.3K ETH across 8 wallets on ETH Mainnet, ~83M XRP across 4 wallets and ~18.9K ZEC in 1. None of them has sent a single transaction since being funded
The laundering is running through one active XRP wallet and the smaller branches. ~5.2M XRP has been peeled off so far, and the TRON, BNB and stablecoin proceeds are being swapped into BTC via @THORChain, @Bridgersxyz and @near_intents
Our team have blacklisted the related addresses and are actively monitoring them

Update: Tracing shows the exploiter behind @payy_link has moved almost all the funds to Tornado Cash
The second batch of ~$90.2K in USDC remains parked in the attacker’s wallet, with no action from @circle in the past two days

It seems like @payy_link was exploited for ~$1.9M in USDC
Our tracing shows the proceeds were swapped into ~683 ETH and split across four fresh wallets (~200 / ~280 / ~200 / 1 ETH). Those wallets have not moved since
A second batch of ~90.2k USDC is still parked in the attacker's entry wallet. It remains there and was not blacklisted by @circle at our last check
Worth noting: the attack wallet's gas was seeded through Railgun two days before the drain
We are actively monitoring this case and will post updates if funds move

~$343M (~88%) of the ~$389M stolen from @bitget has not moved
Our tracing shows 13 attacker wallets are lying dormant: ~68.3K ETH across 8 wallets on ETH Mainnet, ~83M XRP across 4 wallets and ~18.9K ZEC in 1. None of them has sent a single transaction since being funded
The laundering is running through one active XRP wallet and the smaller branches. ~5.2M XRP has been peeled off so far, and the TRON, BNB and stablecoin proceeds are being swapped into BTC via @THORChain, @Bridgersxyz and @near_intents
Our team have blacklisted the related addresses and are actively monitoring them