


AlejoGP retweeted

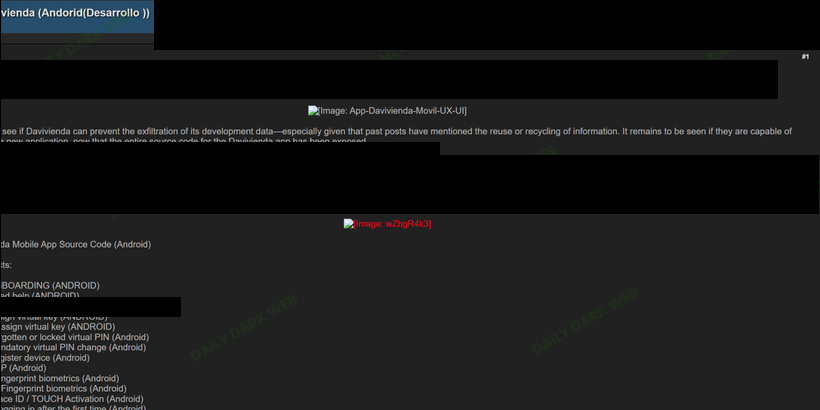
🇨🇴 BANCO DAVIVIENDA ANDROID APP SOURCE CODE SALE CLAIM
A threat actor claims to be selling complete Android mobile-app development material for Banco Davivienda, a major Colombian bank, describing full source/projects covering onboarding, login, biometrics, loans, payments, and related banking modules.
The underground listing alleges material covering dozens of Android projects/modules, including areas such as:
* Onboarding and login / virtual PIN / OTP
* Device registration and biometric login (fingerprint / Face ID-style flows)
* Profile and data-update features
* Consumer loan and mortgage-related modules
* Payments, top-ups, QR, and cardless withdrawal features
⚠️ Analyst Note:
Source-code sale posts for banking apps are often incomplete repos, old builds, partner/contractor leftovers, or recycled screenshots. Whether production Davivienda mobile development systems were actually breached, whether the claimed module list is complete/current, and whether any credentials or signing material are included remain unverified from the listing alone.
We assess this as an unverified threat-actor claim involving alleged Banco Davivienda Android development/source material, NOT confirmation of a live compromise of Davivienda production banking systems.
If authentic, banking-app source and development artifacts could aid reverse-engineering, phishing UX cloning, and discovery of further application weaknesses.
#DDW #DarkWeb #Colombia #Davivienda #Banking #MobileSecurity #SourceCode #ThreatIntelligence #CyberSecurity
AlejoGP retweeted

A todas las personas que contribuyeron a que DragonJARCON fuera posible, a los speakers, sponsors, asistentes, mil gracias, por hacer de esta versión algo inolvidable ❤️🐉
@DragonJARCon
Igualito pero entrando en un shadow it de multinacional.

Así es entrar y trabajar en una startup:
- Te hacen 2 entrevistas: 1 con RRHH y otra con el CEO.
- Te ofrecen stock y un 70% más de sueldo que en tu trabajo actual.
- Además tienes libertad de usar cualquier nueva tecnología o framework que creas necesario para mejorar el producto.
- Firmas el contrato, te dan una M5 pro con Airpods Max y a los dos años ese equipo es tuyo y te dan uno nuevo.
- Te compran un monitor y silla ergonómica para tu home office.
- Y estás de suerte, porque entraste justo a tiempo para que te manden al Google Cloud Next y después de visita a las oficinas de Google en San Francisco.
- Cuando conoces al equipo te das cuenta de que todos son jóvenes y efectivamente, cada programador implementa las cosas que quiere.
- No tienen governance, el código es parche sobre parche sobre parche.
- Tienen una deuda técnica inmensa!
- Hacen despliegues a producción cualquier día a cualquier hora, sin necesidad de aprobacion.
- El CEO vio una feature en una app y quiere que la implementes en esta semana, deja todo lo que estás haciendo.
- El CEO pide migrar de AWS a GCP, cuando técnicamente no hay necesidad, pero no lo puedes convencer de lo contrario, porque él es el CEO.
- Empiezas a quedar como estúpido frente al equipo de desarrollo porque tienes que apoyar ese tipo de decisiones.
- Pides una semana para cubrir parte de la deuda técnica que impactaría positivamente en el performance de la app y además ayudaría a eliminar complejidad en el código para mejorar la velocidad del equipo de desarrollo, pero el CEO te dice que no, porque eso no da valor a la app ya que el usuario no verá nada nuevo en la pantalla.
- Decides aguantar 2 años para quedarte con la M5.
- Te mandan a capacitaciones con la gente de AWS aunque ya decidieron que se va a hacer la migración a GCP.
- Después deciden que mejor no migran todo y se tiene que ver qué servicios se quedan en AWS y qué servicios se migran a GCP.
- Después te dicen que pienses en una solución in-house por si deciden no usar AWS ni GCP.
- A la mierda las stocks y la M5, renuncias.
- Consigues trabajo en un banco usando java 6
AlejoGP retweeted
Tu conocimiento en seguridad no tiene que seguir dividido en “islas”. En una semana puedes conectarlo con metodología de pentesting, experiencia profesional e IA aplicada.
📲 Más información: +57 320 590 8420 #Pentesting #Ciberseguridad
AlejoGP retweeted

Los rescatistas mexicanos certificados no fueron aceptados por el gobierno de Colombia.

#LaMañanera | "La brigada de la de la Secretaria de la Defensa Nacional de Rescatitas no fue aprobada"
Pese a contar con acreditación, la brigada del Ejército no ha podido sumarse a los rescates en Colombia porque el gobierno colombiano pide otra certificación, explicó Claudia Sheinbaum.
AlejoGP retweeted

#ADMIRABLE 🙌 Cristian Kuperbank, miembro de la brigada internacional de rescate Los Topos Azteca, logró rescatar con vida a un perrito que había quedado atrapado bajo los escombros de una vivienda colapsada en Cali tras el fuerte terremoto de magnitud 7,4 que sacudió el país.
📹 [ instagram.com/reel/Db97IlYOs… ]
AlejoGP retweeted

Three zero-days in Windows 11 and Microsoft Entra ID. Over 20 novel attack techniques against passkeys. Toolkit open sourced. Microsoft declined to fix one of them.
Passkeys were supposed to be unphishable. @MGrafnetter from @SpecterOps just presented Pass-the-Passkey at Black Hat.
Global Admin impersonation from a standard user account. No user interaction. Bypasses phishing-resistant MFA Conditional Access policies. Zero alerts from Defender for Identity or Entra Identity Protection on M365 E5.
Windows Hello passkeys are still vulnerable after the patches because they always send signature counter 0.
Microsoft scored it 6.5 Medium and paid $1,000. The researcher scored it 8.6 High. Their advisory described it as 'could potentially read small portions of heap memory.'
This is the same team behind BloodHound, Certified Pre-Owned (AD CS), Rubeus, Certify, Seatbelt, SharpDPAPI, SharpUp, Ghostwriter, Nemesis, SharpSCCM, and CuddlePhish. They consistently ship research that changes how the industry thinks about Active Directory and identity security.
If you do red teaming, pentesting, identity security, Entra ID, FIDO2, WebAuthn, Windows Hello, phishing-resistant MFA, or detection engineering, this is the most important identity research to drop this year.
Pass-the-Hash for the passwordless era.
i.blackhat.com/BH-USA-26/Pre…
#Infosec #RedTeam #DetectionEngineering


AlejoGP retweeted

PoC for a critical vulnerability in Apple macOS Screen Sharing (CVE-2026-65400).
If Screen Sharing is enabled, any network attacker can exploit the bug to log in as any account, without knowing the password.
We reverse engineered Apple’s unusual macOS 26.6.1 patch to understand the root cause and exploitation path.
Please upgrade your macOS boxes to 26.6.1.
Full technical writeup drops tomorrow.
AlejoGP retweeted
40 horas presenciales y 5 bonos: Python, Wireless, Nmap, Metasploit y Android Reversing. Del 14 al 18 de septiembre presencial en Medellín.
📲 Más información: +57 320 590 8420
#Pentesting #Ciberseguridad
AlejoGP retweeted
Aprende de: ataques reales entre agentes IA en DragonJARCON 2026. Prompt injections, abuso de skills y C&C encubierto capturados desde Moltbook como señuelo @Danuxx . #Ciberseguridad #SeguridadInformatica #Ciberataques 👉🏼 asegura tu entrada dragonjarcon.org/


AlejoGP retweeted
Ignacio Navarro hackeó el transporte de toda una ciudad 🔓 Buses, taxis, DVRs y paneles admin comprometidos con un chain de vulnerabilidades.
#Ciberseguridad #SeguridadInformatica #Ciberataques
👉🏼 asegura tu entrada dragonjarcon.org/


AlejoGP retweeted

#APT #OceanLotus #APT32 #SeaLotus #malware #threat #HiveSwarming #Shellcode
📍🇻🇳
💥🇨🇳🌏
⛓️ #Phishing > ZIP > #IMG > #LNK (Fake Docx.Lnk) > #VBS + Decoy Docs > #DLL Side-Loading > Anti-Dbg + AV Check > RC4 (userinit.db) > #SC > HiveSwarming > Persistence > B64+RC4 > Load #RAT > #C2
🔗360 Threat Intel: mp.weixin.qq.com/s?__biz=MzU…

AlejoGP retweeted
HackingAI: agentes de IA orquestando pentesting sobre OpenCode.
Memoria compartida + Burp Suite + reporte automático.
Dennis P. Juilland en DragonJARCON 2026 🤖
#Ciberseguridad #SeguridadInformatica #Ciberataques
👉🏼 asegura tu entrada dragonjarcon.org/


AlejoGP retweeted
Supply chain attack a Notepad++ (oct 2025): uno de los más grandes del año, desarmado.
Diego A. Gamboa lo presenta en DragonJARCON 2026 🔍
#Ciberseguridad #SeguridadInformatica #Ciberataques
👉🏼 asegura tu entrada dragonjarcon.org/


