

Mark 8:36 | Full Stack Web3 Dev | Co-Founder @PayoraHQ | All things Crypto, AI and Softwares e-commerce specialist https://xitter.cf/t.co/pQTN8au1Ko building @mwauditor
Trenches
Joined December 2023
- Tweets13.7K
- Following972
- Followers877
- Likes21.2K



npm retweeted

If Carrick cares about this team like he claims, he should resign effective immediately.
npm retweeted

In addition to our earlier alert, the same attack has now been identified on additional sites. These are actively serving the Step Drainer:
• stonkfun[.]xyz
• pickle[.]finance
• echelon[.]market
• origami[.]finance
• fluxbeam[.]xyz
• stakepoint[.]app
• supswap[.]xyz
• longbow[.]cash
• shprd[.]finance
• apexdefi[.]xyz
We’re actively investigating and gathering more data.
npm retweeted

StonkFun was affected by tonight's domain attack on several crypto sites, flagged by @blockaid_.
Please don't visit the site or connect a wallet until we confirm it's safe. The team is working on restoring it now.
This only affected the website. Everything on-chain is working as normal, and we're not aware of anyone affected.
Updates only from this account.

In addition to our earlier alert, the same attack has now been identified on additional sites. These are actively serving the Step Drainer:
• stonkfun[.]xyz
• pickle[.]finance
• echelon[.]market
• origami[.]finance
• fluxbeam[.]xyz
• stakepoint[.]app
• supswap[.]xyz
• longbow[.]cash
• shprd[.]finance
• apexdefi[.]xyz
We’re actively investigating and gathering more data.
npm retweeted

Amplifying again, more domains under attack. Not sure what’s happening but stay safe ya’ll.


npm retweeted

We identified a security incident affecting a modified Claude Code VS Code extension accessed through our Cursor IDE extension marketplace, impacting at most 5,000 users. This malicious version of the extension was not developed by Anthropic. It does not impact other extensions downloaded from the cursor.com/marketplace, Grok Bot, Grok or our other SpaceXSI products.
In response, we took down our extension marketplace this afternoon, worked with relevant providers to neutralize the malware, and have reinstated the marketplace after confirming there is no further risk.
If affected, please review instructions in this blog post to understand how to find the malicious package and establish a path to mitigate any potential impact. We are asking all customers update to Claude Code for VS Code version 2.1.314: cursor.com/blog/claude-code-…
npm retweeted

CZ: we’re finally okay, we’re financially strong.
Female TV reporter: ….??

The Binance $5.6B drain is a masterclass in modern EVM exploitation.
It wasn't a complex logic bug. It was an EIP-7702 delegation hijack:
1. Setup: Attacker funds 0x7c86 via Tornado Cash, deploys a sweep contract (0x63e8), and runs three live dry-runs on external wallets.
2. Execution: Attacker submits an EIP-7702 batch with 50 pre-signed authorizations (nonce n to n+49) to hit Binance 14's moving nonce window.
3. One authorization hits. Instantly, Binance 14 (an EOA) is reprogrammed to run the attacker's contract bytecode.
4. Execution looks totally organic: Binance 14 sweeps itself clean. Internal threshold alerts don't trigger because, from the nodes' perspective, the hot wallet is just executing its own transaction.
5. Binance 16 immediately auto-refills 28,000 ETH due to automated treasury rebalance scripts, feeding the exploit loop.
The cold truth: you cannot forge an EIP-7702 delegation list.
For this to execute, the attacker already held the raw private key or unconstrained signing access to Binance 14's HSM/KMS.
But hey, 5.64 billion drained across ETH, BTC, and Tron. 2.54 billion frozen by Tether, Circle, Ripple, and World Liberty within hours.
Code is law until the stablecoin admin keys log in.
Binance got bailed out by the very centralized choke points the cypherpunks warned you about.
Hardware wallets leak your home address.
Centralized exchanges leak the keys to the kingdom.
Self-custody on native, non-delegated chains remains the only honest baseline.
At least you know what to avoid.
npm retweeted

After years of repeated CEX hacks, I still don’t understand how outgoing transfers of this size can happen without independent human review and signing.
Where are the circuit breakers? Why aren’t unusually large withdrawals automatically delayed, queued for review and subject to additional approval, especially when funds are moving to a new address?
Withdrawing $5,000 from a bank can involve questions and a manager’s approval. Yet somehow, $100 million++++ can flow out of an exchange to an unfamiliar address in seconds.
Make it make sense. Please.

Binance's initial investigation suggests that the security incident may involve a compromised DevOps engineer’s laptop, which allowed an attacker to gain access to a service container and submit unauthorized withdrawal transactions. We have found no evidence of any wallet private key leak. We will share a detailed technical post-mortem once the investigation is complete and the facts are fully verified.
The estimated total impact sits at around $6.3B. We have worked with blockchain partners to freeze affected assets, with ~$3 billion frozen on-chain so far.
Binance will cover all losses from the SAFU fund and the company’s funds. User funds are safe. We will also publish an updated Proof of Reserves once the remediation is complete.
As an immediate precaution, Binance has:
- temporarily suspended deposits and withdrawals while security checks are completed;
- revoked the affected address authorisation;
- engaged law enforcement and blockchain intelligence partners to trace and recover funds.
Our teams are working around the clock to resolve this issue safely and thoroughly. We are working closely with our law enforcement partners to confirm the identity of these criminals and bring them to justice.
Please rely only on official Binance channels for updates. Please feel free to contact Binance Customer Support if you have any further questions.
binance.com/en/support/annou…


npm retweeted

Binance right now

🌍 BINANCE HACKER RACED THE FREEZES
Stablecoins like USDT can be frozen by the company that issues them. ETH can't. So the hacker had about 30 minutes to turn stolen USDT into ETH.
4:34 PM ET: the first swaps start. Market makers on UniswapX (a trading app) bought stolen USDT for ETH, and the hacker paid about 15% over market price for speed. By the time the freezes hit, $729M had been swapped.
4:58 PM ET: the hacker pledges 60M stolen USDT on Aave (a crypto lending app) and borrows 19,762 ETH against it. That ETH went to the hacker's wallets. The USDT stays stuck in Aave.
5:01 PM ET: Tether and Circle start freezing. $2.7B is now blocked.
-> hacker was 3 minutes faster
5:42 PM ET: Aave freezes its markets, but the loan stays open. Aave says the collateral covers it, so lenders aren't at risk.

npm retweeted

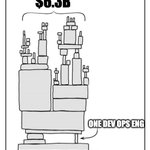
Binance security team showing up to the incident review after leaving billions of $ on a hot wallet that a single dev ops engineer could move.
Binance's initial investigation suggests that the security incident may involve a compromised DevOps engineer’s laptop, which allowed an attacker to gain access to a service container and submit unauthorized withdrawal transactions. We have found no evidence of any wallet private key leak. We will share a detailed technical post-mortem once the investigation is complete and the facts are fully verified.
The estimated total impact sits at around $6.3B. We have worked with blockchain partners to freeze affected assets, with ~$3 billion frozen on-chain so far.
Binance will cover all losses from the SAFU fund and the company’s funds. User funds are safe. We will also publish an updated Proof of Reserves once the remediation is complete.
As an immediate precaution, Binance has:
- temporarily suspended deposits and withdrawals while security checks are completed;
- revoked the affected address authorisation;
- engaged law enforcement and blockchain intelligence partners to trace and recover funds.
Our teams are working around the clock to resolve this issue safely and thoroughly. We are working closely with our law enforcement partners to confirm the identity of these criminals and bring them to justice.
Please rely only on official Binance channels for updates. Please feel free to contact Binance Customer Support if you have any further questions.
binance.com/en/support/annou…
npm retweeted
Drained $5.6B from Binance using bleeding-edge EIP-7702 batch signatures.
Caught because MetaMask default-selected "pay gas with USDT" and logged their IP on ConsenSys servers.
You couldn't write a better script:
- Wallet had 1.75B USDT and 2 native ETH ready for gas.
- In a panic, the operator blindly clicked confirm without noticing MetaMask's smart gas station.
- MetaMask relayer paid the ETH, charged 127 USDT, and logged the raw client request on their backend API.
Advanced chain exploitation defeated by Web2 frontend UX.
One more thing to avoid.

The Binance $5.6B drain is a masterclass in modern EVM exploitation.
It wasn't a complex logic bug. It was an EIP-7702 delegation hijack:
1. Setup: Attacker funds 0x7c86 via Tornado Cash, deploys a sweep contract (0x63e8), and runs three live dry-runs on external wallets.
2. Execution: Attacker submits an EIP-7702 batch with 50 pre-signed authorizations (nonce n to n+49) to hit Binance 14's moving nonce window.
3. One authorization hits. Instantly, Binance 14 (an EOA) is reprogrammed to run the attacker's contract bytecode.
4. Execution looks totally organic: Binance 14 sweeps itself clean. Internal threshold alerts don't trigger because, from the nodes' perspective, the hot wallet is just executing its own transaction.
5. Binance 16 immediately auto-refills 28,000 ETH due to automated treasury rebalance scripts, feeding the exploit loop.
The cold truth: you cannot forge an EIP-7702 delegation list.
For this to execute, the attacker already held the raw private key or unconstrained signing access to Binance 14's HSM/KMS.
But hey, 5.64 billion drained across ETH, BTC, and Tron. 2.54 billion frozen by Tether, Circle, Ripple, and World Liberty within hours.
Code is law until the stablecoin admin keys log in.
Binance got bailed out by the very centralized choke points the cypherpunks warned you about.
Hardware wallets leak your home address.
Centralized exchanges leak the keys to the kingdom.
Self-custody on native, non-delegated chains remains the only honest baseline.
At least you know what to avoid.
npm retweeted

I’m giving away 7 GTD + 10 FCFS spots for the @Variant_nft NFT mint to the community!
Project Details
Chain: Robinhood
Supply: 6666
Mint Date: TBA
Price: TBA
About Variant:
This is a one face, Infinite variants.
Same base character endless unique skins, eyes, outfits, elements, and sidekicks.
How to Enter
✅ Must Follow @Variant_nft x @Finance__Nomad
✅ Like & RT this post and the project pinned post →
✅ Drop your EVM wallet in the comments and tag one friend.
• Winners will be selected within 36 hours


NFTs got boring.
We’re changing that.
Variant
One face. Infinite variants.
Grab WL → vrnt.fun
Submit your EVM
Very limited spots. Don’t sleep.

npm retweeted

GIVEAWAY LIVE for 3x @HoodVandalz 🔥 🎬
@geeduppppp has been showing up, and the project is on absolute heat! 🔥
RULES:
Be Following @iamaurel1us and @HoodVandalz!
1. Drop a comment below on why you need a Hood Vandal in your wallet.
2. Tag 2 Friends
3. Like and Repost
I am picking 3 lucky winners to claim one each! 🎟️
⚡ Bonus points for the most solid reason!

npm retweeted

A little world. A new onchain frontier.
Lotlings goes live on @Enter_elysium on Nov 9, 3 PM UTC.
Your place in this world starts here:
- lotlings.io
npm retweeted

Access Pass Giveaway!
Prize 🏆: 1 Fomies Access Passes
Winners: 10
Requirements:
1️⃣ Like + RT this post and pinned post
2️⃣ Follow @FomiesNFT + @onlydotmeme
3️⃣ tag 3 friends
Winners in 48 hours.
Do not ask about the pickles.

npm retweeted

🚨 @Claynosaurz | Popkins Giveaway 🚨
I’m giving away Popkins #279 to one lucky winner
Rules to enter are simple: ⬇️
1. Like & Repost
2. Follow me @draxsui
3. Tag two friends
The winner will be randomly selected by Grok to ensure fairness
All rules must be followed to be eligible to win
Draw is in 72 Hours ⏳
Goodluck all! 🍀

npm retweeted

Streethood evening robinhood 🟢
Giving away WL spots for
COMPANIONS 🐾
🎟️ 10 GTD spots
🏃 20 FCFS spots
To enter:
~ like + RT + comment
~ Join: quest.wfitapp.xyz/?ref=AVI-C… and complete your profile
WFit Companions are digital partners built to move, explore and grow with you — with future GPS hunts, surprises and real utility. 🌍
The Labyrinth is waiting. 👀🔥

npm retweeted

okay, this is damn sick
literally feels like sitting in an airplane cockpit
@birdeye_so just rebranded its tracker to Birdeye Terminal
liquidity, holders, smart money, execution, etc.
literally the best tool to stop buying garbage and finally make money
🤝 Paid partnership


You already use Birdeye to check tokens. Now it's sharper: price action the moment it happens, 0s indexing, in a rebuilt terminal.
Meet Birdeye Terminal: birdeyeterminal.com
Same eye. Sharper sight 🧵