

Vulnerability researcher | Fuzzing | Anything low-level excites me | Admin @ https://xitter.cf/t.co/DjVsvNNdjS | My tweets are my own | Bsky: https://xitter.cf/t.co/0uGccMaOJW
127.0.0.1
Joined May 2017
- Tweets914
- Following545
- Followers3.7K
- Likes2.2K




Pinned Tweet
For the time being here is the 4th and final part of my little D-Link reversing blog: 0x00sec.org/t/breaking-the-d…
434B retweeted
How to break secure boot without touching any cryptography 0x434b.dev/breaking-secure-b…

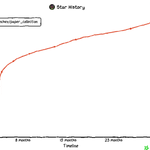
Did a massive overhaul of this last month. More papers, more metrics and a neat graph visualization :)!

Just hacked some AI wizardry to tame my paper collection. Check it out: aischolar.0x434b.dev (based on github.com/0xricksanchez/pap…). Ideas welcome!
I just received 5 coffees from e4cu on @buymeacoffee! buymeacoffee.com/0xricksanch…

Random weekend project of the month: Take an old Perl script and claim you can do better than that if you write it in Rust github.com/0xricksanchez/SMT…

434B retweeted

Have you found some vulns, bypassed detection, or done some cool research the past year you haven't already blogged? Submit to @phrack! Deadline is June 15 for the 40th Anniversary Edition, we're printing 1000s of copies worldwide free at cons & online! Be a part of history!

Recently learned about vulnerable.codes/, which teaches you code auditing. Nice to see more educational platforms popping up. Rn, it's heavily supported with content from @XenoKovah and @OpenSecTraining, but if it keeps expanding even beyond C/C++ it could be very nice :)!
Just hacked some AI wizardry to tame my paper collection. Check it out: aischolar.0x434b.dev (based on github.com/0xricksanchez/pap…). Ideas welcome!
Small QoL feature release to my Shellcoder #BinaryNinja plugin. Now every time you run it the architecture is automatically set based on the currently selected binary/database github.com/0xricksanchez/She…

github.com/0xricksanchez/AFL… just got more rusty, stable, (hopefully) easier to maintain and contribute to. Also, we have a bunch of new features like deterministic generation and fuzzing modes :)!

Having some fun with an old CVE to explore ARM TrustZone more. Having no proper debuggability can really be a nightmare, especially when the MMU/caching is involved. Cool research by @raelizecom

Remember kids, when you're stuck on the technical part of your exploit, the only way to continue is to handcraft sick ASCII art for the exploit in case you ever manage to finish it!


Now also available on the official plugin manager from within #BinaryNinja! Thanks @psifertex :)
Fun little weekend project to implement something like @JonathanSalwan's ShellStorm assembler/disassembler in pure #Binaryninja.
Repo: github.com/0xricksanchez/She…

Fun little weekend project to implement something like @JonathanSalwan's ShellStorm assembler/disassembler in pure #Binaryninja.
Repo: github.com/0xricksanchez/She…
Just made some nice improvements to AFL_Runner a little tool for easy/best-practice multicore @aflplusplus fuzzing campaigns: github.com/0xricksanchez/AFL…. Now with a TUI as a replacement for afl-whatsup as well. New stuff planned :)

434B retweeted

#tools
#Fuzzing
AFL_Runner - tool to streamline running efficient multi-core AFLPlusPlus campaigns
github.com/0xricksanchez/AFL…
After how many side-projects do you get side-tracked back to your main project? Asking for a friend???
'admin!' and '123456' it is. Take it or leave it


Anyone want to donate this to me for fuzzing research? I could need some of those 145152 cores to run some fuzzers only to not find new crashes gsaauctions.gov/auctions/pre…


Pushed some fixes and the latest release, v0.3.4 should be rather stable now again...
On a side-note: if you're one of those people who prefer screen to TMUX, then you have that available now as an option :)!