

sky is the limit
0xffffffe
Joined March 2013
- Tweets2.7K
- Following57
- Followers3.7K
- Likes363



Is there any way to access this model? I’ve tried subscribing multiple times via openai.com/ar/daybreak/, but my country isn’t supported.
@sam @fouadmatin @thsottiaux


Introducing GPT‑6 Cyber: a major advance in security research that pairs stronger capabilities with better model alignment.
The model powered the Linux kernel research we announced yesterday, and security teams at companies like Mozilla, Palo Alto Networks, Calif, and Cisco—alongside our own at OpenAI—are already putting it to work.
GPT-6 Cyber is available to select Daybreak Red customers and we are expanding access over time.
openai.com/index/introducing…
461


Ahmed Aldeab retweeted

Since the @Apple Bug Bounty Program is by far the worst program I've ever hacked on, I am going to be dumping all of the data/POCs/report write ups etc for everything found during the 4 months of hacking them. This will include POCs for vulns that didnt meet their bar for a bounty so wasnt reported to them, so you may be able to find ways to escalate some of them. Ill be uploading the data all this weekend.


Ahmed Aldeab retweeted

As others noted, Apple patched the not-so-secret server side bug. It enabled root access and jailbreaking even on iOS 27.2b3 (18 Pro Max). A public release would've meant an instant patch, so it stayed private. Despite efforts to preserve it, it's cooked. RIP 🪦😭


للاسف ابل اصلحت واحدة من اقوي الثغرات " لم تكن متاحة للعامة" هذه الثغرة تسمح لك بعمل جلبريك لجهازك مهما كان الاصدار الخاص بك لان الثغرة وبشكل اساسي كانت –– serverside bug والان تم الاصلاح!
- علي كل حال هيا هكي او هكي ماكانتش متاحة للعامة 🤷🏻♂️


Ahmed Aldeab retweeted

probably details will be shared in the following days, im not doing it since it’s not my discovery, but to summarize this was a serverside bug that is now patched
Ahmed Aldeab retweeted

BREAKING NEWS
The Royal Swedish Academy of Sciences has decided to award the 2026 #NobelPrize in Physics to Francis Halzen “for decisive contributions to the IceCube Neutrino Observatory and the discovery of high-energy neutrinos of astrophysical origin.”

Today I attended the first lecture of the Advanced Quantum Mechanics course, a graduate-level offering.
- اليوم كانت محاضرتي الاولي في مكانيكا الكم المتقدمة - دراسات عليا.

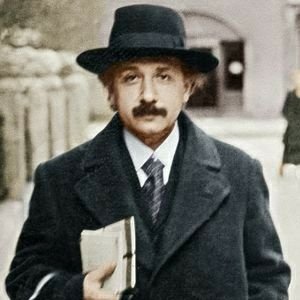
From left to right, physicists Albert Einstein, Hideki Yukawa, John Wheeler, and Homi Bhabha in conversation as they walk through Marquand Park in Princeton, N.J, 1954.

512
السلام عليكم،، شباب من اللي يقدر يساعدني
عندي حسابي الباي بال فيه فلوس حوالي 50 دولار، ومانقدرش نسحبهم الا لبطاقة .
اي حد عنده بطاقة نحوله الفلوس عليها ويحولي usdt
وشكرا
1
871
Ahmed Aldeab retweeted

Found a great RCE in OneDev with @Vulnetic24. Two admin-only settings endpoints take @Valid beans, so JAX-RS runs bean validation before isAdministrator(). Those fields carry @Code, and validating them compiles Groovy. The bundled runtime ships ASTTest, whose closure runs at compile time, before the script is ever invoked. Validation and execution become the same operation, under the caller's identity.
Sable caught it from one 400 where every other endpoint returned 403. A 400 means the body was validated before the caller was rejected. Confirmed root execution on two separate compile paths. Nothing persists; it all runs inside a request the server thinks it denied.
Read the full writeup below 👇
من الأدوات الفعّالة في البحث الأمني وكشف الثغرات في المواقع وتطبيقات الويب
توفر قدرات سيبرانية متقدمة مع مرونة عالية بدون قيود
مع Vulnetic حدّد المهمة واترك الأداة تتولى البحث والكشف
مثال على ثغرة حرجة للغاية تم اكتشافها: RCE مع وصول Root
رغم استجابة 403
vulnetic.ai/blog/groovygate-…

1
4
623