

Partner @y2z_ventures | Founding Member @DewhalesCapital | Cooking in stealth
Joined May 2018
- Tweets2.1K
- Following6K
- Followers15.6K
- Likes4.9K



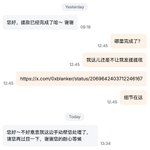
这波感觉Binance没啥问题,但是这个回复感觉越抹越黑了,我大概看懂了,冒昧中译中一下。
Binance Global用户有一套UID.A,Binance TH用户有一套UID.B,两个站完全就是独立站(不能通过UID转账),两边就是存在用户UID一样的情况,就像你的QQ号和Binance UID也有可能一样。
这个用户从Binance Global想转账到Binance TH的账户,因为不知道两个站点是独立站,所以用了UID转账(但其实不互通的),输入了Binance TH的UID,但是这个UID在Binance Global是对应另一个用户的账户。转账的时候其实会弹出二次确认,要用户检验收款账户的用户名是否一致,这一步其实是能发现问题的。
Binance作为金融机构在没有授权的情况下不能直接转走已经收到资金的用户资产,只能冻结后帮转错的用户联系Global这边的用户确认退回,或者等待执法机构介入配合。

每个人在币安都只会有一个UID,且是独立的,并不存在撞号。我理解你的感受,从联系我开始到现在,全程我和4个员工跟踪了前因后果。
我简单描述一下背景:您把币安的钱转到币安(泰国),正常这属于跨站转账,需要用地址或者二维码,但你在转账过程中在币安直接输入UID转账,虽然我们有二次确认环节,但你没有仔细看。你发现转错后,直接找了我。我本人和4个人的团队一直在协助,第一时间帮忙冻结了这笔钱,但因为这个收到钱的持仓用户并不活跃,我们也在反复联系对方,但对方没有响应。我们做了应该做的,甚至设身处地考虑你打错了钱会着急,所以尽可能帮忙。
对方并不是犯罪,是您打错币,如果对方坚持不退只能我们客服介入谈判。你着急,我们建议让你通过报警执法介入,我们再协助沟通。但你在泰国报警,您在您希望收款的泰国报警要求币安主站把另外一个国家的币安用户的资产直接划拨给你,这不符合执法流程,报警应该在你希望找的用户国家所在地而不是泰国。
之前处理过很多打错币的情况,大额打错几千万美金,也是我们及时拦住帮忙追的,而且当时用户坚持不退,也是我们协助谈判,最后到双方能接受的范围和解。
我理解你的难处,团队也一直在跟踪进展,得到的就是这篇长文,我们会继续联系另外一个用户协商,但你打错币这事儿,在泰国报警确实帮不上忙,那是你的钱想去没去成的目的地。
最后提醒大家,币安土耳其,币安泰国,币安美国等本地法币交易平台是独立平台,并不共享账号系统,日常转账提币时请仔细检查地址和UID。

我看完了全程和何一@heyibinance 的解答,还是要说句公道话,我觉得币安产品设计一点问题没有。
败笔就是何一自掏腰包补了这部分亏损,我觉得完全不该补,也能理解,本身客户转错钱不多,不想讨论这种没有意义的东西,更好的策略可能是:「感谢这位用户发现的bug,我们无法帮你找回钱,但是我们愿意将其作为产品的bug赏金,给予等额或者加一点的奖励」。
如果真要挑产品毛病说,只能说没人能想到有用户会傻到同品牌跨app转账,因为本质上是3个不同的app,在用户心智这块,币安这个品牌太成功了,能做到让用户把3个产品当币安主战用。
另一个就是大众对币安的认知最多是币安+us币安,但是真在美国的话用的大概率是hood和coinbase,所以一般人根本触发不了这种情况,币安泰国我是真没听说过,更不知道有人会装两个app互相划转用。
合理处理路径就是币安要等监管机构的相关手续才能处理,不然私自替用户划转,收款方发现自己账目+xxxx usdt之后又减去了,这怎么解释,而且币安真要敢划你钱怎么跟监管解释,合理方式就是报警。
这个事情可以理解为就是用户用支付宝人民币转错款了,收款方如果就是不退,就是要双方协商的。
因为《用户协议》都约定好了,币安也不是什么过错方,谁能想到你能去把三个名字都不一样的app给当成同名转账啊。
按闹分配时代了,大家都不想讲道理了。
万万没想到在高铁上闲着没事随手发的一条帖子能这么多人讨论...快给我忙成币安客服了😇

这波感觉Binance没啥问题,但是这个回复感觉越抹越黑了,我大概看懂了,冒昧中译中一下。
Binance Global用户有一套UID.A,Binance TH用户有一套UID.B,两个站完全就是独立站(不能通过UID转账),两边就是存在用户UID一样的情况,就像你的QQ号和Binance UID也有可能一样。
这个用户从Binance Global想转账到Binance TH的账户,因为不知道两个站点是独立站,所以用了UID转账(但其实不互通的),输入了Binance TH的UID,但是这个UID在Binance Global是对应另一个用户的账户。转账的时候其实会弹出二次确认,要用户检验收款账户的用户名是否一致,这一步其实是能发现问题的。
Binance作为金融机构在没有授权的情况下不能直接转走已经收到资金的用户资产,只能冻结后帮转错的用户联系Global这边的用户确认退回,或者等待执法机构介入配合。
WTF

*sshole is out
if you run sshd on alpine, openwrt or any musl box with password auth on: update now
official writeup: sshhole.com
🙏
Regarding criticism and suggestions about Binance’s security and access management, we accept them all. We have always believed that transparency builds trust. We read every comment one by one. Binance is not a perfect company, but a company that is constantly evolving. Criticism shows that people have expectations and standards for Binance, and these are sources of motivation for our growth.
Binance has never shirked responsibility where problems exist. At present, as a trading platform, Binance needs to address three issues:
1)Will users’ funds be affected? Binance will bear full responsibility,this is what we should do. Legally, if the funding gap is large, one could file for bankruptcy and run away, but Binance operates in a “user-centric” way, with contractual spirit and a sense of moral responsibility.
2)How did the problem occur? Before publication, many professionals advised that it would be best not to include details, but we believe transparency creates trust. If this report is of reference value to other peers regarding the complexity of social engineering and the warning about AI permission boundaries, then the report is meaningful.
3)How can it be prevented in the future? We have already restructured security boundaries across departmental access management, security environments, updated devices, reset AI tools, and in accordance with zero-trust and least-privilege principles. A security audit will subsequently issue a report.
Finally, we welcome more top AI security experts and technical talent to join Binance. You can DM me directly or apply on the Binance website for positions you are interested in. Joining Binance to verify this security system is the best way to validate it.
关于对币安的安全和权限管理的批评建议,我们都认。我们一直相信坦透明会建立信任,大家的评论都有一条一条看,币安不是完美的公司,但是一个一直在进化的公司,批评说明对币安有期望,对币安有标准,这些都是我们成长的动力源泉。
币安有问题的地方也从来没有推卸过责任。当下,币安作为交易平台需要解决三个问题:
1)用户的钱会不会受影响?币安会完全承担,这是我们应该做的。法律上资金缺口大可以申请破产跑路,但币安经营是“以用户中心”,是契约精神和大义。
2)问题是怎么发生的?发布前很多专业人士的意见是最好没有细节,但我们认为透明产生信任,如果这个报告在社会工程的复杂度,在AI权限边界的警示对其他同行有参考意义,那么这个报告就有意义。
3)以后如何杜绝?当前已经从各部门权限管理,安全环境,更新设备,重置AI工具,并遵循0信任、最小化原则重构安全边界,后续会由安全审计出具报告。
最后欢迎更多顶尖的AI安全专家和技术人才加入币安,您可以直接DM我本人,也可以在币安网站申请你感兴趣的岗位。加入币安来验证这套安全体系是最好的验证办法。
我非常喜欢币安,但不得不说这实在有点太草台了…
2020年我刚接触crypto是在火币实习,火币当时就是所有员工强制用堡垒机+动态MFA+离开座位必须锁屏,我一直以为这是币圈交易所的标配,直到看到这篇复盘,才发现当年的火币在这方面竟然领先行业至少6年😇

仅时隔一个月,又出现同一个问题,但这次DM @CoinbaseSupport 的时候发现不管什么时候DM他们都是秒回(上次平均要2-3个小时才回复),感觉大概率是接入AI了,而且权限非常高,现在客服处理的体验有点太好了!
当然,如果不再给我弹KYC就更好了😅看看这次能坚持多久...


blanker retweeted

Ledger isn't the only one, @Trezor devices sold by CryptoBilis also had an implant.
IMPORTANT: If you bought a Trezor from CryptoBilis from March 2026 onwards and are using it to store funds, please move your funds to a newly created wallet with a new seed as soon as possible.
If you have a device you are unsure of, DM me. I'll happily cover shipping fees and analyze your device.
trezor.io/blog/news/implant-…

blanker retweeted

I suspect IBIT is already on North Korea’s shortlist.
In February 2025, the attackers behind the Bybit hack compromised a Safe{Wallet} developer’s Mac through a malicious project disguised as legitimate Docker-related tooling. They had access for 17 days before the theft, giving them enough time to manipulate the transaction interface used by Bybit’s signers. The signers believed they were approving a legitimate transaction. Instead, they unknowingly authorized the theft of $1.5 billion from a cold wallet.
The keys could stay offline while the signers approved a theft through a compromised interface.
TRM Labs attributes the recent Binance incident with high confidence to TraderTraitor, the North Korean group also linked to Bybit and the theft of 4,502.9 BTC from DMM Bitcoin. Binance’s preliminary investigation points to a compromised DevOps engineer’s laptop as the entry point. Binance says there’s no evidence that private keys were leaked, while TRM’s analysis suggests the attackers may have gained control of the signing infrastructure. If confirmed, the attackers could have moved funds through a compromised approval process without extracting the keys.
Now imagine the same thing happening to IBIT.
BlackRock’s IBIT is the world’s largest Bitcoin ETF, holding roughly 815,000 BTC worth around $63 billion. Coinbase remains its active Bitcoin custodian. Although Anchorage Digital has been appointed as an additional custodian, the fund’s latest quarterly filing says there are currently no plans to transfer any Bitcoin there.
That’s an extraordinary concentration of Bitcoin under one custodian. Regardless of how large or well-funded that provider is, a critical failure in its security infrastructure could put the entire fund at risk.
A $6 billion theft would wipe out roughly 9.5% of IBIT’s assets, equivalent to around $4 per share at current valuations.
Binance managed to freeze some stolen stablecoins. Bitcoin has no such mechanism, making stolen BTC far harder to recover.
BlackRock doesn’t separately insure the Bitcoin held by the fund. Coinbase has disclosed $320 million in commercial crime insurance coverage, shared across its customers. Its custody agreement also limits liability to $100 million per cold storage address, with any recovery subject to contractual terms, liability determinations, and other conditions.
If a major theft occurred and the fund couldn’t recover the Bitcoin or obtain sufficient compensation, the remaining losses would ultimately be borne by IBIT shareholders.
Bitcoin ETFs have made owning Bitcoin much more accessible, and there’s real value in that convenience. But as more capital flows into these products, enormous amounts of Bitcoin are also being concentrated among a handful of custodians and the infrastructure they depend on.
The larger these pools become, the more attractive they are to attackers. A compromise at any critical point could have consequences far beyond a single institution.
And that’s why security has no finish line.
Even the most sophisticated cold storage setup still depends on hardware, software, supply chains, signing workflows, and the people operating them. Keeping private keys offline is essential, but it doesn’t eliminate the risks surrounding the transaction approval process.
Spread your assets across independent custody setups. Keep your private keys offline. Verify transaction details on a trusted device screen, independently of the computer initiating the transaction. Continuously review your security architecture, and build it around the assumption that some part of your infrastructure will eventually be compromised.
There are no silver bullets in security, and no permanent guarantees. Stay vigilant, keep verifying, and never mistake a clean track record for proof that you’re safe.
Bunker mode.


blanker retweeted

Ledger is investigating reports of loss of funds from users in South East Asia who purchased products from a reseller named CryptoBillis. As a precaution, and pending the results of our investigation, we have asked CryptoBilis to pause all sales and shipments of Ledger devices. We recommend Ledger users who purchased from this reseller in the last 90 days to not initiate set up if you have not done so yet. If you have set up your Ledger device, consider moving assets to a new Ledger signer (with new seed). We will continue to inform customers of updates as the investigation progresses.
Reach out to Ledger customer support through official channels with any questions: support.ledger.com/
我被Claude无情封号不退款,都还继续注册Claude新号接着用,就是因为即使有概率封号,Claude都比OpenAI更值,只要能用满2周的用量就是血赚!
xitter.cf/0xblanker/status/21027…

#AI
OpenAI 套餐越来越缩水,吐口唾沫走人就完事了。
看到那些说自己是忠实用户,感到寒心的,就有点搞笑了😂
好像在说自己为公司付出了青春,为什么工资一直不涨。其实没人不让你辞职啊。
怎么花钱还花出服务员心态来了,花钱啊,你是在花钱啊,连花钱都不知道用脚投票吗……