

Privacy for people who have other things to do. We fit privacy around your life, not the other way around.
British Virgin Islands
Joined April 2018
- Tweets4.4K
- Following62
- Followers7.3K
- Likes2.8K



Pinned Tweet
A stranger may already know your address, age, and family. Find out with a free scan:
identity.purevpn.com
When a familiar voice asks for money, verify the emergency through a number you know.
AI can imitate voices, and exposed details can make a scam sound real.
#ProtectYourCircle #PureVPN
🚨 A Linux backdoor designed to stay invisible.
Dubbed CWPdoor, the malware hides inside Control Web Panel's server software, allowing attackers to execute commands through specially crafted requests without leaving entries in access logs.
Even routine server activity can hide something far more dangerous.
#CybersecurityNews #Linux #infosec
A password can become the backdoor. 🔓
OpenSSH has issued an emergency fix for a critical flaw that could let attackers bypass SSH authentication on vulnerable Alpine Linux servers using passwords between 257 and 1,024 bytes.
If you run affected systems, update to OpenSSH 10.6p2 immediately.
One overlooked vulnerability is all it takes to compromise a server.
Stay informed. Stay protected.
#CyberSecurity #OpenSSH #DataSecurity #LinuxSecurity #Vulnerability #OnlinePrivacy #StaySecure #PureVPN
🚨 A patched Apple vulnerability is back in the spotlight.
CISA has flagged active exploitation of an Apple security flaw as hackers use compromised websites, fake domains, and malicious scripts to deliver information stealing malware.
The campaign, linked to Russia backed APT29, targets browser cookies and sensitive device data.
Even patched vulnerabilities can remain a threat when devices aren't updated.
#CyberSecurity #Apple #privacy
A fridge hack targeting France's blood supply? 🚨
Hackers reportedly changed freezer settings at Coolworld, an EFS contractor, from -30°C to 110°C.
An on call technician caught it before any operational impact was reported.
When cyberattacks reach physical infrastructure, the stakes go beyond data. They can put critical services at risk.
#CyberSecurity


A WordPress update window could be all it takes for hackers to get in.
CISA has confirmed active exploitation of a high-severity WordPress Core flaw (CVE-2026-119977) that can let unauthenticated attackers execute code on affected servers.
If your site runs WordPress, make sure it's patched.
#CybersecurityNews #WordPress #Vulnerability
What happens when schools say no to AI?
According to reports, K-12 school districts that block Google's generative AI tools could also lose access to an AI-free version of Google Search.
A bigger question follows: Should access to essential search tools depend on accepting AI features?
#privacy #GoogleAlerts

Google said K-12 school districts that block its generative artificial intelligence tools will also lose the ability to use an AI-free version of Google Search.
Read more: forbes.com/sites/maryroeloff…
📸: Matthias Balk/Picture Alliance via Getty Images

An old security flaw. A new ransomware problem. 🔐
Hackers are targeting Synology NAS devices running outdated DiskStation Manager (DSM) software, exploiting a vulnerability patched back in December 2024 to encrypt stored data and demand ransom.
If you use a NAS, update DSM immediately, enable automatic updates, and keep secure backups.
#Cybersecurity #Ransomware #DataSecurity
Your crypto security deserves a closer look. 🔐
Hackers are exploiting a BTCPay Server vulnerability to steal Bitcoin and Litecoin from hot wallets running older versions.
The reminder? Keep software updated, limit funds in hot wallets, and never overlook security patches.
#Cybersecurity #CryptoSecurity #Bitcoin
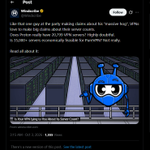
Attackers are exploiting a critical Siemens vulnerability to plant remote command backdoors.
The flaw (CVE-2026-58115) carries a CVSS score of 10.0 and affects SIMATIC IoT2050 Advanced devices running Industrial OS with Node-RED installed.
Organizations are urged to secure affected devices and apply available fixes.
🤖 Made with AI

Please stop using your birthday as your password. Your Facebook friends have been celebrating it publicly for years.😭
#privacymatters
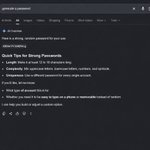
Someone searching “generate a password” is probably trying to make their account safer. They shouldn’t have to wonder whether the “strong, random password” in an AI Overview is also being suggested to someone else.
That’s the concern with this answer. A password can look complicated without being safely generated. Symbols and capital letters aren’t proof. Neither are a few changed characters.
Please don’t ask AI search to create your passwords or use its suggestions for your accounts. Use a trusted password manager to generate a fresh, unique password for each one.
If you’ve already used a password from an AI search answer, replace it.
Share this with someone who might take that answer at face value. They’re trying to protect their personal life. They deserve guidance they can trust.

Going to Reddit for answers? You might soon need an account before getting to the comments. 👀

Reddit is announcing a huge shift: It’s going to start requiring users to log in. Reddit is becoming a ‘logged-in-only experience,’ says CEO Steve Huffman theverge.com/tech/1022571/re…

You updated your OS. Your VPN decided to take a break. 💻
VPN not working after a Windows or macOS update?
Here’s why it happens and what may help.
Read the blog: purevpn.com/blog/vpn-not-wor…
#PureVPN #VPNtips

A $6.3 billion reminder that cybersecurity has no room for weak links.
Not even one compromised laptop.🔐

Binance's initial investigation suggests that the security incident may involve a compromised DevOps engineer’s laptop, which allowed an attacker to gain access to a service container and submit unauthorized withdrawal transactions. We have found no evidence of any wallet private key leak. We will share a detailed technical post-mortem once the investigation is complete and the facts are fully verified.
The estimated total impact sits at around $6.3B. We have worked with blockchain partners to freeze affected assets, with ~$3 billion frozen on-chain so far.
Binance will cover all losses from the SAFU fund and the company’s funds. User funds are safe. We will also publish an updated Proof of Reserves once the remediation is complete.
As an immediate precaution, Binance has:
- temporarily suspended deposits and withdrawals while security checks are completed;
- revoked the affected address authorisation;
- engaged law enforcement and blockchain intelligence partners to trace and recover funds.
Our teams are working around the clock to resolve this issue safely and thoroughly. We are working closely with our law enforcement partners to confirm the identity of these criminals and bring them to justice.
Please rely only on official Binance channels for updates. Please feel free to contact Binance Customer Support if you have any further questions.
binance.com/en/support/annou…


Discord messages from certain public servers could soon appear in Google Search.
AI-generated summaries are coming, too.
The change isn't platform-wide, but it raises an important question: how far can your online conversations travel?

Our marketing team: “PureVPN deserves more attention.”
Forbes Advisor: includes us among its top three VPN picks.
Our marketing team is now unbearable. 🫣

Protect your peace, protect your passwords, and don't click suspicious links. 🫡
#TuesdayMotivaton
Zero-days don’t wait for convenient patch windows.
If your stack depends on PHP, this is one to act on now: identify exposed systems, patch immediately, and prioritize anything internet facing. 🔐
#CybersecurityNews #PHP2Shell #zeroday

‼️ PHP Releases New Windows Build Security Updates to Fix Critical HTTP2Shell Vulnerability
Details: cybersecuritynews.com/php-ht…
The PHP team has released updated Windows builds to fix a serious flaw known as HTTP2Shell. The new packages are PHP 8.5.12-1, 8.4.27-1, 8.3.36-1, and 8.2.35-1, and PHP announced them on October 26, 2026. Each build now includes Brotli 1.2.1, which fixes CVE-2026-111497. Windows users who run PHP should install these packages without delay.
The flaw sits in Google’s Brotli library, a compression tool that many programs use to unpack data. It is an out-of-bounds write, which means the code writes data past the memory area it was meant to use. PHP’s own advisory explains how the flaw reaches PHP on Windows. The vulnerable decoder can be reached through the cURL extension when automatic HTTP response decompression is turned on.
#CybersecurityNews
