

UNLICENSED BROKER OF BITCOIN Working on @FrostsnapTech npub1xh897wvhn93tda0zws94mdyc7eagc8qm0798clp7x48zh6kjwa
Malaysia
Joined September 2013
- Tweets2.8K
- Following1.3K
- Followers3.2K
- Likes16.7K





Pinned Tweet
Upgrade your frostsnap app. And upgrade the firmware on your devices when you can.

Frostsnap v0.4.0 is out ❄
It fixes two security issues. We know of no user funds lost to either, and each has a published report. Update your app and device firmware.
Also: firmware downgrade protection and dozens more fixes.
frostsnap.com/security/updat…

Zero-Knowledge Goof❄️ retweeted

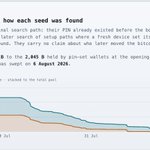
CLAUDE FOUND THE SEEDS
anthropic.com/research/ecdsa…

Zero-Knowledge Goof❄️ retweeted

Announcing LayerTree: a new tree-based scaling solution for Bitcoin that permits O(1), independent of the number of users in the system: xitter.cf/lightning/status/21108…
A single UTXO can hold the balance of millions of users as an off-chain Merkle-sum tree.
Transaction introspection techniques permit batched exit from the system in a single transaction w/o any pre-signing: layertree.tech

Introducing LayerTree, a non-custodial scaling solution on bitcoin that connects to Lightning.
Using covenants, one UXTO can be shared by a million users. Any user can leave at any time in a single transaction. Users don't need to be online to receive. Funds never time out.
LayerTree is the next step in bringing bitcoin to billions.
Learn more: layertree.tech
Zero-Knowledge Goof❄️ retweeted

It's remarkable that the Ledger supply chain infiltration was able to grow to the scale it did given that we were aware of these implants ~6 months ago (thanks @joegrand!)

Reverse Engineering a Ledger Nano X Hardware Implant (@_TROPICON) slides are up! grandideastudio.com/portfoli…

ALT A real-world hardware implant discovered inside of a Ledger Nano X cryptocurrency wallet
WARNING: do not leave your tamper evident bags unattended near @sakak_musdom.
While waiting for an uber at the frostsnap factory I gave him a mk3 in its original bag as a parting gift. Before the uber had arrived he had completely disrespected its bag.
Don't be like him. Make sure to leave evidence when you tamper with hardware wallet packaging. It's part of the ToC.
The simplest way to solve the ledger implant problem: When displaying 24 word backup do not show all 24 on the device. Show 12 on the device screen and send 12 encrypted to the companion app which shows them on the screen. Record them on the same card. Easy :^)
IIRC google’s result implies can break your keys in mempool with non-noisy superconducting circuits in ~5mins so hashing doesn’t protect you. Now the next pleb slop should be that you should have a 10-of-10 multisig even with a single seed to give you 50mins of protection.
Zero-Knowledge Goof❄️ retweeted

I wasn’t going to comment since this is a really bad take IMO, but since it’s taken off I feel the need to. To my understanding, there is no evidence whatsoever pointing to a break of decades old hardness assumptions like elliptic curve cryptography. 1/n

Today I call upon the blockchain industry to calmly begin planning for "bunker mode". My personal recommendation is to set in motion a controlled mass migration of assets to fresh addresses, i.e. addresses whose pubkeys remain hidden behind a hash.
Holders, starting with large and sophisticated ones, should consider moving the bulk of their funds to addresses that have never signed a transaction. And when they do sign one, they should also move remaining funds to a new address (possibly generated from the same seed phrase).
Don't rush. While I believe there is cause for action a rushed migration would do more harm than good. Don't panic either. Moving assets to protected addresses is a simple, preventative step which does not require new cryptography or new wallets.
IMO it is now reasonable to brace for the possibility that ECDSA breaks before qday, in the worst case in months not years. By "break" I mean fast private key recovery (e.g. in one week) on available hardware (e.g. a large GPU cluster).
Recent days have been humbling for human mathematical intuition. Long-held, unquestioned hypotheses have fallen. This includes the n log(n) bound for integer multiplication and the 3SUM conjecture. In hindsight, May's unexpected disproof of the Erdős unit distance conjecture was our warning shot.
Yesterday's OpenAI drop made it clear that mathematical superintelligence is upon us. They say there are weeks where decades happen. We are about to live through weeks where centuries of mathematical progress happen. Could our magic 64-byte ECDSA signatures be too good to be true? Was it just security through obscurity all this time?
Elliptic curves feel especially vulnerable to superintelligence. Curves carry rich structure, with room for fancy tricks like Schoof, Frobenius, pairings. (By contrast, hashes are designed to minimise algebraic structure.)
Separately, as Ewin Tang can attest, an efficient quantum algorithm sometimes foreshadows an efficient classical one. We should be open to the possibility of a classical counterpart to Shor that breaks elliptic curves and RSA at once.
Also noteworthy is the striking under-representation of cryptographic breakthroughs among the 722 mathematical results OpenAI published. I've witnessed first-hand the US government censoring academic quantum cryptanalysis results. Backroom interventionism is my base case.
I urge large, sophisticated actors to lead by example. Project11's "risq list" (bitcoin-risq-list.projecteleven[.]com) is a great tracker of exposed BTC pubkeys. Binance, Bitbank, Robinhood, Bitfinex, and Tether have an opportunity to harden their cold storage. Next month I'll address institutions in London in a live Q&A (forum.ethereuminstitutional[.]org/london-2026).
Again, please do not rush. Wallets holding under 50 BTC enjoy partial cover from "Satoshi's shield", i.e. his 20K exposed addresses that hold 50 BTC each. Load-bearing signers like oracles and L2 security councils should consider rotating ECDSA pubkeys with every signed message and/or multi-signing with a hash-based schemes like SPHINCS.
Exiting bunker mode safely will require post-AI cryptography. My inclination is to go all-in on hash-based cryptography and avoid structured mathematical assumptions entirely, whether from curves, lattices, or isogenies. A single battle-tested hash (e.g. from the SHA or BLAKE families) yields plausible post-AI security.
The Ethereum roadmap on strawmap[.]org fully embraces hash-based cryptography with end-to-end formal verification as a response to the quantum threat. Those timelines must now be revisited and accelerated in light of mathematical superintelligence. I'll be pushing for maximum defensive acceleration.
It's hilarious that even the curl-to-sh command for codex updates suffers from accumulated AI slop. I can't even copy it because it line wraps. Run a curl-to-sh inside an explicit sh which pipes to sh?? Some magic environment variable is required??

Zero-Knowledge Goof❄️ retweeted
At this point I'm more worried about nontrivial projects that *aren't* releasing a stream of security updates than those that are. Where are my BIOS updates? microcode updates?
Good: claude loves mutation testing now which is great.
Bad: A mutation test removed a guard which narrows processes to kill and killed very process on my machine.
Zero-Knowledge Goof❄️ retweeted

Threshold signatures compatible with BIP SHRINCS. Massive step forward, even if it requires a trusted dealer.

1/ You've probably heard of SHRIMPS. But have you heard of PRAWNS? 🦐
After a months-long research effort, @danboneh, @benediktbuenz, Justin, Yavor, and @nazirkamilla are excited to announce a novel thresholdization scheme for one-time hash-based signatures!
Incredible post. This bitcoiner decided to post outside of bitcoin twitter and WoW nerds were not prepared for it. The replies gave me intense pleasure.

#Blizzard, hear me out!
Here’s a proposal for #WoWForever to solve WoW’s gold inflation problem permanently!
Almost every version of WoW eventually runs into the same problem: the gold supply keeps growing without any hard monetary limit.
Over time, this inevitably creates inflation. Gold loses purchasing power, prices rise, and new or returning players enter an economy where veteran players have accumulated wealth for years.
There is a simpler solution:
Give every server a hard, fixed gold supply.
For example: 100 million gold total. Forever.
Think of it as the server’s monetary base.
Gold dropped by mobs would no longer be newly created. Instead, mobs would distribute gold from a global server pool.
The amount of gold mobs drop would dynamically depend on how much gold is currently available in that pool:
• Lots of gold in the pool → mobs drop more
• Little gold in the pool → mobs drop less
Gold spent by players flows back into this pool and can then be redistributed through gameplay.
NPC purchases such as skills, professions, repairs, mounts, etc. would return 100% of the spent gold to the server pool.
Trading systems like the Auction House could also recycle part of the circulating gold back into the pool through transaction fees.
This creates permanent circulation instead of permanent monetary expansion.
NPC prices should also be dynamic.
If a large percentage of the total gold supply is being held by players and very little gold is actively circulating, prices for essential services like skills and professions should decrease.
That prevents new players from being priced out simply because veteran players are sitting on large gold reserves.
The game economy would continuously adapt to the purchasing power and availability of gold.
Over the very long term, the general price level might gradually decline, potentially resulting in mild persistent deflation.
But that wouldn’t necessarily be a problem if the game world itself dynamically adjusts to the purchasing power of gold.
One possible consequence of persistent deflation is that players may initially hoard gold.
Imagine someone accumulates a large amount of gold, stops playing for three years, and then returns. Because prices have fallen in the meantime, their old savings could suddenly have significantly more purchasing power.
But this effect is naturally self-correcting.
The moment that player starts using that increased purchasing power, the saved gold begins circulating again.
They get the benefit of having saved, as they should, but once they spend it, that purchasing power is transferred to other players and gradually redistributed throughout the economy.
In other words: hoarding can temporarily concentrate purchasing power, but spending automatically starts reversing that concentration.
The important part is:
Gold would finally become truly scarce.
No endless monetary expansion.
No inevitable long-term inflation.
No need for increasingly absurd gold sinks every expansion.
Just a closed monetary system where the same gold continuously circulates between players, NPCs, and the game world.
For a version of WoW designed to exist forever, its currency should be designed to exist forever too.
@Warcraft @Blizzard_Ent @Warcraft_DE

Zero-Knowledge Goof❄️ retweeted
rbitcoin: Bitcoin Full Node With Zero Human Code | reardencode SLP775
@reardencode of @rbitcoin_org walks through rbitcoin — a Rust Bitcoin full node where all lines of code were written using AI.
Timestamps
00:00 — Intro: Brandon Black & rbitcoin
00:34 — Why Build rbitcoin
03:46 — Alt Clients Mini-Series
04:39 — Consensus Divergence Risk
05:53 — satd vs rbitcoin Paths
06:51 — Automation Makes Diversity Possible
08:29 — Build-Time Differential Testing
09:20 — Why Consensus Bugs Matter
10:55 — Lessons from btcd Divergences
13:35 — Target User: Wallet Backends
15:29 — Miners Leave the Non-Goal List
16:47 — Kill the dbcache Model
20:50 — Electrum In-Process
22:23 — Silent Payments & Tor
23:01 — BIP324 v2-Only P2P
23:46 — AI-Coded: Zero Human Lines
25:04 — Grok Plus Multi-Model Review
27:01 — DoS Rules & LibreRelay
28:34 — Upgrade Hooks
29:34 — Archive-Only, No 'UTXO Set'
31:50 — AI as the New Compiler
33:52 — Context Limits & Dependencies
38:06 — rust-bitcoin Relationship
39:08 — Wallet Infra Opportunity
40:00 — Still 10% a Joke
41:35 — Future of Client Diversity
44:50 — Outro: rbitcoin.org
Zero-Knowledge Goof❄️ retweeted

***NEW Martyr Made Podcast***
Enemy: The Germans’ War, pt. 3 - The Fighting Man
Millions of German soldiers return home to find the Bolshevik plague pouring out of Russia into Europe. They were only too happy to have someone else to fight. (Link below)

Zero-Knowledge Goof❄️ retweeted

Home invasions are the fastest growing attack type, and one country accounts for most of them. @LLFOURN analyses the situation:
Zero-Knowledge Goof❄️ retweeted
Adaptive attacks against FROST when number of signers and corruptions is large. BIP 445 (FROST) not affected because it requires fewer than 128 signers. This requirement in BIP 445 was added by @real_or_random exactly because there was uncertainty about the hardness of LDVR.
github.com/siv2r/bips/blob/8…


New paper with @AlexRdgzG: We give polynomial-time (!) adaptive attacks against a number of threshold Schnorr signatures.
At the core are the first polynomial-time attacks on LDVR, a problem whose solution yields adaptive attacks on several practical schemes.
Zero-Knowledge Goof❄️ retweeted

❄️COLDCARD WHITE HAT MOVES FUNDS TO TRUST 🏳️
52.37 BTC comprised of coins from Wave 2, Footprints AA, AU, AX consolidated into a fresh address with an OP_RETURN "claim:cryptorecoverytrust dot com" in block 967,948
these white hatted funds represent 2.8% of the coldcard exploit

Zero-Knowledge Goof❄️ retweeted
With 360 Bitcoin wrench attacks cataloged, it's time to take the archive to the next level. Over the weekend I clanked out this interactive dashboard; feedback is welcome!
jlopp.github.io/physical-bit…

Zero-Knowledge Goof❄️ retweeted

“Laws preventing people from speaking are regrettable. They never produce good results. It seems to me that it is always in the name of a greater humanity, of preventing people from being made victims, that measures of this kind are taken. But such taboos are directly contrary to the nature of [scapegoat] Revelation.”
— René Girard

