The global leader in research-fueled cybersecurity services
Ioactive
Joined March 2009
- Tweets9.9K
- Following2.4K
- Followers11K
- Likes1.1K



🚨 PHP releases emergency patches for two critical RCE vulnerabilities (PHP2Shell), both rated CVSS 9.2.
Even secure application code may be exposed. Prioritize patching.
More via @TheHackersNews 👇
thehackernews.com/2026/10/ph…

Next Thursday at hack::soho: Dinis Cruz on “The ultimate insider.” AI agents as insider threat, infrastructure built for static code, and risk management stuck in spreadsheets. Live demos included.
📍 London | 29 Oct | 6–9 PM | Livestream ~7 PM
eventbrite.com/e/hacksoho-oc…

A practical framework for building a cyber risk management strategy that aligns security investments with business impact, OT, AI, and third-party risk. ioactive.com/cyber-risk-mana…

Check out our upcoming events! info.ioactive.com/acton/fs/b…
🌟 Oct. 24 | BSides Peoria - bsidespeoria.com/
🌟 Oct. 28 | CYSAT Madrid - cysat.eu/cysat-madrid
🌟 Oct 29 – 30 | LASCON - lascon.org/
🌟 Oct. 29 | hack::soho - eventbrite.com/e/hacksoho-oc…


Signal messenger security research: IOActive tested Signal Desktop’s Windows screen-capture protection and showed how local code execution can undermine a trusted security control. ioactive.com/signal-messenge…

Security execs: join IOActive leadership for an evening of candid peer discussion this November.
🗽 NYC, Nov 4
🌲 Seattle/Bellevue, Nov 5
🌰 Columbus, Nov 5
🇬🇧 London, Nov 12 (breakfast)
Seats are limited. Pick your city: info.ioactive.com/acton/fs/b…

CISA revised the July water sector campaign from ~30 systems to 100+. The campaign didn’t grow. The observer’s view did. What that says about the OT detection gap. ioactive.com/from-30-systems…

Check out our upcoming events! ioactive.com/events/
🌟 10/12 – 15 | 2026 OCP Global Summit - opencompute.org/events/ocp-s…
🌟 10/24 | BSides Peoria - bsidespeoria.com/
🌟 10/28 | CYSAT Madrid - cysat.eu/cysat-madrid


Secure product development lifecycle requirements protect connected products from design through support. ioactive.com/secure-product-…

October is #CybersecurityAwarenessMonth. Four habits, fewer breaches:
Strong passwords + a password manager
MFA on everything
Spot and report phishing
Update your software
Resources to stay protected: ioactive.com

Check out our upcoming events! info.ioactive.com/acton/fs/b…
🌟 10/6 - 9 | Auto-ISAC Cybersecurity Summit - automotiveisac.com/2026-annu…
🌟 10/12 – 15 | OCP Global Summit - opencompute.org/events/ocp-s…
🌟 10/28 | CYSAT Madrid - cysat.eu/cysat-madrid


Cyber risk management strategies start with business impact. Learn six pillars to prioritize security investments, validate defenses, and strengthen operational resilience. ioactive.com/cyber-risk-mana…
hack::soho is back 🎤 Dinis Cruz on "The Ultimate Insider": why AI agents are the insider threat that never scaled before, and how to contain them. Live demos, all open source.
📅 Thu 29 Oct, 6–9 PM
📍 IOActive London
Register 👉 eventbrite.com/e/hacksoho-oc…
#hacksoho #AIsecurity

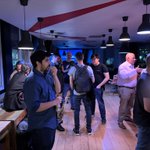
Thanks to everyone who joined Megan Holliday's session at @cornconcyber Conference yesterday! 🌽 Great questions, great conversations, and a packed room. A few highlights below.
Want to see how IOA helps orgs stay ahead of real-world threats? 👉 ioactive.com


New FBI/CISA guidance raises a question every operator should be able to answer: if your ICS integrator were compromised tomorrow, could you still run your plant? cisa.gov/resources-tools/res… #OTSecurity

Asking an LLM to "find all the vulnerabilities" gets you noise. Asking it one testable question anchored in a threat model gets you real bugs.
Carlos Gomez explains the workflow behind two HIGH-severity Angular CVEs: ioactive.com/llm-assisted-vu…
#VulnerabilityResearch #AISecurity

IOActive is proud to sponsor @cornconcyber Conference 2026, kicking off tomorrow, October 1! Don't miss Megan Holliday on October 2 for a practical introduction to penetration testing AWS environments. corncon.net/

Is your AI ready for an adversary? IOActive breaks down the most critical AI red teaming techniques organizations need to know in 2026. ioactive.com/ai-red-teaming-…

That's a wrap on September's #hacksoho! Thanks to everyone who joined us in London and helped this community keep growing. Huge thanks to Nick Dunn for a great talk on data-bouncing exfiltration.


Internet-exposed OT. Different threat actors. The same fundamental risk.
IOActive examines the NCSC’s latest OT Alert alongside AA26-097A — without conflating attribution — and what CNI operators should prioritise next. ioactive.com/one-exposure-ma…
#OTSecurity #ICS #IOActive
