

Scam survivor turned 2D investigator, Advisor @paradigm
Joined February 2015
- Tweets23.8K
- Following2K
- Followers1.1M
- Likes246K



Pinned Tweet
1/ An investigation into how Greavys (Malone Iam), Wiz (Veer Chetal), and Box (Jeandiel Serrano) stole $243M from a single person last month in a highly sophisticated social engineering attack and my efforts which have helped lead to multiple arrests and millions frozen.


Indian law enforcement froze $3M from an innocent Chinese investor after mistaking a crypto bridge for a pig butchering scam. Now an Indian court has ordered Gate to hand his funds to a person they never belonged to.
My analysis of how Indian LE traced through an unlabeled service and wrongly froze @xxxkeym's Gate account:
The case stems from a pig butchering victim who allegedly lost $1.7M of BTC, USDT, DOGE & SOL in May 2025.
Andhra Pradesh CID registered it as Cr. No. 10/2025 and filed a charge sheet in March 2026.
In July 2025, xxxkeym had Gate deposit address 17mpajZ6Nq3dG3T6wUhaXxYF4Qy9HJnYx5 frozen after depositing 15 BTC from 3NcBhqK in the following transaction:
885f3afab562251b222363cf12095e864ddb94636674b01f0cdb05997e5a54a0
This is one transaction Indian LE cites in its notice. 3NcBhqK was funded by xxxkeym's own OKX & Binance withdrawals in Jan 2023 and the coins sat dormant for years until the Gate deposit.
Indian LE never froze his OKX or Binance accounts, the actual source of the 15 BTC, which tells you how flawed their justification is.
Gate froze his entire account, which held roughly $3M at the time and about $1.5M today.
The Indian court order hands all of it to the complainant.
Gate deposit address 17mpajZ also received two deposits for 15 BTC total in 2025 from bc1pkkwqyxn3rm608ryuqg9hyqna0syq4jx5pxkr7pzg8n3usx6tyqfst5u966, which is also controlled by xxxkeym.
Shortly before the deposits to Gate, bc1pkkw was funded in three transactions by bc1quzwkggdf6ly06mrrnnled0qdr57w770k45n5n7 & bc1qtu66zfqxj6pam6e0zunwnggh87f5pjr7vdr5cd.
bc1quzw & bc1qtu66z were reported as alibarbit[.]bit, the same scam named in Indian LE's press release.
That was a mistake. Both belong to the Merlin Chain bridge, which is unlabeled in most compliance tools.
xxxkeym is simply a normal Merlin user trading tokens on the L2. This wrong label is the only place the scam touches his transaction history.
Below is the blockchain data showing each Merlin withdrawal by xxxkeym matched to a BTC payout from those addresses, plus screenshots of the bridge activity.
xxxkeym bridged 50 BTC into Merlin on March 28, 2024, over a year before the alleged May 2025 theft.
His three withdrawals came out of that balance. I found zero onchain connections between xxxkeym and the theft.
Separately on July 15, 2025 xxxkeym had a 7 BTC private key compromise theft which was reported to local police and also SlowMist was engaged. His stolen funds flowed to Wasabi.
This is embarrassing incompetence by Indian LE, who seem incapable of reviewing basic blockchain data.
Indian LE, the prosecutor and the judge all signed off on this, Gate froze the account, and LE did a full press release about it recently, while the real victim here (the Gate user) hasn't had access to his funds for nearly 16 months.
My hot take is VASPs need to challenge weak jurisdictions like India, Canada, etc due to repeated negligence in criminal cases.
Merlin source transactions from xxxkeym
10.1368 BTC - March 25, 2025
0x975081c2a62355019561c3ec0d01c72bf0dadf7121d46764bbb13ac0013a9a06
4.9071 BTC - May 6, 2025
0xa30f7b770e2e8e2e2d0fc0d390aa800e7f880e8e129d1b705dbc4167fc878769
9.9796 BTC - June 17, 2025
0x147429d324520c9ebee8015b0214dbd7bdce97ee37ad25e11819f4b04aecc049
Bitcoin destination transactions to xxxkeym
10.1367 BTC - March 28, 2025
55ab5373c2daa69b1728e6551b59f9dc661d1d78786face798d5251ccbe4685a
4.907 BTC - May 9, 2025
b2222fe38856e65420f15051a4cc419a92868803dec69a218f007948972ea367
9.9795 BTC - June 19, 2025
094f01388638523fb29aac0a0d4f70adf6949fede0847a45cef2c3f930692c73
Merlin Chain bridge
bc1quzwkggdf6ly06mrrnnled0qdr57w770k45n5n7
bc1qtu66zfqxj6pam6e0zunwnggh87f5pjr7vdr5cd
Gate deposit address - xxxkeym
17mpajZ6Nq3dG3T6wUhaXxYF4Qy9HJnYx5
Other addresses - xxxkeym
3NcBhqKnyo8dfzqfG1p5rbaKJFV8yLnx3u
bc1pkkwqyxn3rm608ryuqg9hyqna0syq4jx5pxkr7pzg8n3usx6tyqfst5u966
0x59fd8E3aEca4FAbb53ef6078D2319Dc174fb66a6
July 15, 2025 BTC theft addresses
bc1qjmf2e4fc2r97rq762055ag3g9uhypavta0payq
bc1q80gq7ctfsm6p9h9jh2k45da87jy6s7a87pj3h0
March 28, 2024 50 M-BTC destination transaction to xxxkeym
0xf1ee67ba1d3f97fb2d4776fa8ffc90f0b7ba7d116de3bf510a2c6aeae7d80def


BREAKING: Arbitrum Security Council has executed a transaction to freeze ~$30.5M from the Binance Exploit.
Thanks to all other signers involved.
Exploiter address
0x3E2bf1ac6bf0934BBba6456C341c2EcbCED632d5
Trsanction hash: 0xb69c81774f507d46ce776aeaed8b4d31df96dd66ce6fd05073481011835355d6

Update: Stolen funds from the $6.3B Binance exploit and $388M Bitget exploit were commingled at the same address 45 minutes ago, after arriving via THORChain.
This indicates the same actor is likely behind both incidents.
The Bitget exploit was attributed to DPRK-linked TraiderTraitor, which had overlap with other previous exploits such as Kelp DAO.
Commingling address:
0x15104a9ce0f08a8f0075a0869ae80e795fe0feb7
Bitget exploit context: xitter.cf/zachxbt/status/2104528…


BREAKING: Chinese illicit actors laundering funds from the $387M Bitget exploit on behalf of the alleged DPRK attackers are openly asking for support with orders in public Discord servers and Telegram channels of services they use.
Notably, Alias 4 (below) was also seen laundering funds from the Kelp DAO $292M exploit earlier this year.
I've observed the same pattern after multiple TraderTraitor attributed exploits, and I've closely tracked these groups. I plan to share more of my data on them in coming weeks.
Currently, funds are being chain-hopped via bridges and being deposited into mixing services such as Wasabi.
Alias 1 - Cc
Discord: cc02006
Discord ID: 1351486674386948148
Txn: F08657EFAEAE7B58217CD17A22BF4779582E5D080C2E92E173BC239A5D828363
Alias 2 - jack
Discord: jack_34808
Discord ID: 1553705721768714377
Txn: 68583D313A0CCC99F2702D61D05A242A69C86CAE09ED252B65F34B677C377F69
Alias 3 - Melon
Discord: under0346
Discord ID: 1394240539108573215
Txn 1: ABE2AEF8B10057E60F8259CA2CA2CD5D71D38D254960FEEE89CB3C95A964873F
Txn 2: 7BE290865901DEB1680A6D692A11392D1FDDACA0D31C48F26DCB249F2444BD6B
Alias 4 - lolo / Marin
TG: pvpcz
TGID: 6223514198
Discord: losern
Discord ID: 1024415186527985704
Txn: 8E935C19D00F40639B78BF1FD094FE48C92118F3E586AB52DF93851080CCCE15
Alias 5 - HELP ME
Discord: helpme031897
Discord ID: 1554035533817188384
Txn: 7C58CAD760EBBED54F2CA4D2146D056910B7B6688B4F524396DC8807353C2379


1/ How I infiltrated a Chinese organized crime syndicate that has laundered $1B+ across multiple exploits for Lazarus Group.
Posing as a client, I gathered intel that helped action freezes for the Feb 2025 Bybit exploit and attribute illicit activity onchain.

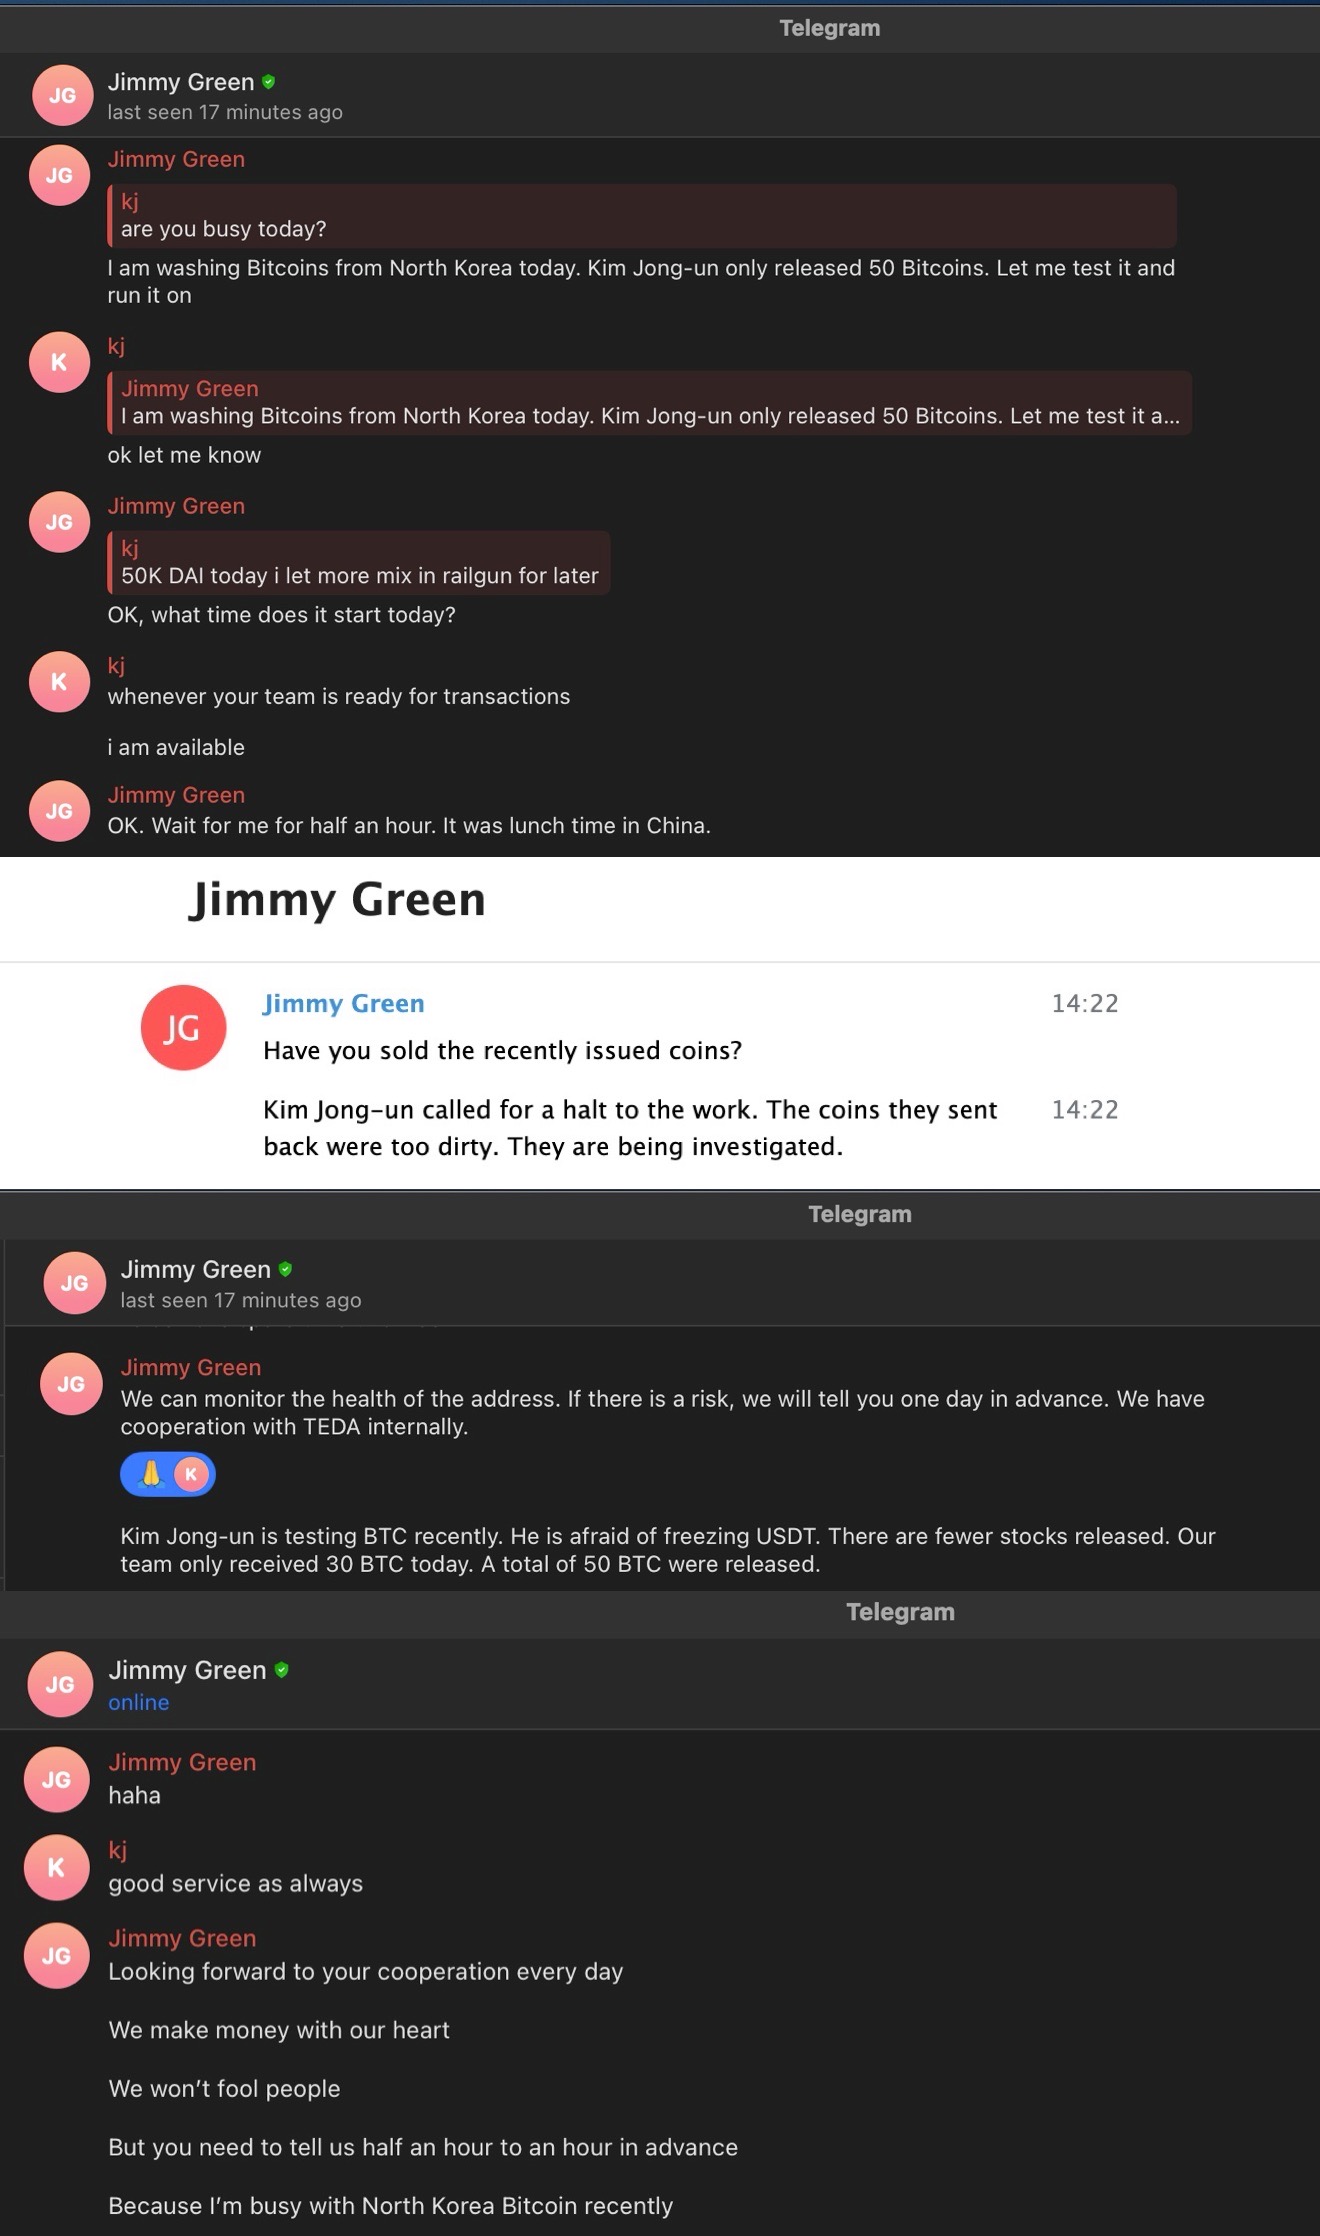
11/ Throughout our conversations, Jimmy and I had a lot of small talk in between discussing laundering for DPRK.
He talked about playing mahjong, hunting wild rabbits, food, his fat reducing meal, family life, and vacations at Disney.
(His awkward grammar can be explained by the use of a translator)


12/ I hope to continue receiving grants from foundations and donations from individuals, as it enables me to take on higher risk for unique cases that others may not consider viable.
For this case, I fronted $349.7K and lost 5% on each order, with no guarantee Jimmy wouldn't disappear with the funds, and an unknown amount of personal risk from dealing with the syndicate.
Since 2022, I have helped action $75M+ in freezes related to DPRK incidents.
My findings were immediately shared with trusted investigators within the private sector and law enforcement assigned to the case.
Due to sensitivity around the investigation, I was unable to publish sooner.
That is one of the frustrations I have with my work. I am not always able to share findings as quickly as I'd like, and I am currently sitting on significant findings from other cases.
If this case resonates with you and you're in a position to support it, feel free to reach out.

BREAKING: Chinese illicit actors laundering funds from the $387M Bitget exploit on behalf of the alleged DPRK attackers are openly asking for support with orders in public Discord servers and Telegram channels of services they use.
Notably, Alias 4 (below) was also seen laundering funds from the Kelp DAO $292M exploit earlier this year.
I've observed the same pattern after multiple TraderTraitor attributed exploits, and I've closely tracked these groups. I plan to share more of my data on them in coming weeks.
Currently, funds are being chain-hopped via bridges and being deposited into mixing services such as Wasabi.
Alias 1 - Cc
Discord: cc02006
Discord ID: 1351486674386948148
Txn: F08657EFAEAE7B58217CD17A22BF4779582E5D080C2E92E173BC239A5D828363
Alias 2 - jack
Discord: jack_34808
Discord ID: 1553705721768714377
Txn: 68583D313A0CCC99F2702D61D05A242A69C86CAE09ED252B65F34B677C377F69
Alias 3 - Melon
Discord: under0346
Discord ID: 1394240539108573215
Txn 1: ABE2AEF8B10057E60F8259CA2CA2CD5D71D38D254960FEEE89CB3C95A964873F
Txn 2: 7BE290865901DEB1680A6D692A11392D1FDDACA0D31C48F26DCB249F2444BD6B
Alias 4 - lolo / Marin
TG: pvpcz
TGID: 6223514198
Discord: losern
Discord ID: 1024415186527985704
Txn: 8E935C19D00F40639B78BF1FD094FE48C92118F3E586AB52DF93851080CCCE15
Alias 5 - HELP ME
Discord: helpme031897
Discord ID: 1554035533817188384
Txn: 7C58CAD760EBBED54F2CA4D2146D056910B7B6688B4F524396DC8807353C2379
1/ Meet M1llionz (RichMilly666), a French cybercriminal allegedly laundering assets from two violent home invasion robberies in France in April 2026 that netted $667K total, with a history of openly posting about bank and retail fraud on social media.
My work has led to a $93K Tether freeze directly tied to these attacks so far.


11/ Home invasion robberies remain one of the cases I prioritize most and if you are a victim do not hesitate to reach out for help.
I have frozen multiple seven figures across US & EU incidents and identified several perpetrators for cases which I hope to be able to share details about in the near future.
Unfortunately, due to the sensitive nature of these cases I can't always publicize them as quickly as I'd like.
M1llionz has gone quiet on TikTok and Telegram in recent weeks and set his TikTok posts to private. I've since identified two further attacks within 2 hops of his OTC addresses.
In my experience, French law enforcement cares about helping victims and solving these cases, though inefficient laws can hinder outcomes.
