

Uptycs is the first unified #CNAPP & #XDR Solution. Because attackers don't think in silos & neither should you. #Cybersecurity #CloudSecurity #ThreatResearch
Waltham, MA
Joined September 2016
- Tweets6K
- Following1.2K
- Followers1.5K
- Likes5.7K




Finding a vulnerability is only the first step.
Uptycs supports reporting, automated ticketing, JIRA, and CI/CD guardrails to move findings toward remediation.
Move vulnerability findings into action.
bit.ly/4ymICsy #VulnerabilityManagement #CloudSecurity

Scaling Osquery takes more than queries.
Plan the problem you want to solve, deployment, configuration, data storage, and how the telemetry will be analyzed.
Build the right foundation for Osquery.
bit.ly/4yx607G #Osquery #EndpointSecurity

More signals should not mean more manual work.
Uptycs XDR correlates related signals into higher-confidence incidents, and Juno helps investigate the evidence.
Turn scattered signals into actionable incidents.
bit.ly/4yAqQCX #XDR #SecurityOperations

Cloud security has a language of its own.
From CNAPP and CWPP to AI-native investigation, telemetry, and compliance, Uptycs brings key concepts together in one place.
Keep modern security terms within reach.
hubs.ly/Q04y0K3Q0 #Cybersecurity #CloudSecurity

Feature count is a weak way to compare CNAPPs.
Ask whether the platform connects posture, runtime, attack paths, and build provenance so teams can trace risk across the lifecycle.
Evaluate CNAPP by connected context.
hubs.ly/Q04y0K5c0 #CNAPP #CloudSecurity

Sensitive data changes how cloud risk should be prioritized.
Uptycs #DSPM connects data sensitivity with vulnerabilities, exposure, and identity context to focus on high-value assets.
Prioritize risk with data context.
hubs.ly/Q04y0JYj0 #CloudSecurity

Juno builds an ontology from native security data before an investigation begins, mapping tables, entities, and relationships so it can reason with environmental context.
See how Juno builds context before it reasons.
hubs.ly/Q04xYfGN0
#JunoAI #VerifiableAI

#CSPM should answer more than “what is misconfigured?”
A practical approach should continuously identify configuration gaps, map them to security and compliance requirements, and support remediation.
Turn posture findings into action.
hubs.ly/Q04xCSR80 #CloudSecurity

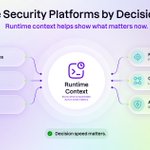
Finding more vulnerabilities does not help if teams cannot decide what matters now.
Runtime context helps show what is exploitable and what needs action first.
Evaluate security platforms by decision speed.
hubs.ly/Q04xCSRt0 #RuntimeSecurity #SecurityAI

A security AI should show more than its answer.
Juno runs multi-step investigations, follows the evidence, and shows the queries, raw data, and reasoning behind its findings.
See how Juno makes investigations verifiable.
hubs.ly/Q04yrdTp0 #JunoAI #VerifiableAI

Cloud posture can change long after the initial review.
Uptycs CSPM continuously monitors changes and adds context from vulnerabilities, identities, runtime activity, and critical assets.
Keep your cloud posture current.
hubs.ly/Q04xCTFT0 #CSPM #CloudSecurity

AIX security should not end at the firewall.
Look for EDR that adds runtime visibility, behavior-based detection, file integrity monitoring, threat hunting, and response.
Build AIX security around continuous verification.
hubs.ly/Q04xCTQv0 #AIX #EDR

#CNAPP should do more than combine security capabilities.
The value comes from connecting cloud, workload, Kubernetes, runtime, and code context so teams can understand which risks matter most.
Evaluate how your cloud security connects.
hubs.ly/Q04xCTQf0 #CloudSecurity

More data does not automatically make an AI investigation better.
Juno connects more sources, maps relationships, and surfaces task summaries and inline evidence so analysts can follow how findings were reached.
See how Juno works.
hubs.ly/Q04xCTYr0 #JunoAI #VerifiableAI

53% of business-critical apps are housed in multicloud environments, while half are most often housed on-premises.
That mix raises the bar for consistent security visibility.
See what the research says: hubs.ly/Q04xCV2x0
#HybridCloud #CloudSecurity

A vulnerability shows what could be exploited. Runtime telemetry shows what is happening now.
Uptycs surfaces suspicious process and network activity across live workloads.
See what is happening at runtime.
hubs.ly/Q04wRdkb0 #RuntimeSecurity #CloudSecurity

Protecting cloud workloads takes more than vulnerability scans.
A practical CWPP strategy needs visibility, runtime detection, behavioral monitoring, and response.
Evaluate workload protection with the right questions.
bit.ly/4ibPdBC #CWPP #CloudSecurity

Security AI is only as verifiable as the architecture beneath it.
Siloed data forces AI to reconstruct context. A unified model lets Juno query evidence and show its work.
Evaluate the architecture behind security AI.
bit.ly/3UDUGra #SecurityAI #VerifiableAI

Adding another connector gives AI more data. It does not automatically give it more context.
Juno uses ontology to connect evidence across sources with bounded, auditable queries.
Connect more sources without losing context.
bit.ly/4h3acp5 #JunoAI #VerifiableAI

Application risk does not stop at the code repository.
Uptycs connects code, CI/CD, container images, provenance, and runtime telemetry across the lifecycle.
Connect application risk from code to runtime.
bit.ly/4qQ44Uv #ASPM #ApplicationSecurity
