Bullshit fearmongering. 0days have always been abundant. These bugs are now being found and patched at an amazing rate, instead of being used by adversarial groups. Be happy, because most organisations have no clue how to run their infrastructure or detect anomalies

This is the most serious 48 hours in cybersecurity history.
"Black October" they're calling it
It seems every *hour* there's a new incident, that in a typical year, would be one of the biggest incidents of the *entire year*
SUMMARY OF THE LAST 48 HOURS:
YEAR-LEVEL INCIDENTS (In a typical year, these would be among the biggest incidents of the year):
1. PHP2Shell: a hole in the software behind ~70% of websites. Governments took sites offline.
2. eMudhra: the master keys that prove websites are real were cracked. One was the number 4.
3. California: data on every public school student since 2023 stolen, including disability status
4. Railway: hackers stole customers' secret keys from a hosting platform used by millions of developers
5. Zeabur: 321,810 accounts breached. The company is shutting down.
6. LiteLLM: an AI tool downloaded 3.4 million times a day was poisoned with a password stealer
7. GitLab: a 10-out-of-10 severity hole in every version since 2014
8. Cairn: criminals used an AI hacking tool to break into 100+ companies
9. Ahold Delhaize: hackers knocked the owner of Food Lion and Stop & Shop offline
10. Onamae: malware planted on up to 26,739 customer servers in Japan
MONTH-LEVEL INCIDENTS (In a typical month, these would be among the biggest incidents):
11. Signal: a bug could leave your mic and camera on after you hang up
12. NGINX: 3 critical holes in software running ~1/3 of websites
13. HTTP/3: a single connection can crash 7 of the 10 web server types tested
14. Plex: hackers breaking into home media servers
15. SafePay ransomware: FBI warns it has hit 600+ critical infrastructure organizations
16. Palo Alto: ransomware gangs breaking in through company firewalls
17. Bullhorn: platform used by 10,000+ companies knocked offline
18. Medi-Cal: 970,000 patients' data stolen
19. WordPress: hackers stole a plugin maker's keys and used them to plant backdoors on websites
20. AOMEI: backup software's update server handed out a backdoor
21. Meta Muse: Meta's AI agent exposed users' personal and business secrets
22. Tor: 333 relays hijacked to steal logins
23. TiDB Cloud: database company's cloud breached
Also serious:
24. State Bank of India: India's biggest bank confirms a data breach
25. OVHcloud: hackers slipped a password stealer into a cloud company's official tool
26. Siemens: a software hole being used to spread malware
27. North Korea: state hackers launch a new attack campaign on South Korea


watching the younglings panic over a PHP RCE
boy, you haven't lived until an RCE involves your VPN, MDM or IdP

now we talking xitter.cf/TheHackersNews/status/…


🚨 CRITICAL: GitLab flaw (CVSS 10.0) affects 12 years of releases.
CVE-2026-110264 could allow unauthenticated remote code execution on self-managed servers.
Read - thehackernews.com/2026/10/cr…


“Tesla stunt is fake”. Sure, the company that belly flops 280 metrics tons and catches it midair will struggle with a car


UPDATE: I can confirm that the Ledger supply chain is compromised in Europe as well. @Ledger should initiate an immediate product recall to protect users.
I just purchased a second device from a different Mediamarkt location today, recorded the unboxing process, and discovered spyware once again (video linked in the second tweet).
The device was compromised in the exact same manner, featuring identical modifications (such as additional cables and an LTE module). This indicates its a widespread issue rather than an isolated incident, potentially affecting Ledger inventory across MediaMarkt and Saturn stores throughout Europe (comprising over 1,000 stores across 11 countries).
My initial hypothesis was that these devices were returns that looked unopened to the employees and were just sold again as new however, a MediaMarkt employee confirmed that the device I purchased was not a return, and that returned Ledgers are sent directly back to the manufacturer rather than resold.
Store records show the inventory originated from Aqipa GmbH. While Ledger's CTO was unsure if Aqipa serves as the direct distributor between Ledger and MediaMarkt, it appears to be the case. Given that Aqipa distributes across Europe, any physical retail store receiving stock through them may be at risk.
I sent the first ledger to mark and the second one is going to ledger now, so that they can analyse it.
If you purchased a ledger from anyone other than the official ledger store, make sure to check your device!!


I’m ready to get hurt again


For decades, researchers have sought materials that sort electrons by spin while their magnetism cancels.
In 3 days, 90+ Opus 5.5 agents helped us uncover two room-temperature magnetic semiconductor candidates in simulations: YBaMnFeO₅ and KV[Cr(CN)₆].
KV[Cr(CN)₆] was synthesized back in 1999. Its predicted ability to sort electrons by spin appears to have been hiding in plain sight for 27 years.


A lot of speculation on if KVM bugs have gotten cheaper, and why id do it for 50k instead of a milly. I wasn't born yesterday. I know I couldve sold it for waayy more. I didnt want to. I did it for the love of the game. I wanted to know if I could do it, and now we know i can. Maybe I am a big dreamer?


Merkel hätte das nie toleriert. Danke für nichts, Merz.

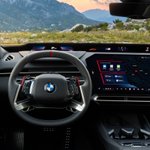
BMW’s Neue Klasse era could get very interesting.
Imagine an i3 Touring built on the new generation platform.
A practical electric wagon, clean proportions, and that Neue Klasse design language without the usual SUV shape.
This is only a rendering for now, but honestly, I’d take this over another electric SUV. 👀
Would you want BMW to build it?

Everyone who was involved or signed off on it needs to be shot

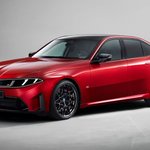
The Base 2027 BMW 3 Series Is Surprisingly Good-Looking.
Read more: bit.ly/4xXNnZk

ALT The Base 2027 BMW 3 Series Is Surprisingly Good-Looking


It’s 2026, and the media here is trying to shame Xhaka for faking his COVID vaccine certificate in ’22, but everyone's struggling to find the scandal