

A blockchain security and data analytics company (telegram: https://xitter.cf/t.co/x72dANZur3)
Joined January 2018
- Tweets1.6K
- Following603
- Followers80.6K
- Likes3.4K




Pinned Tweet
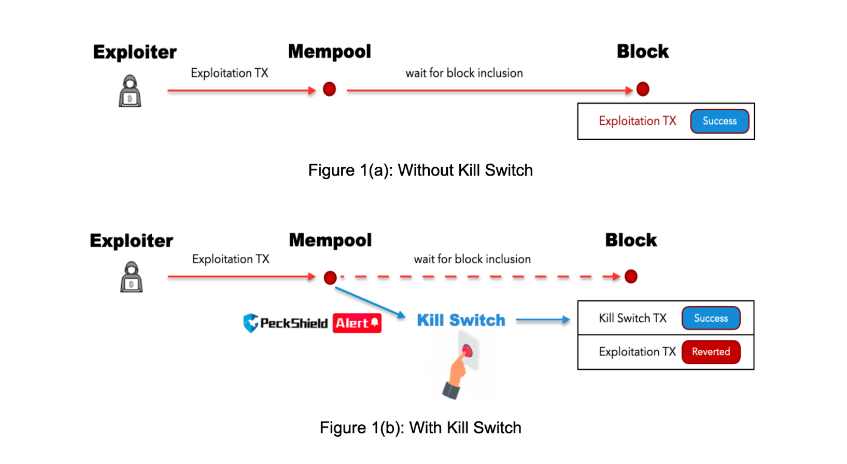
1/ We are thrilled to announce a self-service SaaS platform-#KillSwitch, which aims to detect exploitation TXs before their block inclusion and take contingency measures to block the attack or prevent assets from being stolen. It is in-essence a frontrunning-based DeFi protection
PeckShield Inc. retweeted


The funds from the $3.8M NEAR Intents hack were sent back in full.
We are stopping the investigation.
Please use bug bounties instead of disrupting the services.
It seems @bitget hot wallet potentially hacked w/ >$178m @BitgetSupport etherscan.io/address/0x770b1…

PeckShield Inc. retweeted

#PeckShieldAlert @TectonicFi was exploited for ~$74M total on the @CronosNetwork. In response, Cronos paused the entire chain.
The attacker managed to bridge out only ~$6M to #Ethereum before the pause, leaving the remaining ~$60M stuck on Cronos.
The attacker's funds are now sitting across the following addresses:
~$60M on Cronos: 0x7d4e....4f2dc
~$6M bridged to Ethereum: 0xc404...72dd
~$8M on Cronos: 0x215a...d3fc


Looks like the @summerfinance_ LazyVault_LowerRisk_USDC vault has a share price accounting issue that may be manipulated by donating to SiloManagedVault

#PeckShieldAlert @summerfinance_ has been exploited for $6M ethereum:0x6b175474e89094c44da98b954eedeac495271d0f

PeckShield Inc. retweeted
#PeckShieldAlert @summerfinance_ has been exploited for $6M ethereum:0x6b175474e89094c44da98b954eedeac495271d0f
PeckShield Inc. retweeted
#PeckShieldAlert Specter reported that @Raydium has been drained of $1.3M worth of crypto
The attacker was initially funded from #KuCoin, bridged the stolen funds from #Solana to ETH, and deposited 810 $ETH to #TornadoCash and 7 ETH to #FixedFloat.

PeckShield Inc. retweeted
#PeckShieldAlert The @gravity_bridge has been drained of ~$5.4M, including $4.3M $USDC, 274 $ETH (~$553K), $434K $USDT & 14.164 $PAYG ($64K)
The hacker has laundered a portion of the stolen assets through #ChangeNow & #Binance, and is still holding 2.102K $ETH (~$4.23M).


Hi @mapprotocol, you may want to take a look: huge amount 1,000,000,000,000,000 of $MAP0 were minted:
etherscan.io/tx/0x31e56b4737…

Hi @veruscoin It seems abnormal assets outflow (~$11.4m) from Verus-Ethereum Bridge: etherscan.io/address/0x71518…
The funds are currently parked in the following address: etherscan.io/address/0x65cb8…

PeckShield Inc. retweeted
#PeckShieldAlert @THORChain has been exploited for ~$10M worth of crypto, including 36.75 $BTC ($3M) and ~$7M worth of assets from #BNBChain, #Ethereum, and #Base.
The stolen funds mainly sit in:
bc1ql4u94klk265lnfur2ujk9p6uh52f2a8jhf6f37
0xd477b69551f49C0519F9B18c55030676138890Bd

After liquidating the KelpDAO exploiter's aave position, previously-affected ethereum:0xc02aaa39b223fe8d0a0e5c4f27ead9083c756cc2 core market on Ethereum now has available liquidity of ~$177m !
xitter.cf/aave/status/2052100832…

It seems the 0x1f4c_Kelp DAO Exploiter on ethereum is being liquidated (w/ ~$123m debt) in @aave
Here is the related tx:
etherscan.io/tx/0xe2391ea418…
The arbitrum position is also liquidated:
arbiscan.io/tx/0x78b41623cd2…

It seems the admin key of @wasabi_protocol has been compromised with the estimated loss of $5.5m across multiple chains, including ETH, BASE, BLAST, and BERA chains.
Here is the related tx to add the malicious admin:
etherscan.io/tx/0x11ff84ffbd…


A victim just lost a Alchemix Yearn yvVault position $yvWETH (estimated $~1m), from an earlier approval to an unverified contract (etherscan.io/address/0x143a7…). This unverified contract, created 10 days ago, turns out to be buggy and can be exploited for arbitrary call execution.
Here is the vulnerable logic from the decompiled contract, affected in the following exploit tx: etherscan.io/tx/0xebaaab69ba…

It seems a @tradingprotocol vault, i.e., YieldCore-3rd-deal, was exploited with $398k loss.
There is a missing check on the caller authorization, which is exploited to drain all funds from the vault.
Here is the related tx:
etherscan.io/tx/0x6b04344d56…

Just wanted to clarify that the exploited vault was permissionlessly listed in @TradingProtocol, not part of the protocol itself: tradingstrategy.ai/trading-v…

It seems the @KelpDAO exploiter moved stolen funds via @LayerZero_Core to Tron for laundering.
Related steps:
1: Transfers on Ethereum:
Kelp DAO Exploiter1
-> 0xF9802c5EB6b972Ba686aFa7CA615910Ea8310b85
-> 0x42a71A7ED12582378d4A4567A1af6Bad4f03dF84
-> 0x0BA9e88059c85fBD76b0C025F00C8B8Ebb0AddDf
2: Cross-chain: Ethereum -> Arbitrum:
0x0BA9e88059c85fBD76b0C025F00C8B8Ebb0AddDf (Ethereum)
-> 0x4D5A08A96D644d7CA7F4541E1512a53D55aA5842 (Arbitrum)
3: Swap on Arbitrum from ETH -> USDT
4: Cross-chain: Arbitrum -> Tron
0x4D5A08A96D644d7CA7F4541E1512a53D55aA5842 (Arbitrum)
-> TLTCf565jGgSeCsUhBpWuPhrrHcGGX9ekT (Tron)
#PeckShieldAlert The @KelpDAO exploiter bridged $ETH from #Ethereum to #Arbitrum via @AcrossProtocol, swapped for $USDT0, and subsequently routed funds to @trondao via @LayerZero_Core


I believe the @KelpDAO exploiter is shocked 😱😱😱!
It turns out @arbitrum security council just frozen 30,766 ETH ($71m) tied to the KelpDAO exploit: xitter.cf/arbitrum/status/204643…

The latest fund movement from the @KelpDAO exploiter: arbiscan.io/tx/0x5618044241d…
