

P1 Security is a leading provider for its offensive security services, software and trainings on mobile networks unique protocols (2G to 5G)
Paris, France
Joined October 2011
- Tweets267
- Following88
- Followers1K
- Likes28





Live today, 15:00 CEST: Inside a telecom security assessment. Martin Kacer on how mobile networks are actually tested, SS7 to 5G, and what each kind of test misses. Free, with Q&A and replay. watch.getcontrast.io/registe… #TelecomSecurity

Home-routed roaming carries a partner's SIP traffic straight back into the home IMS core.
New whitepaper: the SIP interconnect threat model, and where a signalling-aware SIP IDS fits alongside the SBC.
p1sec.com/white-paper/sip-in…
#VoLTE #TelecomSecurity

QCSuper has a sequel: DiagNG, a new GUI-based open source tool for Linux that produces PCAP/GSMTAP captures from Qualcomm Snapdragon basebands for Wireshark, NR/5G included.
Launch post: p1sec.com/blog/presenting-di…
Code: github.com/P1sec/DiagNG

A $1000 fibre switch and physical access to one cell site is enough to man-in-the-middle unencrypted backhaul. The user plane is often unprotected: sniff it, inject into it.
From our Cloud RAN webinar. Full session: watch.getcontrast.io/watch/p…
#CloudRAN #TelecomSecurity
India Mobile Congress 2026, 7 to 10 October, Yashobhoomi, New Delhi. P1 Security will be there.
Want to talk signalling, interconnect or 5G core security? Book a slot with our team: p1sec.com/contact
@exploreIMC #IMC2026 #TelecomSecurity

The AMF trusts the device (N1), the gNB (N2) and the 5G core (SBI) differently. Our AMF Under Pressure replay walks the attack paths.
watch.getcontrast.io/registe…

Most O-RAN interface protections are mandatory to support and optional to enable.
The gap between supported and switched on is a fixable deployment question.
New whitepaper on open fronthaul, E2, O1, the RIC and xApps:
p1sec.com/white-paper/o-ran-…
#ORAN #TelecomSecurity

A pentest describes your network on the day it was tested. Networks do not stay still: new elements, new interconnects, new 3GPP features, patch and config drift. Re-testing an estate audited years ago keeps finding new exposure.
p1sec.com/ugtmns

HLR, HSS, UDM: the subscriber database holds identities, authentication material and service profiles. Interconnect filtering decides who may ask, not how the element answers a malformed question.
p1sec.com/white-paper/hackin…

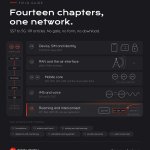
No single public place tells you how mobile networks actually break. So we indexed ours: 191 articles, 14 chapters, SS7 and Diameter through to 5G SBA, O-RAN and IMS.
No gate, no form, no download.
p1sec.com/ugtmns

Tomorrow, live with Titan.ium: Offense vs Defense in Telecom Security.
What a mobile network hands over to a stranger, and the signalling firewall rule that stops it. Built live on screen.
15 Sept, 16:00 CEST.
titaniumplatform.com/webinar…
#TelecomSecurity #SS7
A CVE feed says a vulnerability exists. It does not say what it does inside a mobile network. The P1 VKB holds 2,200+ telecom vulnerabilities from SS7 to 5G, with impact and remediation context. p1sec.com/product/vulnerabil…

11 September 2026: the Cyber Resilience Act's reporting clock starts. Actively exploited vulnerabilities in products with digital elements, early warning within 24 hours. Telecom equipment included. p1sec.com/services/supply-ch…

SS7 was built in the 1980s for a closed club. That club now has 1,000+ interconnected nodes, and MAP/CAP/SCCP still carry no sender authentication.
Joint webinar with Titan.ium, 15 Sept, 16:00 CEST (15:00 London, 10:00 NY).
titaniumplatform.com/webinar…

The most damaging findings in 5G core pentests are rarely exotic: default credentials, reused root SSH keys, SSRF that turns the SCP into an internal scanner.
New whitepaper on the five classes we find most.
p1sec.com/white-paper/top-5g…
#5G #TelecomSecurity

P1 Security is at LEAP 2026 in Riyadh, 31 Aug to 3 Sept. Vikas Sharma is there taking meetings. If you run a mobile network in the region, regulate one, or depend on one, let's compare notes on what your signalling layer exposes. [email protected]
#LEAP26

One vendor compromised, and you are inside many 5G cores at once. No internet exposure needed.
El Mehdi Regragui on the 5G core supply chain path, from our AMF Under Pressure webinar. Full replay:
watch.getcontrast.io/watch/p…
#5GSecurity
Live in under an hour: AMF Under Pressure.
N1, N2, SBI. Three interfaces into the AMF, each trusting a different neighbour. El Mehdi Regragui on the attack paths across each, from P1 pentesting on the 5G core.
Today 15:00 CET. Replay if you register.
watch.getcontrast.io/registe…
Ask an operator where its attack surface is and the answer depends who is in the room: SS7, GTP, IMS, RAN. TelcoASM puts them in one matrix so you can see where exposure concentrates. Self-assessment, no scan. telcoasm.p1sec.com

Smishing defences read the message. But SMS fraud lives in signalling: spoofed origins over SS7, A2P grey routes bypassing the SMSC. Content filters can't see that. p1sec.com/blog/sms-based-att…
