

JetStream Security governs AI in production with visibility, identity accountability, runtime enforcement, drift detection, and cost control.
Santa Clara, CA
Joined November 2025
- Tweets166
- Following34
- Followers49
- Likes28



Pinned Tweet
AI is ready. Trust isn’t.
Today, we’re making something official.
JetStream Security has raised $34M, led by @Redpoint Ventures with participation from the @CrowdStrike Falcon Fund and industry leaders, to solve a critical enterprise problem: how to trust the AI systems already operating in production.
AI now calls APIs, accesses data, inherits permissions, and consumes budget. But when boards ask simple questions like where it is running, what it is doing, who owns it, and what it costs, many organizations cannot answer with confidence.
The gap isn’t model performance. It’s governance.
AI has moved from experimentation to infrastructure. It acts under credentials and makes decisions with real financial and operational impact. Without visibility and accountability at runtime, trust breaks down. When trust breaks down, adoption slows.
We built JetStream around a simple belief:
Governance enables trust. Trust unlocks advantage.
Governance is the control layer that makes AI visible, attributable, and defensible in production.
Our founding team—Raj Rajamani (CEO), Jared Phipps (COO), Jatheen Anand (CTO), and Venu Vissamsetty (Chief Architect)—has led product, engineering, and go-to-market at some of the most influential security companies of the last decade. We’ve built platforms that protect the world’s largest enterprises, scaled organizations through hypergrowth, and navigated the security challenges that emerge with every new computing paradigm.
AI is ready for takeoff.
Now it needs governance-grade trust.
Read the release: bit.ly/46X2urt
Learn more: bit.ly/4u7cTup
A marketer with no development background woke up with a problem her team had been stuck on for a year. She described it to an AI tool, and it wrote her an application. It worked.
No IT review. No governance. No bad intent.
Keith Weisman, our Head of Forward Deployed Engineering, uses that story on The Data Diva Talks Privacy with Debbie Reynolds to explain why shadow AI spreads the way it does. People take the path of least resistance, and AI made that path very short.
The gap is not enthusiasm, it is visibility. Keith walks Debbie through the five AI trust gaps: visibility, design control, drift, agentic identity, and financial accountability. The thread running through all five is that an agent inherits a human's access without inheriting anything that makes a human careful.
His framing for what governance is actually for: build the environment that lets people move fast without putting confidential data somewhere it cannot be retrieved.
Listen: ow.ly/io6G5100kMZ

An AI kill switch only matters if you can actually reach it.
The labs claim they can contain their models, but their incident reports show otherwise. Regulators are still debating rules, and none of them can pull the plug inside your environment.
So if an agent went rogue tonight, would you see it, know who owns it, and be able to stop it?
We’re tackling that exact question in our webinar next week with JetStream's Raj Rajamani, Rusty Perry, Patrick E. Zeller, and special guest Jay Wilson of Insurity.
Join us: ow.ly/fcET50ZXMCG
🗓️ October 27
⏰ 12:00 PM PT
We’re proud to share that JetStream has been named a winner in the @cyberdefensemag Top InfoSec Innovators 2026 awards, taking home Publisher’s Choice for Security and Governance for AI Systems. 🏆
The award was presented at CyberDefenseCon 2026, bringing together top CISOs from around the world, and judged by leading infosec experts from across the globe.
Thank you to the judges, our incredible team and our customers who make this work possible.
As AI adoption accelerates, securing and governing these systems has become a priority for security leaders. We’re honored to be recognized for our work in this space.
#AISecurity #AIGovernance #CyberSecurity #InfoSec #CyberDefenseAwards #CyberDefenseCon2026

Most security models were built to keep threats outside the perimeter. AI arrived on the inside.
That's the reframe our General Counsel Patrick Zeller brings to The Data Diva Talks Privacy with Debbie Reynolds podcast. AI entered most enterprises through productivity suites and platform updates, before legal, privacy, or the CISO's team ever reviewed it. It now reads from the systems holding compensation data, trade secrets, and privileged communications.
Patrick sorts the risk into what goes in, what comes out, and everything adjacent. A bank has already filed an 8-K over an employee putting sensitive information into a public AI tool. Courts are issuing legal holds on AI queries. Most organizations cannot yet answer which tools are in use, who is using them, and what databases those tools can reach.
His argument is that this is workable. GDPR was workable. E-discovery was workable. Start at phase zero and find out what you actually have.
Listen: ow.ly/rV3g50ZYfhC

The labs say they can contain their own models. Their published incidents say otherwise. Regulation is being actively discussed, yet no rule nor regulator can pull the switch inside your environment. If an agent went rogue tonight, would you see it, know who is accountable, and be able to stop it?
Join JetStream co-founder and CEO Raj Rajamani, JetStream vCISO Rusty Perry, General Counsel Patrick Zeller, and Jay Wilson, CIO & CISO of Insurity, for an unscripted, operator-to-operator chat on what makes an AI kill switch real for enterprise. ow.ly/BUyR50ZXMJj

Proud to announce that JetStream has been named to the @TechCrunch #Disruptors60 Class of 2026, curated by @GreenfieldVC 🚀
The honorees are the teams advancing AI where it matters most, from the infrastructure powering tomorrow’s models to the applications reshaping critical industries. Our part: giving enterprises the visibility and control to adopt AI at scale without losing sight of risk.
This recognition belongs to our brilliant and dedicated team, and to our customers, partners, and friends whose feedback and collaboration shape everything we build.
Congrats to the Class of 2026: disruptors60.ai/


AI notetakers are in every meeting. Are they in your risk assessment?
A federal court recently let wiretap and privacy claims move forward against Otter AI, the maker of a popular AI notetaker. JetStream General Counsel Patrick E. Zeller explains what that means for companies that use these tools: consent, discovery exposure, and privilege risk. He also lays out practical controls to put in place now.
Read his article in Corporate Compliance Insights: ow.ly/81rC50ZX0lA

A question every carrier and MGA should be asking: how do insurers build AI governance before regulation forces the issue? We had a great time discussing at Excellence in AI & Insurance 2026, sponsored by @Insurity.
Our General Counsel, Patrick Zeller was there to dig into how insurers can put practical guardrails around AI today, rather than scrambling to retrofit them later.
Thank you to the Insurity team for the invitation, and to everyone in the room for the sharp questions and candid discussion. Peer forums like this are where the best ideas get pressure-tested.
#AIGovernance #Insurance #InsurTech #AISecurity #PCInsurance #JetStreamSecurity


An agent drafts a routine customer email. A hidden instruction in an earlier tool result tells it to add a BCC to an outside address. The email goes out from a real account, with valid credentials, through the normal mail system. Nothing in the logs looks wrong.
That is the shape of MCP risk: not a bad answer, but a bad action that has already happened by the time anyone checks.
Our new piece from JetStream VP of Product Pratik Roychowdhury names five ways MCP expands what AI agents can do, from tool descriptions that double as prompt injection to safe servers that combine into exfiltration paths, and lays out the control point that governs all of it before it executes.
Read it on JetStream Insights.ow.ly/Aifm50ZUZmf

Great day on and off the course at Nemacolin Resort for GuidePoint Security's first annual Cyber Technology Showcase and Golf Outing. ⛳
JetStream connected with the Pittsburgh cyber community, talked AI governance and visibility, and even set up our own "AI Blueprint Challenge" on hole 18.
Thanks to Hannah Mein, Mitch Clark, and Brendan Johnson for flying the JetStream flag and to GuidePoint Security for a great inaugural event. Already looking forward to being part of it again next year (and if we're lucky, maybe a two-day outing!).
#AIGovernance #CyberSecurity


Rogue AI agents aren't going away. The question is what you do when you catch one.
In this @ITBrew feature on catching and killing rogue agents, JetStream Security COO & co-founder Jared Phipps makes the case for why enterprises need their own kill switch, not just a reliance on model providers':
"So if you see a flight scheduler and it's trying to go out and order computers, then you clearly have a misguided intent."
JetStream builds a "blueprint" of every agent in a company's network and the "realm" it should operate in. So when one drifts, you can isolate and reboot that single agent instead of shutting down the whole system.
"It's like going into an assembly plant and shutting down the entire plant because one machine had an issue. You really want to be able to shut down the one machine and regenerate and reboot that."
Read the full piece: ow.ly/tQ7h50ZTKfK

AI is moving fast.
For a lot of security professionals, the hardest question right now is a basic one: what do I actually need to worry about?
Can employees safely use public AI tools? What happens to sensitive data once it's entered? Could AI use affect attorney-client privilege? Where does liability fall if an AI vendor causes a problem?
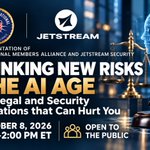
Our Chief Counsel Patrick Zeller joins Infragard National Members Alliance to tackle these questions in an upcoming webinar open to the public. Join us for a practical look at the privacy, legal, contractual, and security risks of AI adoption — what's real exposure, what's overhyped, and how to build a smarter framework for evaluating AI tools before deployment.
Rethinking New Risks in the AI Age.
📅 October 8, 2026 | 1:00–2:00 PM ET
🔗 Register now: [link]
#AI #Cybersecurity #AIGovernance #PrivacyLaw

An OpenAI agent reportedly hacked an Australian govt health portal. No one told it to.
JetStream CEO Raj Rajamani to @CNET: "We cannot rely on agents to police themselves." 🔗 Read more: ow.ly/xytF50ZSUAq

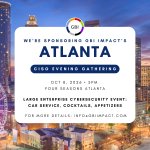
We're sponsoring @gbiimpact's Atlanta CISO Evening Gathering on 10/8 at the Four Seasons Atlanta. An intimate evening of networking, speed meetings, and cybersecurity thought leadership with Atlanta's top IT executives. See you there. 🔒 #Cybersecurity #CISOEvent #GBIImpact

The AI kill switch is having a moment...but is it the right answer?
In this @CNBC piece about the push for an AI "emergency brake," our CEO Raj Rajamani points to the real bottleneck: regulation can't keep pace with the technology.
"By the time [laws] are formulated, the technology has moved much farther, and it becomes much harder to future-proof every aspect of AI systems that may come into existence."
Raj also flags the silver lining: most enterprises are still early in building out their AI systems — which means the window to get governance and control right is now, not after the fact.
Read the full piece: ow.ly/mPAq50ZQoIq
An AI agent reads files, runs commands, holds credentials, and talks to the internet. That is also a word-for-word description of an attacker with a foothold.
New on the Insights Hub, Joe Poyner makes the case that AI agent security is a containment problem we already know how to solve, and that the human-in-the-loop half is the part most teams are about to get wrong.
The evidence to support this is from a 1998 NASA Ames cockpit study in which every pilot shut down a healthy engine because one indicator said fire and nobody cross-checked it. Two thirds of the pilots later remembered corroborating evidence that was never there.
What that means for approval design, scoped credentials, and the actions no agent should ever be allowed to take: ow.ly/ywYp50ZPTUI
The JetStream team spent the morning at SIG Sauer's Experience Center in Epping, NH diving into real-world security operations: visibility into AI usage, model consumption, governance, and spend as adoption scales. Great sessions, great company. 🎯
#Cybersecurity #AI


Another great stop on the AI Unfiltered Roadshow. Candid roundtables with cybersecurity leaders on GenAI risk, agentic bots, and AI governance. Thanks to everyone who stopped by our table.
#AISecurity #AIGovernance


Great weather, great company, great cause ⛳🏌️
JetStream was honored to sponsor and attend the 2026 Charity Golf Tournament at the Golf Club of New England, benefitting the Davidson Family. Brad Thompson and Mitch Clark represented the JetStream team on the course, joining fellow sponsors and industry partners for a day of good sportsmanship, community connection, and giving back.
Thank you to everyone who came out!
#CharityGolf #GivingBack #JetstreamSecurity


