

AppSec Testing as-a-Service
Joined December 2017
- Tweets567
- Following171
- Followers3K
- Likes358

A ticket marked "Resolved" is a claim, not a fact. Rerun the original exploit, then vary it: different encoding, different parameter, a neighboring endpoint. If the fix only blocks the exact payload in the report, you fixed the report, not the bug.
inspectiv.com

The big objection to bug bounty: triage bandwidth.
Unmanaged programs are noise machines. Inspectiv replicates every submission before your team sees it.
You get validated findings. Not a pile of researcher notes.
inspectiv.com/bug-bounty

SSRF turns one URL-fetch feature into a cloud credential leak.
Point it at the metadata service, steal the token, pivot from there. Lock down metadata (IMDSv2 on AWS), allowlist egress, scope IAM, then have a human try to chain it.
na2.hubs.ly/H08kb1d0

A clean pentest report is a statement about last quarter's code. Keep the pentest for depth. Add retesting and ongoing researcher coverage for everything that changes after sign-off.
inspectiv.com/pentesting-as-…

Researchers exposed 32 zero-day flaws on day one of Pwn2Own Ireland.
32 zero-days in a single day, because researchers get paid to find them.
Paid, time-boxed offense beats waiting for someone unpaid to find it first.
Read more: na2.hubs.ly/H08fr3x0
#CyberSecurity #AppSec

"We're too small for bug bounty."
Maybe. But you might just be too small to run one without help.
Managed programs absorb the operational overhead: private scope, vetted researchers, validated findings only. No triage burden on your team.
inspectiv.com/bug-bounty

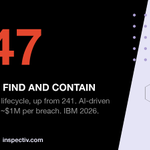
247 days to find and contain the average breach.
AI-driven attacks are up 56% and add ~$1M per breach.
Attackers are on machine time - you should be, too.
na2.hubs.ly/H0899HR0

1 in 3 Critical findings from our bug bounty programs is SQL injection.
Why is a vulnerability class that's been around for decades still so prevalent, and what can security teams do about it?
na2.hubs.ly/H085fLh0

More findings don't mean more security if nobody can tell which ten matter.
Alert fatigue turns real vulnerabilities into backlog noise. Validated, prioritized triage is how they get fixed.
inspectiv.com

Scanners check known patterns.
Researchers think about how to break your specific thing, then do it.
Logic flaws, chained bypasses, race conditions: not in any signature database.
na2.hubs.ly/H081gsG0
#BugBounty

Bug bounty gives you findings. It also gives you researchers who know your architecture and keep coming back every quarter.
With every cycle, they bring more context to the hunt.
#BugBounty

AI-generated code fails in predictable, repeatable ways, and attackers are cataloguing the patterns.
The bugs aren't new. But AI ships them faster than review scales, and confident output gets less scrutiny than it should.
na2.hubs.ly/H07X2l00

Flooding your queue with unverified findings doesn't just waste triager hours - it trains your team to skim every alert, including the real one that's buried. Noise has a cost.
na2.hubs.ly/H07VHq_0

Marking a bug "resolved" and actually fixing it are different events.
Patch the specific PoC, close the ticket, skip retesting, and the root cause often survives untouched. Months later: same bug class, different endpoint.
Close the loop before you close the ticket.
inspectiv.com

CISA: hackers are exploiting a maximum severity GitLab flaw (CVE-2026-85706) that lets unauthenticated attackers read credentials via a path traversal bug. Patched Thursday. Probing began the next day.
Read more:
na2.hubs.ly/H07PxpK0

"We've never had a critical finding."
We've heard this from new Inspectiv customers. Clear the annual pentest, run automated scans, zero open criticals.
That isn't necessarily proof your program is secure.
na2.hubs.ly/H07M-Zh0

API security is business logic.
Can I swap a user ID and see someone else's data? Does rate limiting hold on every path, or just the happy one?
AI clears the repetitive work so researchers can spend their time on the reasoning and chaining that finds these bugs.
na2.hubs.ly/H07HvRz0

Google warns of new Chrome zero-day flaw exploited in attacks.
Google patched CVE-2026-85046, an actively exploited V8 engine type-confusion zero-day, along with 11 other Chrome vulnerabilities. It's the sixth actively exploited Chrome zero-day patched this year.
Read more: na2.hubs.ly/H07FvhN0
#CyberSecurity #AppSec

What's the cost of a vuln your team never found?
Not just IR. Churn + fines + engineering fire drills (+ the board meeting).
Bug bounty ROI is not a close call.
na2.hubs.ly/H07BXQy0

API scanners test what they're told exists. They can't test the debug route someone forgot to remove or the GraphQL field the frontend never queries but the resolver still serves.
inspectiv.com
