

Upskill your business with technology practitioners
Santa Barbara, California
Joined March 2007
- Tweets69.1K
- Following1.1K
- Followers257K
- Likes9.2K






2027 planning is underway. Is independent research in your budget?
When a GigaOm Radar in your category publishes, its value depends on how fast you can use it. If the budget has to be requested after the report is out, momentum isn’t on your side. Lost visibility means lost opportunity.
See how to build the Radar into your 2027 budget:
gigaom.com/blog/blog-why-the…


When you're making a purchase, do you trust a company's marketing more than a neutral third party? Your marketing tells buyers what your technology can do, but independent research helps them understand how it stacks up.
Enterprise technology buyers increasingly rely on third-party analysis to evaluate solutions, compare capabilities, and build vendor shortlists—often before engaging with a sales team.
For technology vendors, engaging with research platforms builds credibility, demonstrates differentiation, and provides insights that can strengthen both go-to-market strategies and product roadmaps.
In our latest blog, we explore why technology vendors engage with independent research platforms, what they gain, and how GigaOm's practitioner-led approach connects technology capabilities to the priorities of enterprise buying committees.
portal.gigaom.com/blog/why-t…

CISOs: your password manager probably "supports passkeys." Can it retire its own master password?
For most of the field, the answer is no.
In GigaOm's latest Radar for Enterprise Password Management, analyst Paul Stringfellow found that passkey storage is now broadly delivered, but a master-password-free vault remains rare.
Across much of the market, SSO users still keep a permanent vault password: the exact credential a passwordless program is trying to eliminate.
In our new breakdown:
• Storing passkeys vs. retiring the master password.
• Why the vault's key architecture decides, not the feature checkbox.
• What changes once there's no master password to fall back on.
• Why most organizations can't say which authenticators hold their credentials.
If passwordless is on your identity roadmap, read this before your next vault renewal.
Read more: portal.gigaom.com/blog/beyon…

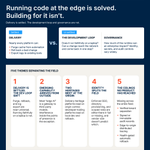
Running code at the edge is no longer the hard part, says Andrew Green in the latest GigaOm Radar for Edge Development Platforms. Delivery is settled: nearly every platform can purge, roll back, and export. The development loop and governance are not, and that's where the 14 platforms in this report separate. Five themes show how.
portal.gigaom.com/report/gig…

Product marketing teams have numerous conversations with a variety of stakeholders, and one analyst report can't support all of them. Our latest blog explains how different GigaOm offerings can work together:
→ Radar Reports provide criteria-based market evaluation and competitive context.
→ CxO Brief Lite translates Radar findings into an executive-ready narrative.
→ Sales Enablement helps teams apply the research accurately in customer conversations.
The right question isn’t “Which report is best?” It’s “Which evidence does this audience need?”
Read the full article: portal.gigaom.com/blog/blog-…

What does “best” mean when the CTO, CIO, and CISO are each looking for something different?
That’s something we address in the refreshed GigaOm Radar Report, designed to fill a gap left in traditional enterprise technology evaluations. Rather than a single ranking built around what a product can do, we’re providing insights targeted directly at the people who do the buying.
In this blog, GigaOm CEO Tom Garske explains how the methodology evaluates and scores vendors on what buyers actually value, and gives buyers clearer, more actionable answers. portal.gigaom.com/blog/blog-…

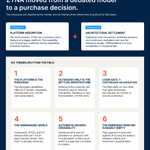
Zero trust network access stopped being a debate and became a purchase decision.
We evaluated 33 platforms against 28 criteria across 3 buyer lenses in our latest ZTNA Radar report. Two pressures are organizing the market. Six themes show where they're pulling the field apart.
See the full report: portal.gigaom.com/report/gig…

84% of CIOs say their role is now digital strategy, not infrastructure. A bad vendor bet doesn't just burn budget — it stalls you long enough for a competitor to get ahead.
40 vendors claim the same things. Before you trust a market intelligence platform, check who wrote it (practitioner or outsider) and whether payment can move the score.
Test: pull a sample report in a category you know cold. If it holds up there, trust it elsewhere.
That's the bar behind the GigaOm Radar. Read more: portal.gigaom.com/blog/blog-…

The debate around ZTNA isn't about the model anymore, says analyst Chris Ray in the latest GigaOm Radar report. It's moved to procurement.
Every product now brokers access one app at a time, on identity + device posture—and nearly all are sold as the end of the VPN.
Full report: portal.gigaom.com/report/gig…

There's one vantage point an attacker can't avoid: the network itself. Premiering today, the latest GigaOm Radar for Network Detection & Response—the first on our redesigned methodology—assesses 30 platforms that turn network evidence into verdicts. portal.gigaom.com/report/rad…

Business Disruptions in Tech with Chris Edson of Tenable xitter.cf/i/broadcasts/1gqxvrNnW…
Business Disruptions in Tech with Kavitha Mariappan xitter.cf/i/broadcasts/1OwGWeNbl…
"If you can't trace the data, you can't trust the model."
AI is forcing a shift from manual data engineering to operational DataOps.
Why? because pipelines built to deliver data "occasionally" break when AI models demand reliability every single day.
See how Sovereignty and Lineage are reshaping the stack in 2026: portal.gigaom.com/blog/data-…

The next great cloud breach will be blamed on a "customer click."
But history will blame the industry for pretending the bots were out of scope.
Non-human identities (service accounts, tokens, keys) are the new attack surface, and the "Shared Responsibility" model is failing to protect them.
Chris Ray breaks down why we need to stop accepting "tenant misconfiguration" as an excuse for risky vendor defaults.
Read the full post: portal.gigaom.com/blog/cloud…

ITAM sustainability features are up 70% year-over-year.
But adoption is uneven. Only a handful of vendors are moving beyond basic tracking to offer real decision support for purchasing and end-of-life cycles.
See which tools actually move the needle on your carbon footprint: portal.gigaom.com/blog/susta…

"What is Endpoint Security?"
If that’s your headline, your marketing is already dead. 💀
The internet is drowning in AI-generated beige prose. To survive, you need to stop writing for algorithms and start writing what ChatGPT can't fake: failures, deep analysis, and "dog food" logs.
See what actually works in the age of the Dead Internet: 🔗 portal.gigaom.com/blog/the-d…

Attackers are automating. Is your endpoint defense keeping up?
Detection alone is no longer enough. Complexity and alert fatigue are breaking security teams. Join GigaOm and WatchGuard to explore the 2025 EDR Radar Report findings and see how AI and automation are redefining endpoint protection.
Register for the webinar: secure.watchguard.com/WB-Glo…

Business Disruptions in Tech with Doug Merritt of Aviatrix xitter.cf/i/broadcasts/1yoKMPwRq…
Studies show 60-70% of engineering time is wasted on alert noise. The solution wasn't "AIOps"—in fact, AIOps made the confusion worse.
AIOps is dead as a unified category. 2026 is the year of fragmentation, LLMOps, and autonomous agents.
Stop buying the buzzword. Read the 2026 operational forecast from GigaOm’s Whit: portal.gigaom.com/blog/aiops…

"Data security, without resilience, is just insight without safety."
The gap between SecOps and Data Protection is leaving enterprise data dangerously exposed. As AI accelerates data growth, dynamic, real-time backup policies are no longer optional.
Paul Stringfellow breaks down the Veeam + Securiti AI acquisition and the future of data defense. Read the latest Analyst Lens: portal.gigaom.com/blog/with-…
