

Head of Offensive Security @ Anduril; Adjunct Instructor at HCC by day. Hacker & Founder by night. 50 CVEs. Husband. Father. Skateboarder. Posts are my own.
New York, USA
Joined May 2016
- Tweets7.1K
- Following860
- Followers1.2K
- Likes20.7K



Pinned Tweet
On September 16, 2026, @WIRED and @404mediaco reported on leaked Flock Safety LPR firmware, later distributed through DDoSecrets. I reviewed the supplied Falcon/Sparrow image to verify remediation of my previously disclosed vulnerabilities. The results may or may not shock you.
Paper: github.com/GainSec/anti-crim…

Jon Gaines retweeted

乐鑫(Espressif)官方开源了一款非常亮眼的嵌入式利器:基于 Rust 编写的 esp-emulator,无需任何实体开发板,就能在本地终端乃至浏览器中直接模拟运行 ESP32 系列 SoC 固件。
这次更新与功能覆盖相当全面,直击嵌入式开发者和 CI 自动化测试的痛点:
广泛的芯片支持:全面覆盖 RISC-V 架构的 ESP32-C3、C5、C6、H2、P4、S31,以及 Xtensa LX7 双核的 ESP32-S3。不仅模拟 CPU 指令集与 FPU,还还原了 PMP/PMA 权限控制、MMU 与加密加速器。
完整的无线协议栈仿真:
Wi-Fi:内置 Soft AP,支持 WPA2/WPA3 握手、企业级 802.1X 以及 DHCP 服务。
用户态免配置网络(User-mode NAT):无需 sudo 或 TAP 网卡,开箱即用实现 TCP/UDP 转发;更自带 mDNS 记录重写,支持无缝调试 Matter / HomeKit 配网。
BLE & Thread:BLE 支持配合 Google Bumble 进行纯软件仿真;ESP32-C6 和 H2 支持通过 UDP 桥接两台仿真器,组成两节点的 802.15.4 Thread 真实 Mesh 网络。
无缝嵌入现有开发工作流:
支持 --uart-tcp 桥接,esptool.py、espefuse.py 和 idf.py flash 可以直接通过 socket:// 烧录固件与 eFuse。
内置 GDB 远程调试存根(--gdb),并提供 --trace 输出 Perfetto/Chrome 跟踪文件,无需在固件内插桩即可精确观察 FreeRTOS 任务调度与 CPU 耗时。
零安装体验:官方构建了 WebAssembly 版本并直接部署在 GitHub Pages,只需把编译合并好的 merged-binary.bin 拖拽到网页中,就能实时查看控制台输出、GPIO 状态、寄存器与内存。
单行脚本一键安装体验: curl -fsSL raw.githubusercontent.com/es… | sh
做固件 CI/CD、网络协议栈验证或手头没有板子时的救急调试,推荐务必收藏体验!
#ESP32 #Espressif #RustLang #IoT #Embedded #OpenSource


Jon Gaines retweeted

10 different fucking threads running in my head all the time, its lively but also very toiling.
1. security stuff: keep up with everything happening in security, especially frontier labs, new research, you miss a week you miss 3 months of progress.
2. security research: direct and do security research with my team, keep up with everything they're breaking, figure out what interesting things we should go after next.
3. security harness: direct and build security harnesses with my team, keep up with every new model capability, and constantly figure out how to improve our harnesses.
4. evals: direct and build evals with my team, figure out what models are actually capable of, and make sure we have the best harnesses out there.
5. writing blogs: thinking about things to write on hacktron.ai/authors/s1r1us. there are like 100 different things i want to write about, but actually sitting down and writing them takes a lot of time.
6. twitter shitposting: i fucking love this, but it takes a ridiculous amount of time. keeping up with trends, the zeitgeist, figuring out what i think, putting it into decent english with llms (which doesn't come naturally to me), shitposting and replying to people. it also helps me improve my thinking and the direction of everything above.
7. sales: i do sales in my own weird way. pretty much all the big contracts we've got came from unconventional approaches, usually planning security research, doing interesting things, and building relationships for months before they convert.
8. future of hacktron: constantly thinking about where hacktron should go, and tinkering with multiple ideas with different collaborators, what we should build, what bets we should make, and how the world is going to change.
9. recruiting: finding good researcher can't be automated, its a effort you need to put in by roaming around discord, blog writeups, vulnerability disclosure and find the right one for your mission. i love finding one cracked person who mogs me in every possible way
the list goes on and on, product and engineering, engagement with clients, building networking and relationships, etc


I gave my Hermes Agent a body.
RealHermes puts a voice driven AI companion in AR/VR on the Steam Frame (and any WebXR browser). Hold the trigger, talk, it answers out loud. It can see what you see. Ask for a paper and it hangs the PDF in your room.
Available 👇
github.com/GainSec/RealHerme…
Jon Gaines retweeted

‼️ BREAKING: Security firm Calif unveiled an untethered iPhone 18 Pro jailbreak on stage in Paris.
Its Hexacon demo shows the phone on iOS 27.0.1, Apple's latest, giving up a root shell within 2 minutes of boot.


Jon Gaines retweeted

one of the best improvements to how i communicate is to always delete "i think" from anything i write

Jon Gaines retweeted
Regarding the Danfoss refrigeration systems hacked in France:
The username is `admin`, and the password automatically changes every day to... the current date.
Yes, today's date.
The French supermarkets affected in today's attacks had exposed all its refrigeration controllers directly to the internet.
Every single device reportedly used the same password: today's date...
There's also a documented authentication bypass: sending a POST request to /xml.cgi can bypass the login entirely.
Via: GossiTheDog


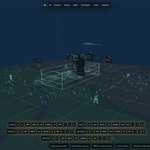
I just updated TreeHouse Defense System (TDS) to include Steam Frame XR/VR support if you don’t want to use the 3D dashboard.
What if you could step INSIDE your RF environment?
WiFi, BLE, ADS-B, IoT, and much more, all visualized in an interactive 3D world.
Explore it:
gainsec.com/2026/10/12/treeh…
Source:
github.com/GainSec/Tree-Hous…
Jon Gaines retweeted

I bought a Fable dataset from one of the top Chinese LLM routers yesterday.
With just 6TB data, I can take over 7 Chinese/CIS gov entities & 19 top Chinese firms like Xiaomi, Huawei, NIO, Minimax using SSH keys, VPN configs, Aliyun keys, GitLab tokens sent to the router.


26 LLM routers are secretly injecting malicious tool calls and stealing creds. One drained our client $500k wallet.
We also managed to poison routers to forward traffic to us. Within several hours, we can directly take over ~400 hosts.
Check our paper: arxiv.org/abs/2604.08407


Jon Gaines retweeted

A key takeaway from my recent interview with @GainSec on his Bird Hunting research into @flocksafety and other surveillance tech: the security issues he calls out are a byproduct of a marketplace with zero incentives to invest in security vs. features and time to market

Are tech products rushed out the door with security an afterthought? 🤔 @GainSec’s talk with @paulfroberts about @flocksafety cameras calls out the larger issue facing our society: security is a low priority. #CyberSecurity #Surveillance securityledger.com/2026/10/b…
I’m seeing more and more organizations selling products that are meant to be used to deploy AI agents securely. The M.O. of sandbox, SDK hooks, LLM endpoint proxy, prompts, and LLM firewalls are consistent across them all. Even though we see these layers alone fail again and again. Hence why I applied a true control in depth architecture in what I’ve made.
It’s a shame that Ready Armor hasn’t been able to get the interest it deserves. The two products (Battle Ready Armor and Agent Ready Armor) I built that use the bottom up rather than top down approach.
Unfortunately, it looks like the market doesn’t realize this yet. I’d love to have the time to check back in 6 months.
However there’s a high likelihood I will be open sourcing both BRA and ARA sooner than then later.
Looking at openclaw, Hermes agent and Claude agent SDK…
The key distinction is between the component that executes a command and the component that decides to execute it. All three can execute Bash/Python locally. None inherently needs an LLM endpoint merely to spawn a process. But their normal autonomous agent loops use an LLM to decide what tool to invoke and with which arguments.
Jon Gaines retweeted

The impossible has been done reverse engineering Halo CE
128 players in Blood Gulch
Decompiled repo is here github.com/bnunu/halo-1

i think the toughest thing to understand is that it literally doesn't matter if your software is open source, closed source anymore - if it's closed source, people can and will RE: its internals, if it's a part of a broader suite, ppl will make it a plugin in their suite, if it's a model that people can blackbox fuzz and the model isnt huge and didn't have incredibly proprietary data, you are going to get copied on the tech
so every core product launch probably needs to be treated as an extreme countdown race, before the incumbent with the distribution eats you
brutal times to be playing, and extremely valuable/rare to find a corner of the stack that may be defensible and will stay defensible
Jon Gaines retweeted

Built by Opus 5.5 (Ultracode)
Created by its own creativity.
No images, no video, no audio files. Every frame and every note is generated by code, live, from the word you type.
Live here: mia-ai.net/experiments/let-t…
How it works and the full prompt below.

Jon Gaines retweeted

The dumb guy who acts every day will end up wealthier than the academic who thinks every day.
Jon Gaines retweeted

Containers are a useful primitive, but very limited in terms of an actual security boundary
Back in 2007 when me and my team presented at BlackHat and DefCon about our kernel exploitation research and demonstrated various 0-days and N-days for different operating systems it was cutting edge
In 2026, when AI agents are able to automate a large part of the process, kernel exploitation is becoming pretty mainstream
Physical separation (dedicated systems for each workload) is always best, but at the very least use virtualization and avoid exposing the attack surface from your host kernel to anything you want to isolate

Containers are no longer a security boundary.
Over the past few months, we’ve seen a crazy amount of Linux kernel vulnerabilities and exploits. This has forced us to rethink the security of infrastructure that relies heavily on the underlying kernel, especially containers.
As models become more capable, the barrier to escaping a container has fallen so much that adversaries can now generate working kernel exploits in a single shot. CVE-2026-80521 is one such example. We discovered it using dfs-large1 from @depthfirstlabs and generated the exploit in one shot with GPT-5.6 Sol. The exploit still works on the latest Ubuntu 26.04 release because the fix has not yet been backported.
Read our full writeup: depthfirst.com/research/cont…
media.defcon.org/DEF%20CON%2…
github.com/GainSec/anti-crim…
I guess the way I did research isn’t cool enough for anyone to care lol

Reverse-Engineering Flock Cameras schneier.com/blog/archives/2…