



Finn Lobsien retweeted

over the past few weeks, we leaked thousands of API keys across the NYC subway!
please don't try this at home.


Finn Lobsien retweeted

Access denied. Credential required.
On October 21 at 1 PM ET, see how Agent Vault gives AI agents access to the services they need without ever exposing the credentials behind them
We’ll walk through Agent Vault live and show how it works with tools like Claude Code and Codex, and answer your questions.
Save your spot: infisical.com/webinars/live-…
Finn Lobsien retweeted
A credential an AI agent can read, is a credential it can leak.
Introducing Agent Vault: a new Infisical product that lets Claude Code, Codex, and other agents call the APIs and services they need, without holding real credentials.
With Agent Vault:
> Your agents work as they normally do, with no code changes
> A prompt-injected agent can only reach preapproved HTTP services, down to exact methods and paths
> Agent sessions expire on a schedule you set, and every request is logged
Finn Lobsien retweeted
If your agents run in @daytonaio sandboxes, you can now manage their keys in Infisical alongside every other secret your team uses!
Infisical now syncs copies of secrets straight into Daytona's secret store. Daytona keeps the real values out of the sandbox, and Infisical keeps the secret values current. Rotate a key in Infisical and every sandbox that references it gets the new value on the next sync, with no changes to your create calls.
Available on all plans, including free!
Finn Lobsien retweeted

DevOps / DevSecOps folks, how are you managing secrets in Terraform?
In this video, I walk through .tfstate, ephemeral values, write-only arguments, and how a secrets manager fits into the picture.
Curious what you're doing out in the wild. What's working well for you? 😃

Finn Lobsien retweeted
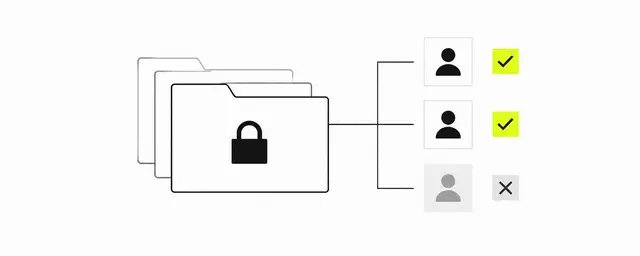
You can now give someone access to production Redis without giving them the password!
You put the password into Infisical once. After that, you decide who has access. Anyone with permission can open Redis from their browser or terminal without ever seeing the password. Infisical keeps logs for every command.
Live in Infisical PAM today! If you haven't looked at Infisical for privileged access management yet, the list of supported account types is growing every week. Docs below 👇
Finn Lobsien retweeted
"How do you share .env files as a team?"
I see this question all too often. The answer is "You don't". And you actually don't need a .env file at all!
In this video I break down what environment variables are, what the environment really is, and how runtime injection with centralized secrets can help deliver env vars to the environment and solve the problem of secret sprawl.
Ditch the .env file. There's a better way.
Finn Lobsien retweeted
I pasted this API key into Claude and it told me to rotate it immediately.
Is this supposed to make it harder to read or something?

Finn Lobsien retweeted
Most people know Infisical for secrets management but you can also use it for privileged access management (PAM) to access resources like databases too.
This release is a step forward specifically in Infisical’s PAM account discovery functionality where we can help surface existing accounts.

New in Infisical: Postgres account discovery!
Infisical PAM can now scan your Postgres instances and surface every account that can log in, including the ones no-one is tracking. Pick the accounts you want to bring under management, and rescan on a schedule to catch what changes.
No network exposure: the scan runs through your Infisical Gateway.
Live today on Enterprise. See it in action 👇
Finn Lobsien retweeted
Every developer should understand the difference between static credentials, secret rotation, and dynamic secrets.
I made a quick explainer covering all three:
Finn Lobsien retweeted
Infisical now writes your secrets into your Spacelift contexts!
You choose an Infisical folder and the @spaceliftio context to write to. When a value changes in Infisical, Infisical updates the context, and every stack attached to it gets the new value on its next run, with support for environment variables or mounted files.
Available on all plans.
Finn Lobsien retweeted

searched up 'infisical alternatives' and got this
infisical.com/blog/infisical…
well played infisical. well played.
(you have to read the article to understand)

Finn Lobsien retweeted
New in Infisical: Post-Sync Commands for certificate management!
After a certificate is deployed through your Infisical Gateway, you can automatically run commands on the destination server, like reloading NGINX or binding the certificate to a port in IIS.
See it in action 👇
Finn Lobsien retweeted
Agent Proxy launched last week and it's the first commercial offering of its kind for brokering credentials to agents backed with so many rich features from our existing arsenal of secrets management features.
Highly worth checking out for anyone building agent infrastructure.
In this video @JakeHulberg walks through how you can use Agent proxy 🎉