

Full Scope Cybersecurity | Human Driven, AI Accelerated Pentesting | Continuous Monitoring | SOC2 Type II Audited
Joined December 2021
- Tweets2.1K
- Following87
- Followers3.3K
- Likes1.7K




Pinned Tweet
CredShields and @SolidityScan are proud to contribute to the release of the @owasp Smart Contract Top 10 2026.
OWASP Smart Contract Top 10 defines the primary contract-level failure patterns that repeatedly lead to loss in blockchain systems.
Sincere gratitude to @ethereumfndn Ecosystem Support Program for supporting the OWASP Smart Contract Security initiative.
owasp.org/www-project-smart-…

🚨 SECURITY ALERT
It has been historically brutal 48 hours for security teams.
From critical zero days in core internet architecture to supply chain attacks poisoning popular AI libraries, the threat landscape just shifted under our feet.
We’ve compiled the 6 major incidents you need to patch, rotate, and audit immediately.
Swipe through to see if your infrastructure is exposed. 👇
#Cybersecurity #Infosec #PatchNow #DevOps #ApplicationSecurity #ThreatIntel


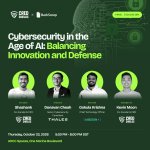
Cybersecurity in the Age of AI is happening tomorrow.
We’ll be taking a realistic look at how tech teams are managing AI innovation alongside defense risks.
Don't miss the conversation.
🗓️ Tomorrow, Oct 22
⏰ 5:30 PM - 8:00 PM SGT
📍 ARCC Spaces, One Marina Boulevard
luma.com/sn3z153m

We are excited to introduce @iam_Gokul , Fractional CTO at MISSION+, as part of our speaker and leadership lineup for our upcoming event co-hosted by CredShields × @BackScoopHQ! 🚀
Gokul is a hands-on engineering leader specializing in Enterprise AI, agentic systems, and AI platform engineering.
He leads the development of production grade AI solutions, his experience spans building and scaling AI products from 0→1, deploying solutions across enterprises and public sector organizations, and leading engineering teams to deliver measurable business impact.
Join us for an evening packed with actionable insights on modern AI engineering, velocity, and security:
📌 Topic: Cybersecurity in the Age of AI
📅 Date: Thursday, October 22, 2026
⏰ Time: 5:30 PM – 8:00 PM SGT
📍 Location: One Marina Boulevard
luma.com/sn3z153m

Reuters reported this week on a NorForge researcher who pointed AI agents at 1,200+ websites with almost no human direction. The agents got into more than 100. Each successful break-in cost about $50 in tokens and took around 23 hours.
Plenty of smaller sites got left alone because they weren't worth an attacker's time. At $50 a target, they are now. Worth checking what in your own stack is actually exploitable as often as you ship, using the same kind of agents. #AIsecurity
The full Reuters story on Snorre Fagerland's research at NorForge, from Oct 19: reuters.com/legal/government…

We are thrilled to welcome Donavan Cheah, Senior Cybersecurity Consultant at Thales, as a speaker for our upcoming event co-hosted by CredShields × @BackScoopHQ! 🚀
Donavan brings a decade of experience across penetration testing, threat modeling, security architecture, and product security.
As the security program lead for CloudFormity at Thales and author of "The AI-Cyber Loop: Essential Foundations for Business Leaders", he works at the exact intersection where artificial intelligence and cyber risk meet.
Join us as he shares practical insights on identifying security failures before attackers do:
📌 Topic: Cybersecurity in the Age of AI
📅 Date: Thursday, October 22, 2026
⏰ Time: 5:30 PM – 8:00 PM SGT
📍 Location: One Marina Boulevard
luma.com/sn3z153m

Two low-severity findings can be a key and the lock it opens. Testing them together is how you find out.
Does your current testing check findings in combination? #PenetrationTesting #AppSec
Read more : linkedin.com/feed/update/urn…

If you ship code daily, weekly, or even biweekly, an annual penetration test only covers a fraction of your releases.
Every release can change what an attacker can reach.
How much code has changed since your last security test?
@BackScoopHQ

Each false positive from a vulnerability scanner costs more than the hour it takes to close. It also spends a little of engineering's trust in the next security ticket, which may be the one that matters.
What share of last quarter's findings turned out to be real?
The full carousel, with four signs and what to do about each this quarter: lnkd.in/p/gGtfiWTX
An agent took a free account to premium on an app that uses Stripe, and no charge was settled. It traced what the upgrade step trusted as proof of payment, then carried a valid session reference into confirmation until it was accepted.
Read more here: lnkd.in/p/geQRAkyw
