

Husband, Father, Infosec @ SAS, Linux/Maker/Gadget/Automation guy. Views are my own and do not represent those of my employer. GPG KeyID 0x3DAECE84E841D6E3.
Raleigh, NC
Joined March 2007
- Tweets5.5K
- Following264
- Followers578
- Likes2.1K



Brian Wilson (@brianwilson@infosec.exchange) retweeted

I really recommending reading this.
In summary, a company which does ID verification for in-person interactions (hotels, car rentals, ID verification for alcohol or marijuana, etc) has some how exposed over 153,000,000 drivers licenses for people in the United States and Canada.
It is a catastrophic data breach, probably one of the worse I've ever seen. If you're in the United States and have traveled, gotten a hotel, purchased marijuana or alcohol, there is a high probability you're in this.
Unlike other breaches, this includes a photo of the person (from the license), making verification you've identified the person significantly easier.
This poses a significant threat to celebrities (musicians, YouTubers, streamers, adult entertainers, actors, etc), politicians, lawyers, wealthy people (CEOs, investors, people of public interest), Law Enforcement Officers, etc
Krebs himself, and several other security researchers, have already confirmed they're in the data leak.
tl;dr gah damn dawg this company is going to be sued into oblivion
krebsonsecurity.com/2026/09/…
From one Garnerian to another; when you got to go, you got to go. wral.com/news/local/garner-m… his tattoo is *chefs kiss* cc @woodyandwilcox

1
126
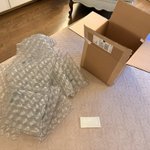
Ok @tilebar one of your shippers is trolling us or you only have one size shipping box. 14” squared box with 4lbs of postage and packing for a single subway tile? And it was free? We’ve had a good laugh but seriously?


1
46


I didn’t have “@Ticketmaster couldn’t get more sleazy” on my bingo card. Can’t login unless you agree to not join a class action lawsuit. I think I’ll pass and figure out how to join said lawsuit.

.@PaloAltoNtwks Can PA comment as to why support does not consider the copying a valid SAML token from one machine (that meets cond. access policy) to a 2nd (that doesn't), then using that token to login on 2nd device, would permit GlobalProtect to bypass cond. access policy.
141
Brian Wilson (@brianwilson@infosec.exchange) retweeted

@FBIDirectorKash @FBIDDBongino please have the bureau look into the murder of Giovanni Pelletier. #CrimeHasToBeStopped
change.org/p/justice-for-gio…
.@NC_QuickPass please tell your website team that not permitting copy/paste in password fields as well as limiting of special characters is unnecessary and counterproductive. Please help us normalize the use of password vaults and copy/paste and less restrictive rules are a must!
2
295
Oh my, @Egnyte. You only support password and explicitly do NOT support key-based authentication for SFTP? Seems like a significant gap for a file sharing service, unless I'm missing something. helpdesk.egnyte.com/hc/en-us…

2
325
Brian Wilson (@brianwilson@infosec.exchange) retweeted

This is a wild ride. Snowflake breached and scraped of over 400 companies data.
Ticketmaster and Santander leaks this week seem to be tied to this.
@vxunderground and @GossiTheDog putting out great content on it.


First print off the @BambulabGlobal A1 Mini using some 2 year old filament with a generic PLA profile. 16 minutes on the fastest speed. Only caveat is you will not be able to work at the same table if you plan on printing on the highest speed; it needs a seatbelt.


166
Only feature I'm excited about on IOS17 is the sharing of Airtags with up to 5 people. This also works with $7 non-Airtag "Find My" capable tags from Aliexpress.
152
And to think, there are people in this same camp that still want law enforcement to have a back door to encryption technology. What's the difference? xitter.cf/libertysafeinc/status/…


1
208
Uhh @ATT; but nice looking Phish. Looks like someone may have swiped email sending creds from @brevo_official? At least the URL was quickly blocked...


3
204

Genuinely interested in the thought process of our government when our accounting department gets an email from secureemail.federalreserve.c…. NOT a .gov. Why should we trust this and not think it's a phish? It sure looks like a good phish. @federalreserve @JenEasterly
1
102
